permissions

Winsage
September 24, 2026
Security researchers from Graz University of Technology in Austria have discovered significant vulnerabilities in the file notification systems of major operating systems: Android, Linux, macOS, and Windows. These flaws have existed for decades and can lead to the leakage of sensitive system information. The affected systems include inotify on Linux (since 2005), FileObserver on Android (since 2008), ReadDirectoryChangesW on Windows (since 2000), and FSEvents on macOS (since 2007). The vulnerabilities allow unprivileged users to monitor file events without explicit read permissions, enabling potential attacks such as inter-keystroke timing attacks and website fingerprinting. For example, on Linux, monitoring a readable directory can leak events on files that cannot be read, allowing attackers to achieve a 93.1% to 100% accuracy rate in monitoring keystrokes. Specific vulnerabilities include CVE-2025-68788 on Linux, which received a partial fix in December 2025, and issues on Android where FileObserver can bypass app storage isolation. On macOS, limited information is available due to a lack of bypasses for private directories, while on Windows, monitoring the root directory can reveal the full path of every accessed file, allowing real-time tracking of web activity with a 97.8% accuracy rate. Microsoft has described the issue as "by-design," which has faced criticism. The researchers propose stronger mitigations, such as disallowing monitoring of entire drives on Windows and introducing a permission system for file monitoring on Windows and macOS. Their findings will be presented at the ACM CCS 2026 conference in November in The Hague, Netherlands.

AppWizard
September 22, 2026
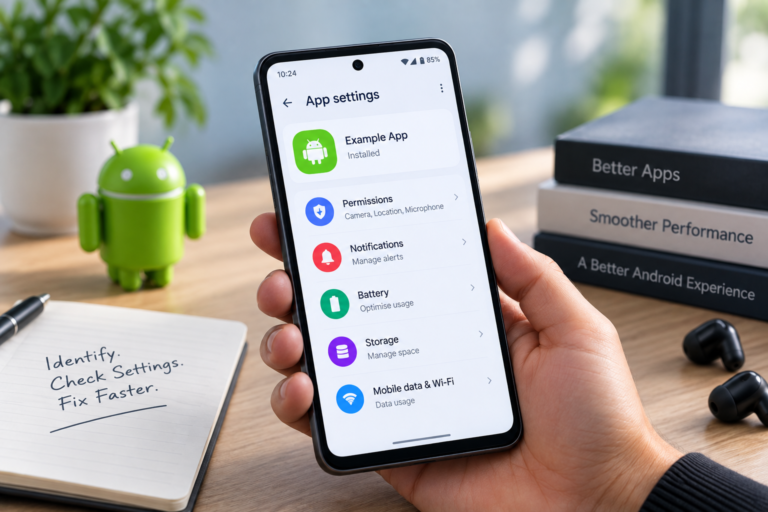
When an Android app encounters issues, the cause may be related to the device's settings rather than the app itself. Factors such as missing permissions, battery restrictions, or disabled notifications can affect app functionality. Users should check the specific feature that is failing, such as verifying microphone permission for voice messages or camera access for QR code scanners. Background restrictions can hinder apps that require background functionality, and different apps have varying background requirements. Notification settings should be inspected if alerts are absent, as these can differ by application and device. Storage space and cache management are important, with a recommendation to avoid clearing everything at once. If problems arise after installing an app from an untrusted source or if it requests excessive permissions, the app itself may be the issue. Android settings can vary between devices, so users may need to search for specific settings if guides do not match their device. Troubleshooting should be done one step at a time to identify the root cause of the issue.
AppWizard
September 22, 2026
Cybersecurity researchers at Zimperium have identified a new strain of malware called RatHat, targeting Android devices and linked to threat actors from China. RatHat uses generative AI to maintain persistence and control over infected devices. The malware is typically spread through social engineering, tricking users into downloading counterfeit applications that appear legitimate. Once installed, RatHat requests accessibility permissions, activates Wireless Debugging, and can capture text messages, create overlays, and steal passwords and multi-factor authentication codes. Its AI capabilities allow it to navigate the device interface in real-time, making detection by security software more difficult. To protect against RatHat, users should avoid downloading apps from untrustworthy sources, and removal requires a factory reset of the device.
Winsage
September 20, 2026
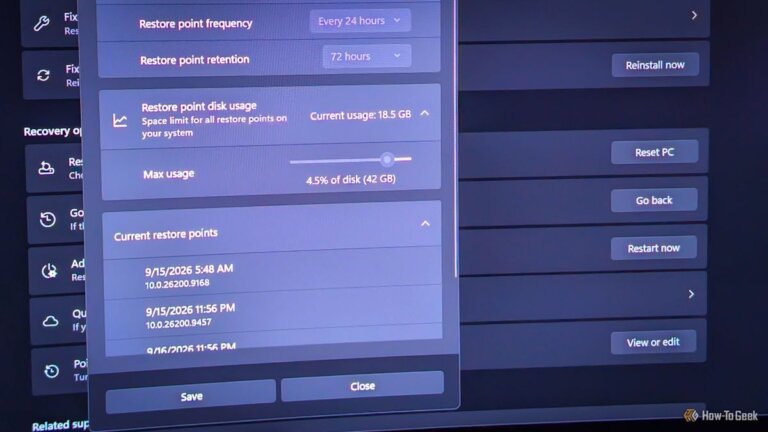
Microsoft introduced a feature called point-in-time restore in Windows 11, which creates snapshots of the system every 24 hours to enhance recovery options. This feature began rolling out in late June 2026 and is typically enabled by default for boot drives of 200GB or larger. It uses the Volume Shadow Copy Service to generate restore points that are available for 72 hours before being purged. The feature can consume significant storage space, initially occupying 3.9GB and potentially increasing to over 18GB within two months, reaching a maximum of 2% of the total disk space. Users can adjust the storage usage settings or disable the feature entirely to reclaim space. The default maximum usage can be modified to as low as 0.2%. There are concerns that this feature should have been opt-in rather than opt-out due to its storage implications.
Search