phishing emails

Winsage
September 24, 2026
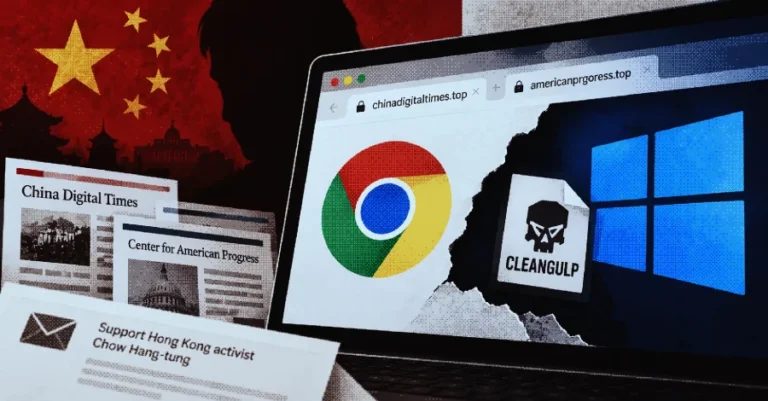
A Chinese threat actor, codenamed UTA0565, has exploited newly disclosed vulnerabilities in Google Chrome (CVE-2026-85046, CVE-2026-87491) and Windows (CVE-2026-85880) through deceptive websites, achieving remote code execution. The attacks were detected on September 3 and 4, 2026, and involved impersonating organizations to mislead victims, particularly targeting Asian government entities with phishing emails related to Hong Kong activist Chow Hang-tung. The phishing messages directed users to fraudulent sites that loaded an HTML element using the BlueMoon exploit kit, which delivered a payload named "chrome_cleanup.exe," associated with the CLEANGULP malware family. This malware allows for command execution, process listing, file uploads and downloads, and uses a hard-coded domain for command-and-control communications. The exploit's widespread use suggests a coordinated effort within the Chinese cyber espionage community, with indications that multiple groups are sharing and weaponizing the exploit.
Winsage
September 15, 2026
A spear-phishing campaign linked to the Chinese threat actor UTA0560 targeted various NGOs on September 1, 2026, exploiting recently patched vulnerabilities in Google Chrome and Microsoft Windows. The campaign utilized a malicious JavaScript backdoor called GRIMWEDGE, which was deployed through a multi-stage exploit chain that involved three vulnerabilities: CVE-2026-85046, CVE-2026-87491, and CVE-2026-85880. The attack began with spear-phishing emails that led recipients to a vulnerable U.S.-based university website, allowing attackers to redirect users to their infrastructure. The exploit chain enabled arbitrary code execution and facilitated the deployment of GRIMWEDGE, which is capable of host reconnaissance, file and process management, command execution, and payload delivery. The initial payload was an executable named "msgbox.exe," which extracted a legitimate Windows binary and a malicious DLL called "wsc.dll." This DLL initiated a sideloading chain and contacted a command-and-control server for further instructions. GRIMWEDGE allows for several commands, including system reconnaissance, directory listing, file deletion, and command execution in a hidden window. It lacks built-in persistence or lateral movement mechanisms but provides a foothold for further exploitation. Concurrently, another Chinese threat actor, JungleBamboo (APT31), used the same exploit chain to deploy a loader named SUPERSTOMP, which installs a credential-stealing Chrome extension called LONGTALE. The simultaneous use of the exploit chain by multiple actors suggests potential sharing or sale of the exploit, raising concerns about patch-gap vulnerabilities that pose risks for exploitation campaigns.
Winsage
September 9, 2026
Recent investigations have identified the BlueMoon exploit kit, used by espionage-driven threat activity clusters, particularly linked to APT31, a China-aligned state-sponsored group, since August 28, 2026. BlueMoon exploits three vulnerabilities: CVE-2026-85046 (a type confusion vulnerability in Google Chrome's V8 engine), an unassigned V8 sandbox escape, and CVE-2026-85880 (a heap-based buffer overflow in Windows ALPC). Google and Microsoft have released patches for these vulnerabilities, which were exploited as "patch-gap" zero-days. The attack vectors typically begin with phishing emails that lead victims to malicious URLs, triggering the vulnerabilities for code execution and privilege escalation. Variants of BlueMoon have been detected, featuring modifications for specific campaigns. Notable attack chains include: - APT31 targeting NGOs and mining firms in the U.S. with a malicious browser add-on called GemStone. - UNK_LateNight targeting U.S. aerospace companies, deploying BlueMoon alongside the ShadowPad backdoor. - UNK_DoubleCheck targeting a Vietnamese manufacturer, using DLL sideloading to execute a Rust binary. - UNK_QuietRacket targeting government and financial organizations in Indonesia and Singapore, modifying BlueMoon to execute a .NET assembly. CISA added the Chrome flaw to its Known Exploited Vulnerabilities catalog on September 4, 2026, requiring federal agencies to apply patches by September 18, 2026. Indicators of compromise include specific process trees, files, folders, scheduled tasks, mutexes, and registry keys. Proofpoint has released detection rules to help organizations identify and mitigate these threats.
Tech Optimizer
July 27, 2026
Shopping for antivirus software can be overwhelming due to technical jargon and extensive feature lists. Key considerations for effective antivirus software include: - Real-time protection: The software should continuously monitor activities and provide automatic protection against threats. - Malware and ransomware blocking: It should defend against various online threats, including malware, spyware, and ransomware. - Firewall protection: A firewall should monitor and block suspicious connections to enhance security. - Performance: The software should operate quietly in the background without interrupting daily tasks. - Frequent updates: Regular updates are essential to combat evolving online threats. - Scam protection: The software should flag suspicious links and messages to prevent cyberattacks before they reach the device. When choosing antivirus software, prioritize these features to ensure effective protection without complicating your life.
Tech Optimizer
July 25, 2026
A new remote access trojan (RAT) named msaRAT has been identified by Cisco Talos, linked to the Chaos ransomware group and built using Rust. It exploits Chrome and Edge browsers to disguise its traffic and evade detection. MsaRAT operates through a headless browser process, enabling remote code execution and facilitating ransomware deployment, data theft, and other malicious activities. It is typically installed via phishing emails or malicious files, making it resistant to standard browser patches. Cisco Talos recommends specific SNORT rules and a ClamAV signature for detection. Indicators of Compromise (IoC) include traffic to the IP address 172.86.126.18 and the domain is-01-ast.ols-img-12.workers.dev. The malware primarily targets large organizations, but individual users may also be at risk.
Tech Optimizer
July 10, 2026
Cybercriminals are exploiting the VLC media player to install ValleyRAT, a remote access trojan, by embedding malware in a seemingly harmless file linked in phishing emails. The attack starts with an email that prompts the victim to download a ZIP archive containing a fake VLC executable and a malicious DLL named libvlc.dll. This method uses DLL sideloading to execute the malware under the guise of a legitimate application. Once executed, the malware establishes persistence by creating a registry entry and connects to a remote server to retrieve the final payload. ValleyRAT employs evasion tactics to avoid detection, including assessing system characteristics before executing harmful actions and using a fileless approach to deliver the payload directly into memory. Researchers have identified indicators of compromise, including specific SHA1 hashes and URLs associated with the malicious campaign.
Tech Optimizer
July 3, 2026
Cybercriminals are using a sophisticated method to bypass security measures by embedding malware within the VLC media player. This campaign exploits VLC to install ValleyRAT, a remote access trojan, through phishing emails that contain links to download a seemingly harmless file. Once the file is opened, it activates a hidden backdoor that evades detection by antivirus solutions. The malware has been active since 2023, with a significant increase in activity noted through 2025 and into 2026, particularly targeting Chinese and Japanese-speaking users. The infection process begins when a victim clicks a link in a phishing email, leading to a ZIP archive containing a disguised executable and a malicious DLL (libvlc.dll). The executable mimics a legitimate VLC file, and when executed, it loads the DLL, allowing the malware to run under the guise of VLC. The malware establishes persistence by creating a registry entry and connects to a remote server to retrieve the final payload. ValleyRAT employs evasion tactics to avoid detection, such as performing checks on system behavior and using a fileless approach to inject its payload directly into memory, avoiding storage on disk. Researchers recommend training employees to recognize suspicious filenames and deploying endpoint detection tools to identify DLL sideloading behavior. For organizations affected by this campaign, isolating compromised systems and reviewing security logs are critical initial steps. Indicators of compromise include a malicious email domain, a ZIP archive containing a fake VLC executable, and a download URL for ValleyRAT.
Tech Optimizer
June 22, 2026
The author conducted an experiment by disabling both Bitdefender and Windows Security for a week to rely solely on personal cybersecurity instincts. They took precautions by using a secondary device and backing up important data. Throughout the week, the author experienced heightened awareness while navigating online tasks, encountered a phishing email, and adapted to a more deliberate browsing rhythm. Key takeaways included exercising caution, verifying sources, being aware of URLs, and keeping software updated. The experiment highlighted the importance of both good habits and antivirus software in maintaining cybersecurity. The author concluded that while personal vigilance is crucial, antivirus software is essential for those lacking strong instincts.
Search