phishing sites

AppWizard
September 18, 2026
Cybersecurity experts have identified a new Android malware named RatHat, believed to be operated by Chinese threat actors. RatHat is distributed primarily through smishing and malvertising campaigns, leading users to deceptive download portals. It employs an automated multi-stage infection process and exploits Accessibility features along with a local ADB self-pairing mechanism to escape the Android application sandbox. The malware uses various anti-analysis techniques, including container tampering, manifest bombs, DEX bytecode poisoning, and dual string-encryption. RatHat's architecture consists of a malicious Android application, a Go agent, and an FRP reverse-proxy client, which together enable it to gain critical system permissions and perform various malicious activities such as credential capturing, screen recording, and SMS interception. Even if uninstalled, the malware retains shell access to the device, allowing attackers to reinstall it. RatHat can serialize the device's Accessibility tree to XML and communicate with a Generative AI assistant for tasks like screen coordinate determination and text extraction. The Go Agent, masquerading as a native library, exploits shell access to execute commands and establish a persistent connection to a command-and-control server via the FRP client. The C2 server can issue extensive commands to collect sensitive information, including SMS messages, credentials, files, and keystrokes, and RatHat also features a hardware-level keylogger.
AppWizard
September 17, 2026
Security researchers at Zimperium have identified a new strain of Android malware called RatHat, which is linked to threat actors from China and is designed to steal sensitive credentials and banking information. RatHat infiltrates devices through phishing sites, malvertising, and SMS phishing (smishing), tricking users into downloading malicious Android package kits (APKs). The malware uses a dropper to activate its payload, which is hidden in encrypted assets, and employs techniques to bypass Android's security measures. RatHat consists of three main components: a malicious Android application, a Go agent (liblocal-service.so), and an FRP client (libmedia_codec.so). The app collects sensitive information such as banking credentials, notifications, 2FA codes, OTP keys, and screen inputs. It features a generative AI user interface-automation engine that communicates in Mandarin and can perform various tasks like determining screen coordinates and issuing navigation commands. The Go agent acts as a command-and-control executor, executing commands to bypass app-level security and manage system-level tasks. The FRP client maintains a secure reverse tunnel to the attacker's server, allowing ongoing remote access to the device. The architecture of RatHat demonstrates the inadequacy of traditional mobile security measures against such advanced threats.
Tech Optimizer
September 1, 2026
NordVPN's next-generation antivirus achieved a 94% detection rate for phishing threats in an evaluation by AV-Comparatives, tested against 250 active phishing URLs and recording zero false positives. The antivirus also demonstrated a 92% block rate in similar independent testing and ranked third overall in speed and malware protection behind Avast and Norton. It is included in NordVPN's Complete subscription tier and operates alongside the standard VPN tunnel to block trackers, ads, and malicious sites in real-time. Users are advised to maintain vigilance and practice strong digital hygiene, including scrutinizing URLs and enabling two-factor authentication for added security.
Tech Optimizer
August 30, 2026
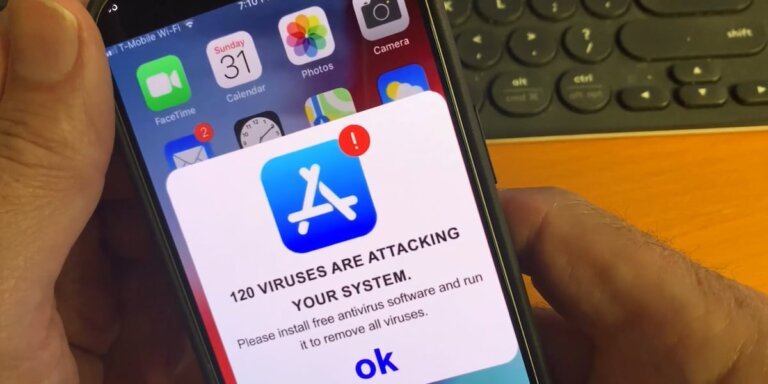
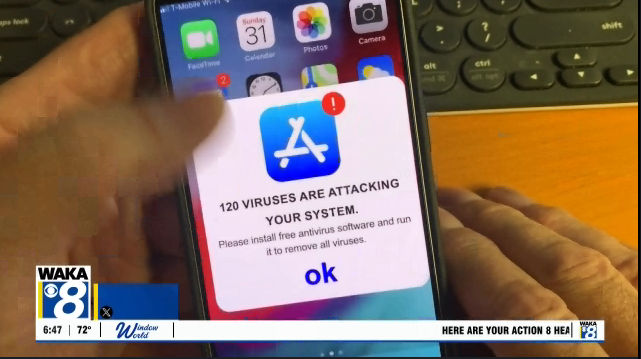
A viewer received a popup warning claiming her device had 120 viruses, which is a scam designed to prompt her to download a free antivirus app called "Total Cleaner." This alert is misleading and cannot scan the phone for viruses. The app has fake reviews, hidden costs, and privacy concerns, as it collects personal data. Most modern smartphones do not need traditional antivirus programs, and such popups are advertisements from free apps, misleading websites, or ad networks. To protect yourself, close the tab immediately, keep your device updated, and only download apps from official app stores after thorough research.
Tech Optimizer
August 29, 2026
A viewer reported receiving a popup on her smartphone claiming her system was infected with 120 viruses, which is a scam designed to provoke panic and encourage the download of a free antivirus app called “Total Cleaner.” This popup aims to trick users into downloading an app that may have hidden costs, initiate expensive subscriptions, or direct them to phishing sites. The app “Total Cleaner” has fake reviews, hidden costs after installation, and privacy concerns regarding personal data collection. Most modern smartphones do not require traditional antivirus programs, and such popups are advertisements from deceptive sources. To protect against these alerts, users should close the tab immediately, keep their devices updated, and only download apps from official app stores after thorough research.
Tech Optimizer
August 27, 2026
A viewer encountered a popup warning claiming her device was infected with 120 viruses, which is a scam designed to induce panic and prompt users to download a deceptive app called “Total Cleaner.” This app has fake reviews, hidden costs, and privacy concerns. Modern smartphones typically do not need traditional antivirus programs, and such popups are ads from free apps or misleading websites. To protect oneself, it is advised to close the browser tab immediately, keep the device updated, and only download apps from official app stores after thorough research.
Tech Optimizer
August 26, 2026
A viewer experienced a pop-up warning claiming her device had 120 viruses, which is a scam designed to promote a free antivirus app called “Total Cleaner.” The pop-up aims to incite panic and persuade users to download the app, which has hidden costs, fake reviews, and privacy concerns. Modern smartphones generally do not require traditional antivirus programs, and these pop-ups are advertisements that do not reflect the phone's security status. To protect against such alerts, users should close the tab immediately, keep their device updated, and be cautious with app downloads.
AppWizard
August 23, 2026
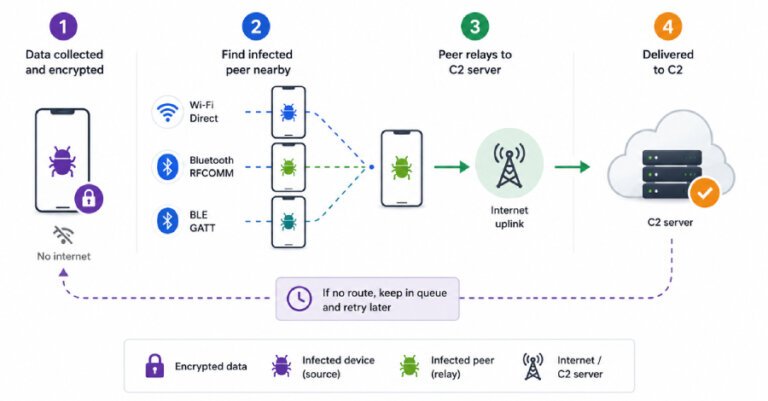
A new Android malware threat, codenamed Manic, poses significant risks to Ukrainian banks, government services, and messaging applications, with a reach extending to Russian and European financial institutions, global fintech platforms, cryptocurrency services, and military communication channels. Manic combines Android banking malware and mobile spyware, targeting sensitive applications and enabling comprehensive device takeover. It features a novel Wi-Fi mesh technique for data relay through compromised devices and utilizes phishing sites and dropper apps. The malware originated in February 2026, with initial development leading to its first deployment by late May. It monitors 169 package IDs related to banks, payment services, and messaging applications, primarily affecting Ukrainian targets but also impacting applications in Russia and Europe. Manic can infiltrate commercial and military messaging apps, track locations, monitor notifications, and collect files. It exploits Android's accessibility services to capture sensitive data and employs a store-and-forward relay mechanism for data exfiltration through nearby compromised devices. Google has stated that no apps containing this malware are found on Google Play, and Android users are protected by Google Play Protect.
Search