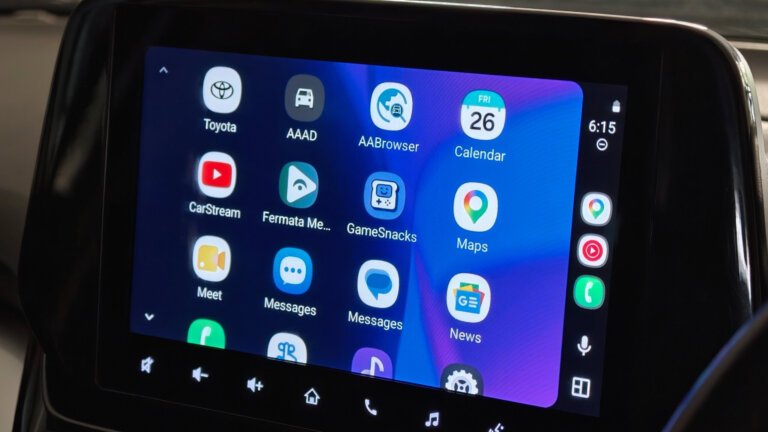
Google is preparing a full-screen GameSnacks experience for Android Auto by removing the navigation rail from both the GameSnacks menu and games themselves, making it consistent with other Android Auto games.
A small business is typically defined as one where the owner can personally name all employees, usually comprising a workforce of a few dozen. Licensing options for IT protection for small businesses vary, with Malwarebytes and Norton covering up to 20 devices, ESET offering plans for five to 25 devices, and Bitdefender providing options for three, five, ten, or 25 users. Avast and AVG allow licenses for one to 999 devices. All security suites support Windows, and most, except AVG, also support Mac devices. Four suites offer protection for Android and iOS devices, while Avast and AVG do not support mobile devices. Bitdefender, ESET, and Norton provide dedicated server editions, while Avast and AVG allow individual policy definitions for servers. Remote installation features vary in reliability, but all suites enable administrators to manage installations and monitor device status. Norton offers backup solutions and 500GB of shared hosted storage, while firewall protection is standard except for Malwarebytes. Bitdefender and ESET provide anti-theft systems for lost devices, and both ESET and Avast have measures against unauthorized device access. Malwarebytes and Norton offer 24/7 priority support, and Norton provides dark web monitoring for sensitive information.
A sophisticated PAYLOAD ransomware attack targeted an unnamed manufacturing organization in the Middle East, exploiting vulnerabilities in Microsoft Active Directory Group Policy. The attackers accessed the network through a compromised domain account via FortiGate SSL VPN on April 11, escalated privileges to domain administrator by April 13, and created a malicious Group Policy Object (GPO) named "PAYLOAD." This GPO was linked at the root of the domain, allowing it to affect nearly all domain-joined Windows workstations. The attackers distributed ransom notes, altered desktop images, displayed ransom messages at login, and disabled local administrator accounts. A second GPO, "win Firewall Off," was deployed to disable Windows Firewall across all profiles. The malicious policies activated on April 14 after systems were rebooted, causing widespread disruption. The attackers also exfiltrated data from file servers and published it on the dark web, while Kaspersky found no evidence of Windows file encryption or active malware processes. Recommendations for organizations include monitoring GPO creation, checking for unexpected changes, implementing multi-factor authentication for VPN access, and protecting privileged accounts.
A sophisticated PAYLOAD ransomware attack targeted a manufacturing organization in the Middle East, exploiting vulnerabilities in Microsoft Active Directory Group Policy. The attackers gained initial access on April 11 by compromising a domain account through the company's FortiGate SSL VPN. By April 13, they escalated privileges to a domain administrator and created a malicious Group Policy Object (GPO) named “PAYLOAD,” which was linked at the root of the domain. This GPO allowed them to distribute a ransom note, change desktop images, display a ransom message during login, and disable the local administrator account. A secondary GPO, “win Firewall Off,” was used to disable Windows Firewall across all profiles. The malicious changes activated on April 14 after system reboots, causing widespread disruption. The attackers also exfiltrated sensitive data, which was later released on the dark web. Kaspersky's investigation found no evidence of file encryption or active malware processes, indicating the attack was contained within Active Directory. Recommendations for organizations include monitoring GPO modifications, implementing multi-factor authentication for VPN access, and safeguarding privileged accounts.
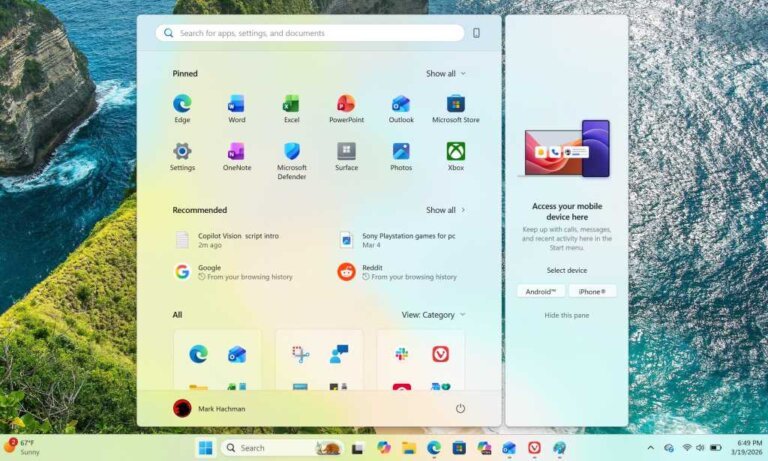
Administrators can manage taskbar settings in Windows by either freezing current configurations or restricting user modifications through the Registry or Group Policy. The Group Policy Editor is available in Windows Professional, Education, and Business editions. To lock down taskbar changes via the Registry, access the Registry Editor, navigate to HKEYCURRENTUSERSoftwareMicrosoftWindowsCurrentVersionPoliciesExplorer, create a new DWORD (32-bit) value named TaskbarLockAll, set its value to 1, and confirm. This will grey out certain options in the Taskbar settings. In the Group Policy Editor, navigate to User Configuration → Administrative Templates → Start Menu and Taskbar, enable "Lock all Taskbar Settings," and confirm. To prevent standard users from altering taskbar settings, navigate to HKEYCURRENTUSERSoftwarePoliciesMicrosoftWindowsExplorer in the Registry and create a new DWORD (32-bit) value.
Changing the desktop wallpaper to a solid color in Windows 7 caused a 30-second delay on the Welcome screen after entering a password. This issue arose because the system waited for a signal from the wallpaper component, which only sent its "I'm ready" signal when an image file was used. When a solid color was selected, this signal was not sent, leading to unnecessary waiting. The problem was acknowledged by Microsoft for both Windows 7 and Windows Server 2008 R2, and it was resolved with a Hotfix update in November 2009. Users found workarounds, such as switching to an image or creating a small solid-color image, to eliminate the delay.
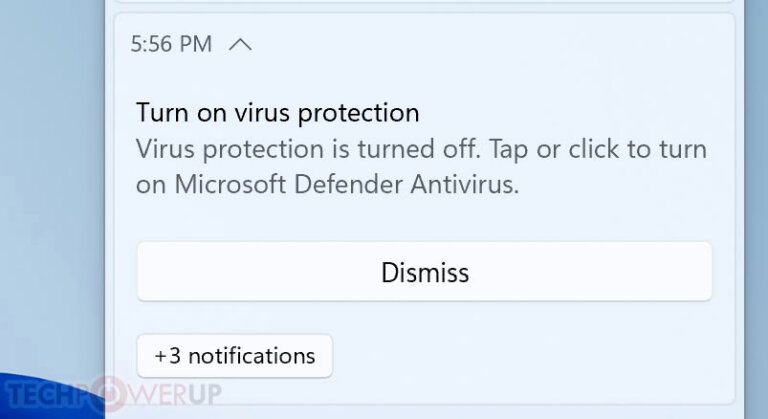
Microsoft resolved an issue in its Windows Security framework that incorrectly indicated Microsoft Defender Antivirus was disabled. This fix was implemented through Defender platform update 4.18.26080.4, released on September 17. The update installs automatically unless users have blocked mandatory security updates. Users had been receiving false alerts during system boot and intermittently afterward, which redirected them to the Windows Security home tab where settings appeared normal. Microsoft acknowledged the issue on August 28, affecting all supported versions of Windows and Windows Server with the latest Defender updates, but did not specify the triggering update. Users in the Windows Insider program reported similar warnings as early as June.
For nearly two months, Windows 11 users received persistent notifications from the Windows Security app falsely indicating that Microsoft Defender was disabled, despite it functioning properly. This issue, which began in early August, has been addressed with a security update from Microsoft. The false alerts affected all versions of Windows 11, Windows Server, and Windows 10, and were linked to a bug introduced with a recent Defender security update. Microsoft confirmed that no manual action is required from users to resolve the issue, as the fix will be automatically deployed to all PCs with mandatory security updates enabled. The problem was resolved in the Microsoft Defender Antivirus update (version 4.18.26080.4), released on September 17, 2026. Users can verify the status of Defender by checking Windows Security or using a PowerShell command.
Bitdefender Antivirus Free was upgraded to version 27.0.62.355 on September 11, 2026, introducing a new Advanced Threat Defense driver that enhances behavioral monitoring capabilities. The free version is designed for Windows only and promises to remain free indefinitely, lacking features found in paid versions such as anti-tracking tools and a full vulnerability scanner. The installation requires Windows 10 or 11, at least 2GB of free disk space, a local administrator account, an active internet connection, and a Bitdefender Central account. Users must remove any existing antivirus software before installation, and the installation process typically takes 60 to 75 minutes. Bitdefender Free covers one Windows device and offers robust malware detection capabilities, particularly with the Advanced Threat Defense layer. It is recommended to schedule regular scans and check the Notification Center for quarantined items. If uninstalled, the dedicated uninstall tool should be used to avoid leftovers that could interfere with future installations.
Users are experiencing freezing issues with web applications on PCs due to a bug in Microsoft Edge version 153, which causes windows to become unresponsive to mouse and keyboard inputs. Microsoft has acknowledged the problem and suggested reverting to version 152 as a temporary solution. To downgrade Microsoft Edge, users must disable updates through the Group Policy Editor, download the MSI file for version 152, and execute a rollback command in the Windows command prompt. After completing these steps, users can verify the version of Microsoft Edge to confirm the rollback.