protections

Tech Optimizer
September 19, 2026
For nearly two months, Windows 11 users received persistent notifications from the Windows Security app falsely indicating that Microsoft Defender was disabled, despite it functioning properly. This issue, which began in early August, has been addressed with a security update from Microsoft. The false alerts affected all versions of Windows 11, Windows Server, and Windows 10, and were linked to a bug introduced with a recent Defender security update. Microsoft confirmed that no manual action is required from users to resolve the issue, as the fix will be automatically deployed to all PCs with mandatory security updates enabled. The problem was resolved in the Microsoft Defender Antivirus update (version 4.18.26080.4), released on September 17, 2026. Users can verify the status of Defender by checking Windows Security or using a PowerShell command.
AppWizard
September 19, 2026
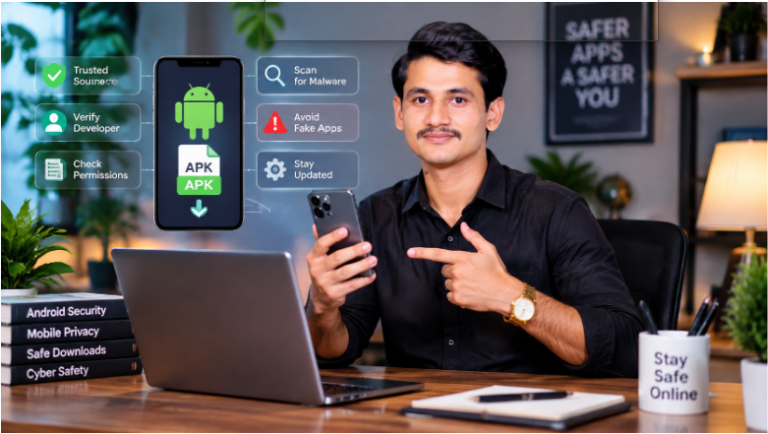
Security researchers have identified an Android banking Trojan named RatHat, which utilizes artificial intelligence, accessibility features, and Android Debug Bridge (ADB) to steal financial credentials, PINs, and one-time passcodes. Unlike traditional malware, RatHat employs a live AI assistant that interacts with the Android accessibility tree, allowing it to make real-time decisions based on the victim's screen content. The infection typically starts with social-engineering tactics, leading victims to counterfeit download pages where they are tricked into sideloading a malicious APK. Once installed, RatHat prompts users to enable Android Accessibility Service permissions, which it exploits to navigate Developer Options and enable Wireless Debugging. This grants it shell-level ADB access, allowing it to bypass application sandbox restrictions. RatHat deploys two native binaries for executing commands and maintaining a connection to the attacker's infrastructure. It targets banking applications through credential-stealing overlays and can intercept SMS messages for transaction verification codes. Additionally, it can record touch coordinates to reconstruct PINs and unlock patterns. RatHat includes persistence mechanisms to restore itself after removal, and users are advised to perform a factory reset if they suspect compromise. To reduce infection risk, users should avoid sideloading apps from unknown links, deny unnecessary Accessibility Service requests, and refrain from enabling Developer Options or Wireless Debugging for unfamiliar applications.
AppWizard
September 17, 2026
Security researchers at Zimperium have identified a new strain of Android malware called RatHat, which is linked to threat actors from China and is designed to steal sensitive credentials and banking information. RatHat infiltrates devices through phishing sites, malvertising, and SMS phishing (smishing), tricking users into downloading malicious Android package kits (APKs). The malware uses a dropper to activate its payload, which is hidden in encrypted assets, and employs techniques to bypass Android's security measures. RatHat consists of three main components: a malicious Android application, a Go agent (liblocal-service.so), and an FRP client (libmedia_codec.so). The app collects sensitive information such as banking credentials, notifications, 2FA codes, OTP keys, and screen inputs. It features a generative AI user interface-automation engine that communicates in Mandarin and can perform various tasks like determining screen coordinates and issuing navigation commands. The Go agent acts as a command-and-control executor, executing commands to bypass app-level security and manage system-level tasks. The FRP client maintains a secure reverse tunnel to the attacker's server, allowing ongoing remote access to the device. The architecture of RatHat demonstrates the inadequacy of traditional mobile security measures against such advanced threats.
AppWizard
September 16, 2026
Denuvo has filed a lawsuit against an individual known as "voices38" for allegedly tampering with and bypassing its anti-piracy technology, which is used in various popular PC games. The lawsuit was initiated in the U.S. Northern District Court of California, claiming violations of the Digital Millennium Copyright Act (DMCA). Denuvo describes voices38 as a "computer hacker" who has cracked numerous games, including titles like Doom: The Dark Ages and Hogwarts Legacy. Voices38 responded casually on Reddit, indicating a lack of concern for the lawsuit. Denuvo's business model relies on selling DRM solutions, and while it cannot sue for copyright infringement, it claims to be harmed by voices38's activities. The lawsuit lists several games that voices38 has allegedly cracked and marks Denuvo's first legal action against a video game pirate in the U.S. The company is also attempting to uncover voices38's true identity and may file subpoenas to gather more information. Public sentiment appears to be against Denuvo, with criticism regarding its software's impact on legitimate users.
AppWizard
September 16, 2026
A new feature called "expert mode" is being introduced to enhance the "Advanced Protection" framework for Android users, allowing them to toggle specific security features individually. Users will be able to manage six distinct items within the Advanced Protection suite: Intrusion logging, USB protection, Block auto-connection to unsecured Wi-Fi, Unknown apps, Spam filter, and Suspicious links in Google Messages. The "expert features" will not replace "Advanced Protection" but will provide users with the option to enable all protections at once or selectively activate specific features. While "Block auto-connection to unsecured Wi-Fi" will debut with "expert features," the inclusion of "Unknown apps," "Spam filter," and "Suspicious links in Google Messages" in the final version remains uncertain. The relevant resource for updates is the "Google Play services" app, version v26.36, released on September 15, 2026.
Tech Optimizer
September 16, 2026
Intego has reduced the price of its top-tier Mac security plan, the Intego ONE “Complete” plan, to half its usual cost during the back-to-school season. The plan, which covers one Mac and one iPhone, is now priced at .99 for a year, down from .99. A two-year subscription is available for .98, reduced from 9.99, equating to .74 per month. The promotion does not require a discount code, as the price is automatically applied at checkout, and it includes a 30-day money-back guarantee, valid until September 30. The “Complete” plan features Intego VPN and an iPhone app, providing comprehensive protection even when the laptop is not in use. The VPN encrypts internet traffic and conceals the user's IP address, while the iPhone app audits device settings and includes a Wi-Fi security check. Intego acknowledges that macOS has built-in security features and positions its antivirus as a complementary layer. The plan is particularly beneficial for users who travel frequently or connect to public Wi-Fi.
Winsage
September 15, 2026
Microsoft has released out-of-band updates for Windows 11 versions 26H1, 25H2, and 24H2 to address security vulnerabilities and improve system performance. The KB5129194 patch for version 26H1 fixes a critical elevation-of-privilege vulnerability (CVE-2026-62721) related to the Windows User-Mode Power Service (UMPS). The KB5129195 update for versions 25H2 and 24H2 also addresses a similar UMPS vulnerability and resolves a connection issue with Remote Desktop Services. Additionally, the updates fix problems with multichannel audio features on certain USB Audio Class 1.0 devices. These updates include enhancements from the September 2026 Patch Tuesday release, such as Taskbar customization, a faster Windows Search experience, and new Start Menu options. Users with unmanaged PCs will receive these updates automatically but can also check for updates manually.
Search