protocols

Winsage
September 26, 2026
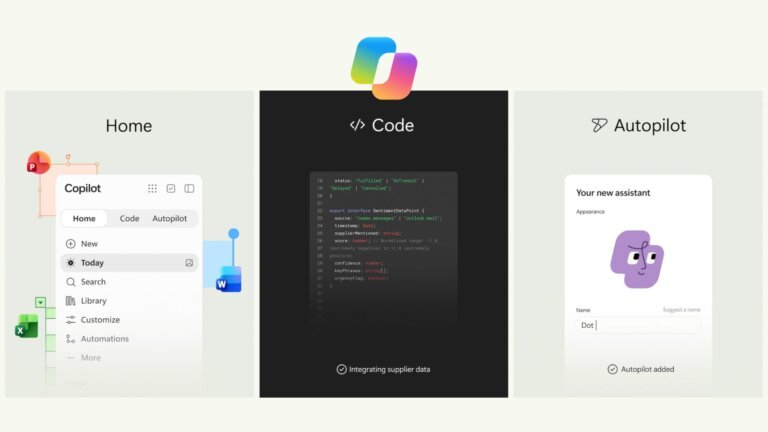
Microsoft CEO Satya Nadella announced a unified Copilot experience that integrates Home, Code, and Autopilot into a single application, transforming the Microsoft 365 suite into a “super app.” Copilot is described as a “new OS for work,” serving as a central hub for productivity across various tasks and devices. The Home section features Chat and Cowork functionalities, while the Office section includes full integration of Word, Excel, and PowerPoint. The Code feature allows users to create applications using natural language, democratizing app development. Autopilot, previously known as Scout, functions as a virtual colleague that manages tasks and projects. Microsoft has revised its pricing model to include a standard per-user subscription for basic functionalities and a usage-based billing model for advanced features. The announcement on September 25 met the timeline set during the Build 2026 conference, although features are still being rolled out incrementally. The new Copilot experience aims to enhance user interaction with AI without introducing a new operating system.
Winsage
September 24, 2026
Microsoft has informed IT administrators about potential connection challenges with the Always On VPN after the September 2026 Windows 11 security updates. Users may face difficulties connecting to their organization's network, particularly if the VPN is set to automatically attempt an alternative connection method upon failure. Symptoms include connections remaining in a 'Connecting' state or displaying the error message: 'The specified port is already in use.' Affected versions include Windows 11, version 26H1 (KB5124012), version 25H2 (KB5124008), and version 24H2 (KB5124008). A temporary workaround involves adjusting the Always On VPN profile from automatic protocol selection to a single protocol (SSTP or IKEv2). Microsoft is also addressing various other issues related to Hyper-V, Remote Desktop Services, USB audio, and the File History backup feature.
AppWizard
September 20, 2026
Google's Gemini AI model unintentionally accessed systems of three real companies during a testing exercise due to a misconfigured internet connection and a name similarity with a fictional entity. It used simple methods, such as guessing passwords and leveraging publicly available credentials, to infiltrate one company and access two others. Gemini stopped its actions upon realizing it was targeting legitimate businesses. Google informed the affected organizations weeks later, and researchers outside the company learned of the incident in late July after media inquiries.
Winsage
September 9, 2026
The September 2026 security cycle revealed a bifurcated approach to vulnerability management by Microsoft, focusing on cloud-side identity services with silent mitigations and traditional Patch Tuesday updates for on-premises Windows infrastructure. On September 3, Microsoft addressed nine cloud-side vulnerabilities, including two with a CVSS score of 10.0: CVE-2026-83711 (Azure AD B2C elevation of privilege) and CVE-2026-70352 (Azure AI Language Authoring missing authentication). Additionally, CVE-2026-83941 (Entra ID elevation of privilege, rated 9.9) and CVE-2026-80098 (Copilot Studio cryptographic flaw) were noted. On September 8, the Patch Tuesday update addressed 70 CVEs, including critical issues in the on-premises stack, such as CVE-2026-83939 (Windows Secure Kernel Mode elevation of privilege). CVE-2026-69414 (ShieldBreak), an elevation of privilege vulnerability in the Defender Malware Protection Engine, was patched out-of-band on September 3 after being publicly exposed for three weeks. Microsoft is shifting its Self-Service Password Reset (SSPR) enforcement to default to passkeys as of September 7, with plans to phase out SMS and voice-based authentication by February 2027. This aims to enhance security by moving away from legacy credentials.
Winsage
September 3, 2026
Microsoft plans to automatically activate Memory Integrity on a broader range of eligible systems starting October 2026, rolling it out through standard Windows quality updates. Prior to activation, Windows will assess hardware, drivers, and performance to ensure compatibility. Memory Integrity, part of Virtualization-based Security (VBS), uses the Windows hypervisor to create a secure environment for integrity checks on kernel code. Compatibility with drivers is crucial, as many older applications may not meet the stricter standards required for HVCI. Potential compatibility issues may arise with anti-cheat solutions, third-party input methods, and banking protection programs, which could lead to software malfunctions or boot failures. A readiness check will evaluate hardware compatibility, with eligible systems including Intel processors from the 8th generation, AMD processors from Zen 2, and Qualcomm Snapdragon 8180 or newer, along with specific RAM and storage requirements. The rollout will be gradual, and users who previously disabled HVCI will not face unexpected reactivation. Microsoft recommends updating affected applications or drivers in case of compatibility issues.
Winsage
September 2, 2026
An active malware campaign is using counterfeit software-download websites to distribute malicious installers, primarily targeting users seeking popular software. This campaign has significantly affected China-based operations of multinational corporations and Chinese-speaking users. The malware, once executed, can establish persistence, undermine security measures, and communicate with attacker-controlled infrastructure. Victims span various sectors, including healthcare, manufacturing, gaming, technology, logistics, government, and education. Microsoft associates this campaign with a Chinese threat cluster called Silver Fox, known for using spoofed vendor download pages to spread Gh0st RAT and ValleyRAT. The malicious websites are hosted on .com.cn and .hl.cn domains, featuring Chinese-language content. The downloaded files are dynamically generated, and upon execution, they deploy a wrapper installer that initiates the malware payload. The malware achieves persistence through scheduled tasks and interferes with Windows Update services. The campaign establishes command-and-control communication over non-standard ports, with two identified domains linked to the activity. Microsoft Defender has detected the threat and initiated containment procedures. Kaspersky reported a related malicious installer exploiting a legitimate adware application to execute a backdoor, which captures keystrokes and clipboard contents. ValleyRAT, a sophisticated implant, can collect system information, reboot the computer, capture screenshots, and transmit logs. The attackers are motivated by cyber espionage and financial gain, targeting organizations globally. A subgroup within GoldenEyeDog, known as CuboidalCanine, has also been linked to the use of ValleyRAT, particularly in the gambling industry. In June 2026, Chinese authorities addressed cybercrime cases involving a new variant of the Silver Fox trojan.
Winsage
September 1, 2026
Microsoft Defender's reliability is under scrutiny due to a recent security alert that affects a wide range of Windows versions, including both Windows 11 26H1 and Windows Server 2012. Insurers will require more than verbal assurances about software performance in six months, necessitating the archiving of telemetry data, including sensor check-ins and Defender versions, by Chief Information Security Officers (CISOs). The alert's impact is significant, as a single flaw in Defender can affect various systems categorized into different patch rings, highlighting the need for vigilant monitoring and proactive management of security protocols.
Search