proxy

AppWizard
October 9, 2026
Bitdefender researchers have identified a malware campaign called Midnight Mimosa that can be embedded in the software of low-cost Android devices before sale. This malware operates stealthily, allowing it to install and remove applications without user knowledge, generate fraudulent advertising activity, and convert devices into residential-proxy relay nodes for a botnet. It has been found on MediaTek-based, white-label devices marketed under misleading names. Users should be cautious of suspiciously cheap devices and look for signs of infection, such as unexplained ads, unfamiliar apps, sudden battery drain, and discrepancies in model names. Standard uninstallation or factory resets may not remove this malware, and users are advised to update their devices, review app lists, and contact sellers for refunds or replacements if they suspect infection. Mobile protection solutions can help monitor app behavior and alert users to potential threats.
AppWizard
October 1, 2026
In Android app development, maintaining connectivity, security, and debugging capabilities is crucial. When connecting to a London edge server, all requests must be visible to QA teams, but using a consumer VPN can hinder debugging proxies. A debugging proxy allows developers to inspect request headers and modify data by terminating TLS on their workstation. In contrast, a VPN creates an encrypted tunnel for all device traffic but prevents debugging proxies from intercepting packets. TorGuard is a hybrid solution that combines a VPN with SOCKS5 and V2Ray endpoints, allowing for traffic encryption and application-specific proxying. mitmproxy is an open-source tool that enables scripted request manipulation and can intercept various traffic types. Tailscale uses a WireGuard-based mesh network to provide stable private IPs for devices without needing port forwarding. HTTP Toolkit offers a rootless interception method for Android, directing traffic to a laptop without complex configurations. WireGuard is a high-speed self-hosted VPN that encrypts packets but does not allow for inspection. To inspect traffic while changing geographic egress, developers can run mitmproxy on a laptop and connect it to a VPN, ensuring the proxy is closest to the app. For debugging Android HTTPS traffic, a proxy is preferred for reading or rewriting requests, while a VPN is better for changing exit IPs or encrypted routing. SOCKS5 masks IP addresses but does not encrypt traffic.
AppWizard
September 30, 2026
Russian cybersecurity firm Positive Technologies has identified 11 security vulnerabilities affecting Android and Apple devices, with nine related to Apple and two to Android, classified as high severity. The Android vulnerabilities include one that allows attackers to exploit an NFC tag to execute an app without owner approval and another that lets installed apps modify network settings without additional permissions. Google has addressed these issues in its September 2026 security patches. For Apple, vulnerabilities include a macOS flaw that allows malicious apps to gain the highest system privileges and another that exposes sensitive information. Apple has released patches for these vulnerabilities, but specific OS versions affected have not been disclosed. Users are advised to ensure their devices have the latest security updates to mitigate risks.
AppWizard
September 27, 2026
F-Droid has released version 2.0 of its official Android app, marking the most substantial update in a decade after over a year of development and 14 test builds. The app has been reconstructed using Kotlin and Jetpack Compose, aligning it with Android’s Material Design principles and improving maintenance and feature expansion. Navigation is simplified into three sections: Discover, Search, and My Apps. The Discover section showcases new apps, updates, and popular downloads, while categories have been refined for easier access to specific software types. The search functionality has been enhanced to allow users to filter by application names, descriptions, categories, and languages. F-Droid 2.0 now automatically checks for and installs updates, with manual controls still available. Recent changes in the Android platform enable smoother installation experiences for alternative app stores. Privacy features have been updated, but the F-Droid Privileged Extension is not supported in this version, and the app-wiping capability has not returned.
AppWizard
September 25, 2026
Ocean Browser is an Android application that provides a secure and private browsing experience by integrating advanced proxy technology, eliminating the need for separate VPN applications. It reroutes browsing traffic through its secure infrastructure, hiding users' actual IP addresses from websites. Ocean Browser offers features such as encrypted proxy connections, the ability to select proxy locations, and seamless management of proxy connections without complex settings. It is designed for everyday use, particularly on public Wi-Fi networks, and is available for free on Google Play.
AppWizard
September 23, 2026
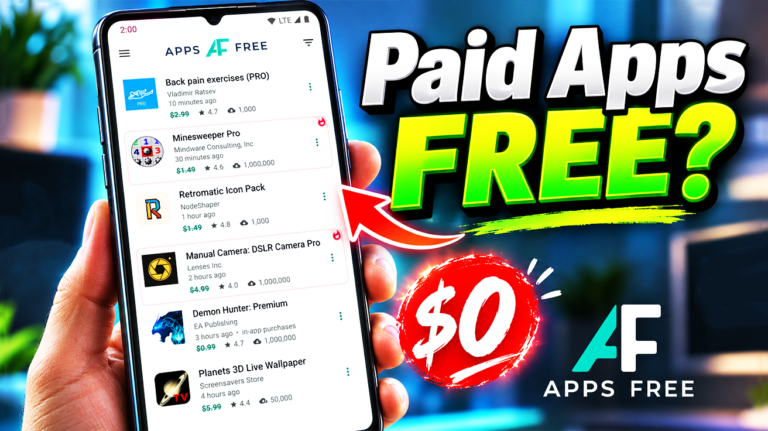
More than 70% of the world’s smartphones operate on the Android platform. Users often struggle to find apps that address specific issues, leading to a time-consuming search through numerous options. A curated list presents five applications that provide practical solutions to common mobile frustrations. 1. AppsFree: Monitors Google Play for premium apps, games, and wallpapers that temporarily drop to free, allowing users to snag deals that would otherwise be missed. Developed by ts-apps GmbH, it enables users to blacklist developers and filter low-quality offers. 2. Monocles Browser: Prioritizes user privacy by disabling JavaScript and cookies by default, reducing tracking. It has an APK size of approximately 13–14 MB and integrates ad blocking and supports Tor/Orbot proxy networks. Created by Arne-Brün Vogelsang, it offers a clean browsing experience. 3. Amarok: Allows users to instantly hide files and applications without resource-intensive encryption by obfuscating filenames and signatures. It supports multiple hiding modes and includes a “panic button” feature for quick data concealment. 4. Buckwheat: Budget manager: Requires manual input of total budget and days to cover, promoting financial reflection. It calculates daily spending allowances and provides detailed analytics. Developed by Danil Zakhvatkin, it has a user rating of around 4.6–4.7/5. 5. Chill Live Wallpaper: Offers minimalist landscapes that sync with local time and weather, providing a visually soothing experience. Compatible with Android 7.1+, it is ad-free and has a compact APK size of 5–6 MB.
AppWizard
September 19, 2026
A new Android malware called RatHat has emerged, analyzed by researchers from Zimperium's zLabs. It spreads through deceptive smishing texts and malicious ads that lead users to counterfeit download pages for popular apps. Once installed, it manipulates Android's Accessibility Service to gain elevated access by enabling Wireless Debugging and retrieving authentication codes without user intervention. RatHat targets finance and banking apps to steal user IDs, passwords, and MFA codes, using techniques to obtain touch coordinates for PIN recovery. It can intercept SMS messages, gain limited control of the device, and reinstall itself. Users are advised against sideloading apps and granting unnecessary accessibility permissions. Google's Advanced Protection Mode and Malwarebytes for Android can help mitigate risks associated with RatHat.
AppWizard
September 19, 2026
Security researchers have identified an Android banking Trojan named RatHat, which utilizes artificial intelligence, accessibility features, and Android Debug Bridge (ADB) to steal financial credentials, PINs, and one-time passcodes. Unlike traditional malware, RatHat employs a live AI assistant that interacts with the Android accessibility tree, allowing it to make real-time decisions based on the victim's screen content. The infection typically starts with social-engineering tactics, leading victims to counterfeit download pages where they are tricked into sideloading a malicious APK. Once installed, RatHat prompts users to enable Android Accessibility Service permissions, which it exploits to navigate Developer Options and enable Wireless Debugging. This grants it shell-level ADB access, allowing it to bypass application sandbox restrictions. RatHat deploys two native binaries for executing commands and maintaining a connection to the attacker's infrastructure. It targets banking applications through credential-stealing overlays and can intercept SMS messages for transaction verification codes. Additionally, it can record touch coordinates to reconstruct PINs and unlock patterns. RatHat includes persistence mechanisms to restore itself after removal, and users are advised to perform a factory reset if they suspect compromise. To reduce infection risk, users should avoid sideloading apps from unknown links, deny unnecessary Accessibility Service requests, and refrain from enabling Developer Options or Wireless Debugging for unfamiliar applications.
AppWizard
September 18, 2026
Cybersecurity experts have identified a new Android malware named RatHat, believed to be operated by Chinese threat actors. RatHat is distributed primarily through smishing and malvertising campaigns, leading users to deceptive download portals. It employs an automated multi-stage infection process and exploits Accessibility features along with a local ADB self-pairing mechanism to escape the Android application sandbox. The malware uses various anti-analysis techniques, including container tampering, manifest bombs, DEX bytecode poisoning, and dual string-encryption. RatHat's architecture consists of a malicious Android application, a Go agent, and an FRP reverse-proxy client, which together enable it to gain critical system permissions and perform various malicious activities such as credential capturing, screen recording, and SMS interception. Even if uninstalled, the malware retains shell access to the device, allowing attackers to reinstall it. RatHat can serialize the device's Accessibility tree to XML and communicate with a Generative AI assistant for tasks like screen coordinate determination and text extraction. The Go Agent, masquerading as a native library, exploits shell access to execute commands and establish a persistent connection to a command-and-control server via the FRP client. The C2 server can issue extensive commands to collect sensitive information, including SMS messages, credentials, files, and keystrokes, and RatHat also features a hardware-level keylogger.
Search