records

Winsage
September 28, 2026
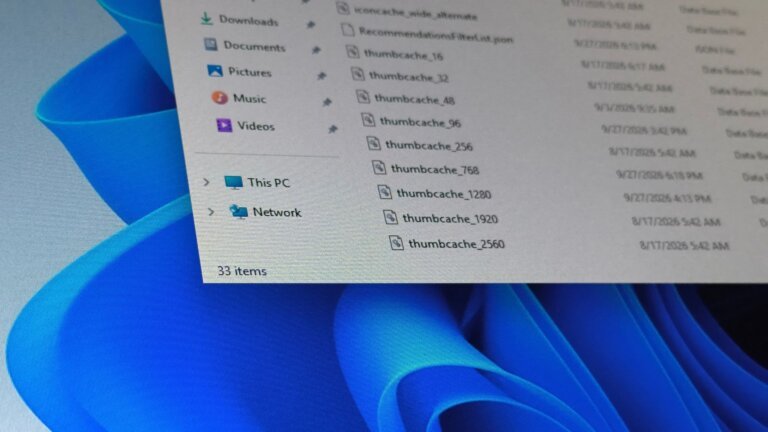
Windows retains thumbnails in a cache file named thumbcache_256.db, but it does not save a thumbnail of every deleted photo. Other operating systems, including macOS and Linux, also use thumbnail caching. Users can access their thumbnail cache by navigating to %LOCALAPPDATA%MicrosoftWindowsExplorer, but this will not show deleted images. Thumbnails are created only when images are displayed in Explorer’s thumbnail view. Windows allows users to clear the thumbnail cache using the Disk Cleanup tool, and there is an option to disable thumbnail caching in Windows 11 Pro and higher. The cached thumbnails do not guarantee persistence and do not represent original files. Windows also keeps records of application launches in Prefetch, maintains entries for USB devices in the USBSTOR registry key, saves Wi-Fi networks and passwords, and can keep clipboard history and recent file shortcuts.
Winsage
September 28, 2026
A recent post on X claims that Windows retains a thumbnail of every deleted photo in a file named thumbcache_256.db, which has raised privacy concerns among users. While Windows does maintain a thumbnail cache for efficiency, this practice is not unique to Windows, as other operating systems like macOS, Linux, and Android also use similar systems. Users can inspect or clear their thumbnail cache by accessing specific database files in the Windows Explorer directory. The claim that Windows retains "every photo you’ve ever deleted" is misleading, as thumbnails are only created when images are viewed in thumbnail mode. Windows does not cache every file, and thumbnails must exist before they can be cached. Additionally, Windows keeps app launch records in Prefetch files for performance optimization, maintains entries for USB devices in the USBSTOR registry key, retains records of Wi-Fi networks and passwords (which are encrypted), and can keep clipboard history and recent file shortcuts. Caching previews is common across various operating systems, and Microsoft is focused on user consent and privacy as it enhances Windows 11 with AI functionalities.
Tech Optimizer
September 28, 2026
Two newly identified Critical CVEs have expanded Microsoft's September identity infrastructure vulnerabilities to over ten verified weaknesses across more than ten distinct services. The Azure Database for PostgreSQL is vulnerable to CVE-2026-85878, an Improper Authorization flaw (CWE-285) with a CVSS score of 9.9. Azure Billing is impacted by CVE-2026-62874, which presents an Insufficient Data Authenticity Verification issue (CWE-345) with a CVSS score of 10.0. Both vulnerabilities were disclosed on September 18 and validated by Tenable and MITRE. CVE-2026-85878 allows an authorized attacker to elevate privileges over the network with minimal complexity, while CVE-2026-62874 requires no authentication, enabling unauthenticated attackers to jeopardize financial integrity. The vulnerability cluster first emerged during the Patch Tuesday cycles on September 3 and September 8, with initial reports highlighting critical flaws in core services. Other September disclosures include CVE-2026-83711 (Azure AD B2C, CVSS 10.0), CVE-2026-70352 (Azure AI Language, CVSS 10.0), CVE-2026-83941 (Entra ID, CVSS 9.9), CVE-2026-62916 (Entra ID, CVSS 9.1), CVE-2026-69857 (Azure Cosmos DB, CVSS 8.5), and CVE-2026-69854 (Spring Cloud Azure, CVSS 9.0). Activity heightened between September 17 and 18 with the introduction of CVE-2026-77903 (Microsoft Dataverse, CVSS 9.0) and CVE-2026-69843 (Microsoft Fabric, CVSS 10.0). The attack surface has broadened from authentication concerns to encompass trust in AI endpoints, data storage locations, and billing verification processes. Seven out of the ten vulnerabilities are unauthenticated, and all issues were addressed through server-side fixes by Microsoft. The extensive range of affected services suggests these vulnerabilities indicate a shared architectural dependency on authentication logic.
BetaBeacon
September 28, 2026
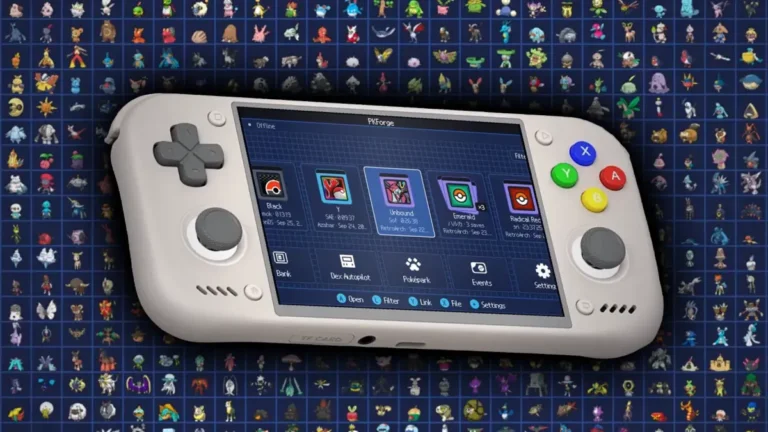
Main features of version 3.0 include managing Pokémon by editing various aspects, legalizing Pokémon offline, moving Pokémon between games, storing collections in a Bank, tracking the Pokédex, browsing and injecting events, editing the bag and trainer, using RNG tools, batch editing, breeding and hatching Pokémon, completing the Pokédex, playing with Pokémon in the Poképark, sharing teams, using game-specific editors, keeping saves safe, and supporting dual-screen devices. The software supports various generations of Pokémon games and emulators.
AppWizard
September 22, 2026
Cybersecurity researchers at Zimperium have identified a new strain of malware called RatHat, targeting Android devices and linked to threat actors from China. RatHat uses generative AI to maintain persistence and control over infected devices. The malware is typically spread through social engineering, tricking users into downloading counterfeit applications that appear legitimate. Once installed, RatHat requests accessibility permissions, activates Wireless Debugging, and can capture text messages, create overlays, and steal passwords and multi-factor authentication codes. Its AI capabilities allow it to navigate the device interface in real-time, making detection by security software more difficult. To protect against RatHat, users should avoid downloading apps from untrustworthy sources, and removal requires a factory reset of the device.
AppWizard
September 19, 2026
Researchers have found that Max, a messaging app mandated by the Russian government, can secretly capture screenshots, access sensitive information, impersonate users, and inject code into other applications. Developed by VK, the app integrates messaging, banking, and government services. Since September 1 of last year, it has been preinstalled on new smartphones, following the blocking of WhatsApp and Telegram. Despite its reach, it is not widely used in political circles, with insiders indicating that compliance with its use is performative.
AppWizard
September 19, 2026
To block a number on a Samsung Android phone, open the Contacts app, select the contact, tap More, choose Block contact, and confirm. Alternatively, in the Phone app, copy the number, tap More, select Settings, tap Block numbers, add the number, and tap the plus sign. To block a number from the Recents section, navigate to the number, tap Details, More Options, and Block number. For Pixel phones or stock Android, open the Phone app, tap More, select Call history, choose the call, and tap Block/report spam. To unblock a number on a Samsung device, open the Contacts app, select the contact, tap More options, and select Unblock contact. In the Phone app, tap More, select Settings, tap Block numbers, and tap the (-) next to the number. For Google Pixel and stock Android, open the Phone app, tap More, select Settings, tap Blocked numbers, and tap Clear (x) next to the number. Calls made during the blocking period will not appear in call logs.
AppWizard
September 19, 2026
ESG reporting standards are becoming increasingly important in mobile technology, affecting various aspects such as data management, material sourcing, energy consumption, privacy, supply chain dynamics, and product accountability. The lifecycle of mobile devices involves raw material sourcing, component manufacturing, device assembly, shipping, marketing, sales, updates, repairs, trade-ins, and disposal. Companies must understand ESG standards to create coherent sustainability narratives and may need to disclose supplier practices, carbon emissions, and governance documentation when partnering with larger firms. Consumers are now asking more questions about the longevity of software updates, repairability, data collection, packaging design, and the accountability of product creators. The rise of connected devices complicates ESG reporting due to extended product lifecycles and the need for ongoing software support. Companies should track product lifespan estimates, warranty data, repair trends, and update schedules to improve product quality and ESG reporting credibility. Emerging tech companies can start their ESG journey by cataloging product claims, consolidating evidence, designating ownership of records, and reviewing product lifecycle information. Global sustainability frameworks exist but may not align with consumer needs for straightforward product information. Successful mobile tech companies will need to bridge formal reporting requirements with accessible product-level communication. Trust and transparency in practices will increasingly influence consumer choices in mobile technology.
Search