The ACCC granted Google and Epic a six-year authorization covering Google Play service fees and rules governing alternative payment options inside Android apps sold in Australia.
Starting September 30, 2026, Google will implement changes to the Android game distribution economics through the Google Play Games Level Up program, reducing the commission on game revenue exceeding million annually from 20% to 15%. Developers must launch their games on Android simultaneously with other platforms to qualify for this discount; otherwise, they will be ineligible for six months. The new fee structure includes a baseline rate cut to 10% on the first million and 20% on earnings above that, while the Level Up program allows qualifying titles to pay 15% on revenue beyond the first million. The rollout of the Level Up program will begin in Australia, the European Economic Area, Japan, the United Kingdom, and the United States on September 30, 2026, followed by South Korea on December 31, 2026, and the rest of the world on September 30, 2027. If a game launches on a non-Android platform first, it will face a six-month waiting period before qualifying for Level Up pricing. Existing games launched before September 30, 2026, are exempt from this penalty.
The Russian Ministry of Digital Development has expressed concerns about Google's Android developer verification process starting in September 2026, which may hinder the accessibility of Russian applications on Android devices. Minister Maksut Shadaev noted that the verification checks could restrict users from freely installing mobile applications, posing challenges for developers already affected by removals from online marketplaces. Users may face a waiting period of up to 24 hours for certain installations. The potential exclusion of Russian applications from Android devices raises concerns about the future viability of local developers.
A nine-year-old boy named Mike created a YouTube channel called "Mighty Mike Plays" and, with his father's initial support, launched a modest advertising campaign. However, Mike independently escalated the budget to ,000 using his father's corporate credit card, resulting in significant charges. This led to his father, Dave, losing his job and facing financial difficulties. The situation has garnered over three million views online, but some skepticism exists regarding its authenticity, particularly due to Dave promoting merchandise instead of seeking direct financial help. The incident raises concerns about financial literacy among children and parents in the digital age, especially related to online spending and microtransactions in gaming.
Microsoft introduced a feature called Cloud Rebuild with the release of Build 26220.9343 to the Beta channel on September 8, 2026. This tool allows users to download a fresh installation of Windows 11 from the internet, restoring the operating system and its drivers without needing removable media. The recovery process is conducted through the Windows Recovery Environment (WinRE), and users can access it by booting into WinRE or through Settings. For Cloud Rebuild to work, a healthy WinRE, internet access, a compatible networking driver, and local administrator credentials are required. The feature also enables the storage of Wi-Fi profiles in WinRE, allowing wireless-only setups to utilize cloud recovery. Cloud Rebuild is compatible with enterprise management tools like Intune and Windows Autopilot, but it is currently only available to Beta channel Insider participants for non-production evaluation.
If you hold Microsoft 365 E5, you already have access to Microsoft Defender for Endpoint, which provides enterprise-grade endpoint protection at no additional cost. For organizations without a dedicated security specialist, Sophos is recommended. CrowdStrike is suitable for those with a mature Security Operations Center (SOC) and sufficient budget. Other options include SentinelOne for mid-sized organizations needing automation, ESET for older hardware and virtual desktops, Avast Business for very small businesses without IT staff, VIPRE for budget-conscious organizations, and Expel for tool-agnostic managed detection and response.
It is essential to assess your organization's current situation honestly when evaluating endpoint protection options. Antivirus and EDR are now essentially the same agent, and organizations should inquire about update staging processes and review independent tests for protection rates. Coverage for servers and Linux environments is often overlooked but crucial, as Linux servers are prime targets for ransomware.
Key recommendations include:
- Microsoft Defender for Endpoint for organizations already on Microsoft 365 E5.
- Sophos for organizations with 25-500 staff relying on IT generalists.
- CrowdStrike for enterprises with a well-funded security operations function.
- SentinelOne for mid-sized organizations needing autonomous operation.
- ESET for organizations with older hardware or virtual desktop infrastructure.
- Avast Business for micro and small businesses.
- VIPRE for budget-conscious organizations.
- Expel for those seeking managed detection across various environments.
During deployment, avoid running two real-time agents simultaneously, ensure prevention features are activated, and test on line-of-business applications first. Verify update staging and rollback procedures with vendors, and confirm whether Microsoft licensing covers your needs to avoid unnecessary purchases.
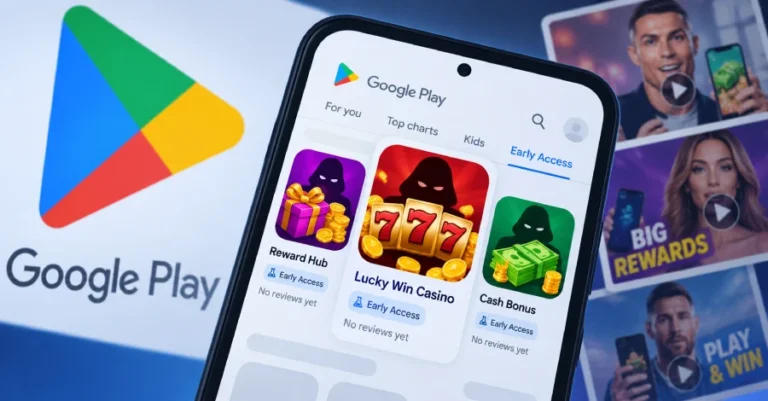
Bad actors are exploiting Google Play's Early Access program to distribute misleading applications that promise money, rewards, and casino winnings. This program allows developers to gather user feedback on unreleased apps but lacks public reviews or star ratings, enabling malicious actors to launch numerous fraudulent applications without immediate scrutiny. An example is the app "Vice Streets: Open World," which mimics Grand Theft Auto, has over 1 million downloads, and recently disappeared from the store without reviews or ratings. These deceptive apps are often promoted on social media with misleading advertisements and promise cash rewards, but users face obstacles when trying to withdraw their earnings. The primary goal of these apps is to generate revenue through excessive advertisements while circumventing regulatory requirements for legitimate gambling apps. Additionally, various malware families targeting Android devices have emerged, including Hagaseca, Mantax Otax, StreamRat, and GoldFactory's use of the Gigabud banking trojan, highlighting ongoing security threats in the digital landscape.
If you hold Microsoft 365 E5, you have access to Microsoft Defender for Endpoint, which provides enterprise-grade endpoint protection at no additional cost. For organizations without a dedicated security specialist, Sophos is recommended for its user-friendly platform. CrowdStrike is suggested for those with a mature Security Operations Center (SOC) and sufficient budget. Other options include SentinelOne for mid-sized organizations needing automation, ESET for older hardware and virtual desktops, Avast Business for very small businesses, VIPRE for budget-conscious mixed estates, and Expel for tool-agnostic managed detection and response.
Antivirus and EDR are now unified under a single agent, and organizations should inquire about update staging processes to avoid issues like those experienced in July 2024 with a major vendor's faulty content update. Independent tests from organizations like AV-Comparatives and AV-TEST are crucial for evaluating protection rates and false positives. Linux servers require attention as they are often targeted by ransomware.
When deploying endpoint protection, avoid running two real-time agents simultaneously, activate prevention features promptly, and test deployments on critical applications first. Organizations should confirm their Microsoft licensing covers necessary features and ensure there is a plan for responding to alerts. Common pitfalls include neglecting identity management and failing to test response workflows before incidents occur.
Apple provides built-in security features for macOS, including XProtect, Gatekeeper, and automatic malware removal, which contribute to the safety of Macs. However, these protections do not effectively address threats like infostealers, phishing, and adware. For enhanced security, third-party antivirus solutions are recommended.
Bitdefender is noted for its strong detection rates and minimal system impact, making it suitable for most users. Intego specializes in Mac-specific threats and is ideal for users focused solely on Apple products. ESET and Trend Micro are recommended for businesses needing centralized management. F-Secure is recognized for its privacy-focused approach, while Norton offers a comprehensive suite of security features. AVG provides free real-time protection suitable for low-risk personal use, but may not be adequate for business needs.
CleanMyMac is a maintenance tool rather than a traditional antivirus, focusing on system cleanup and optimization. Users should avoid running multiple real-time scanners simultaneously and ensure they purchase appropriate licenses for business use. It's important to evaluate the necessity of additional features and consider long-term pricing when selecting antivirus software.
- Book of Ra offers authentic Egyptian slot action with high-variance gameplay.
- Players can guess the color of the second playing card up to 5 times in a row.
- New icons in the game include a Pharaoh, Cleopatra, a Scarab, an archaeologist, and the Golden Book of Ra.
- The game has a simple bonus game where winnings can be wagered up to 5 times.
- The top payout is 500 times the bet in the base game.
- Book of Ra has a classic 5x3 layout with 10 paylines.
- The game has a Gamble Feature where players can double their winnings.
- The bonus round can result in wins up to 5,100,000 times the original stake.
- The game has a Scatter symbol, a Wild symbol, and a Bonus symbol.
- The game has a high RTP value of 92.13%.