Remote Access Trojan

AppWizard
September 11, 2026
The Cybersecurity and Infrastructure Security Agency (CISA) warned of a critical vulnerability in NetScaler, identified as CVE-2026-19490, with a CVSS score of 9.3, which has been exploited and affects all NetScaler ADC and Gateway appliances. Citrix has patched this vulnerability as of August 19. AdaptHealth reported a data breach affecting over 4.1 million individuals, compromising personal, health, and insurance information, but not Social Security numbers or financial data. A new strain of Android malware, MantaxOtax, attributed to Indonesian threat actors, combines ransomware and spyware, stealing sensitive information and affecting older Android versions. The Gigabud banking trojan has evolved to evade detection by installing a secondary app that hides the malicious application. CISA acting director Nick Andersen emphasized the need for swift adaptation to cybersecurity threats and highlighted staffing improvements within CISA. Russian e-commerce giant Wildberries experienced disruptions from a DDoS attack affecting payments to sellers, following claims of a cyber operation by Ukraine's military intelligence. McKesson faced a cyberattack exposing sensitive data of 6.4 million individuals, with the ShinyHunters group releasing this data after a failed extortion attempt. IDScan confirmed a data breach affecting 150 million individuals, resulting in the theft of personally identifiable information and government-issued documents.
AppWizard
September 10, 2026
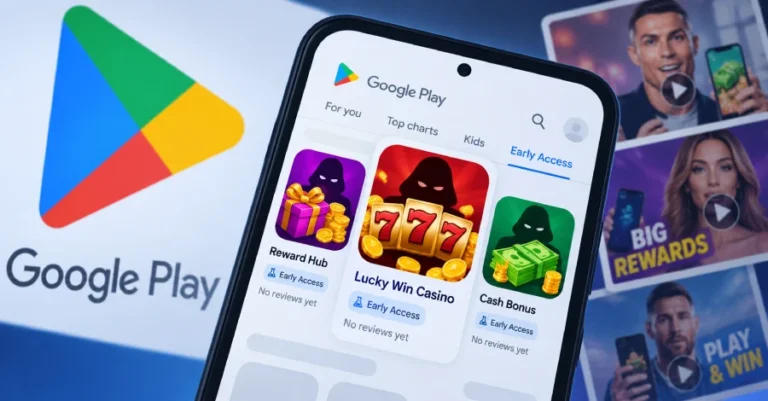
Bad actors are exploiting Google Play's Early Access program to distribute misleading applications that promise money, rewards, and casino winnings. This program allows developers to gather user feedback on unreleased apps but lacks public reviews or star ratings, enabling malicious actors to launch numerous fraudulent applications without immediate scrutiny. An example is the app "Vice Streets: Open World," which mimics Grand Theft Auto, has over 1 million downloads, and recently disappeared from the store without reviews or ratings. These deceptive apps are often promoted on social media with misleading advertisements and promise cash rewards, but users face obstacles when trying to withdraw their earnings. The primary goal of these apps is to generate revenue through excessive advertisements while circumventing regulatory requirements for legitimate gambling apps. Additionally, various malware families targeting Android devices have emerged, including Hagaseca, Mantax Otax, StreamRat, and GoldFactory's use of the Gigabud banking trojan, highlighting ongoing security threats in the digital landscape.
Tech Optimizer
July 25, 2026
A new remote access trojan (RAT) named msaRAT has been identified by Cisco Talos, linked to the Chaos ransomware group and built using Rust. It exploits Chrome and Edge browsers to disguise its traffic and evade detection. MsaRAT operates through a headless browser process, enabling remote code execution and facilitating ransomware deployment, data theft, and other malicious activities. It is typically installed via phishing emails or malicious files, making it resistant to standard browser patches. Cisco Talos recommends specific SNORT rules and a ClamAV signature for detection. Indicators of Compromise (IoC) include traffic to the IP address 172.86.126.18 and the domain is-01-ast.ols-img-12.workers.dev. The malware primarily targets large organizations, but individual users may also be at risk.
Tech Optimizer
July 18, 2026
North Korea's Contagious Interview hackers have been using a deceptive strategy to target developers by posing as recruiters and embedding malware in SVG files. Elastic Security Labs discovered that the attackers hid malicious payloads within HTML comment blocks of these files, allowing the malware to evade antivirus detection. At the time of the findings, no antivirus engines flagged the compromised repositories, which included trojanized GitHub repositories disguised as coding challenges. The malware executed automatically at server startup and deployed four modules: a browser credential and cryptocurrency wallet stealer, a file stealer, a remote access Trojan, and a clipboard monitor. The campaign, tracked as REF9403, is part of the ongoing Contagious Interview operation attributed to North Korea's Lazarus Group, which aims to generate revenue through cryptocurrency theft. Developers are advised to audit any projects run from unsolicited sources and to monitor specific domains associated with the attack.
Tech Optimizer
July 10, 2026
Cybercriminals are exploiting the VLC media player to install ValleyRAT, a remote access trojan, by embedding malware in a seemingly harmless file linked in phishing emails. The attack starts with an email that prompts the victim to download a ZIP archive containing a fake VLC executable and a malicious DLL named libvlc.dll. This method uses DLL sideloading to execute the malware under the guise of a legitimate application. Once executed, the malware establishes persistence by creating a registry entry and connects to a remote server to retrieve the final payload. ValleyRAT employs evasion tactics to avoid detection, including assessing system characteristics before executing harmful actions and using a fileless approach to deliver the payload directly into memory. Researchers have identified indicators of compromise, including specific SHA1 hashes and URLs associated with the malicious campaign.
Tech Optimizer
July 3, 2026
Cybercriminals are using a sophisticated method to bypass security measures by embedding malware within the VLC media player. This campaign exploits VLC to install ValleyRAT, a remote access trojan, through phishing emails that contain links to download a seemingly harmless file. Once the file is opened, it activates a hidden backdoor that evades detection by antivirus solutions. The malware has been active since 2023, with a significant increase in activity noted through 2025 and into 2026, particularly targeting Chinese and Japanese-speaking users. The infection process begins when a victim clicks a link in a phishing email, leading to a ZIP archive containing a disguised executable and a malicious DLL (libvlc.dll). The executable mimics a legitimate VLC file, and when executed, it loads the DLL, allowing the malware to run under the guise of VLC. The malware establishes persistence by creating a registry entry and connects to a remote server to retrieve the final payload. ValleyRAT employs evasion tactics to avoid detection, such as performing checks on system behavior and using a fileless approach to inject its payload directly into memory, avoiding storage on disk. Researchers recommend training employees to recognize suspicious filenames and deploying endpoint detection tools to identify DLL sideloading behavior. For organizations affected by this campaign, isolating compromised systems and reviewing security logs are critical initial steps. Indicators of compromise include a malicious email domain, a ZIP archive containing a fake VLC executable, and a download URL for ValleyRAT.
Search