remote access

AppWizard
September 17, 2026
Security researchers at Zimperium have identified a new strain of Android malware called RatHat, which is linked to threat actors from China and is designed to steal sensitive credentials and banking information. RatHat infiltrates devices through phishing sites, malvertising, and SMS phishing (smishing), tricking users into downloading malicious Android package kits (APKs). The malware uses a dropper to activate its payload, which is hidden in encrypted assets, and employs techniques to bypass Android's security measures. RatHat consists of three main components: a malicious Android application, a Go agent (liblocal-service.so), and an FRP client (libmedia_codec.so). The app collects sensitive information such as banking credentials, notifications, 2FA codes, OTP keys, and screen inputs. It features a generative AI user interface-automation engine that communicates in Mandarin and can perform various tasks like determining screen coordinates and issuing navigation commands. The Go agent acts as a command-and-control executor, executing commands to bypass app-level security and manage system-level tasks. The FRP client maintains a secure reverse tunnel to the attacker's server, allowing ongoing remote access to the device. The architecture of RatHat demonstrates the inadequacy of traditional mobile security measures against such advanced threats.
Winsage
September 14, 2026
Microsoft's recent security updates have caused disruptions in several areas: 1. Remote Desktop Services (RDS): Users on Windows 11 26H1 and Windows Server 2012 are experiencing connectivity issues, including failed connections, freezing servers, and unresponsive tools like Microsoft Management Console (MMC). A temporary solution involves restarting the virtual machine, and Microsoft is working on a fix. 2. USB Audio Devices: Problems have been reported with USB Audio Class 1.0 devices on Windows 11 26H1, 25H2, and 24H2, leading to audio issues. A workaround includes switching to two-channel mode, and Microsoft is addressing the situation. 3. Excel Functionality: A fix for vulnerabilities in Excel has disrupted the paste operation across versions 2016, 2019, 2021, and 2024, leaving users unable to paste content correctly. Some users have resolved the issue by uninstalling and reinstalling Office or using commands to remove the security update, though this also removes the associated security fixes.
Winsage
September 12, 2026
Windows 11 KB5124008, released on September 8, has caused various issues, including disruptions to WSL-based applications and Remote Desktop sessions. Users have reported problems with File History backups and instability in Explorer.exe, leading to system and GPU crashes. Microsoft confirmed a bug affecting applications using HCS-managed Linux virtual machines, particularly Claude Cowork, which is experiencing connectivity issues. Remote Desktop Services (RDS) are malfunctioning, leading to connection failures and sign-in problems. Additionally, some users face black screens upon sign-in due to Explorer.exe crashes. Reports indicate that File History is not recognizing external backup drives, and serious GPU issues have been reported on AMD Radeon systems, including driver timeouts and system freezes.
AppWizard
September 11, 2026
The Cybersecurity and Infrastructure Security Agency (CISA) warned of a critical vulnerability in NetScaler, identified as CVE-2026-19490, with a CVSS score of 9.3, which has been exploited and affects all NetScaler ADC and Gateway appliances. Citrix has patched this vulnerability as of August 19. AdaptHealth reported a data breach affecting over 4.1 million individuals, compromising personal, health, and insurance information, but not Social Security numbers or financial data. A new strain of Android malware, MantaxOtax, attributed to Indonesian threat actors, combines ransomware and spyware, stealing sensitive information and affecting older Android versions. The Gigabud banking trojan has evolved to evade detection by installing a secondary app that hides the malicious application. CISA acting director Nick Andersen emphasized the need for swift adaptation to cybersecurity threats and highlighted staffing improvements within CISA. Russian e-commerce giant Wildberries experienced disruptions from a DDoS attack affecting payments to sellers, following claims of a cyber operation by Ukraine's military intelligence. McKesson faced a cyberattack exposing sensitive data of 6.4 million individuals, with the ShinyHunters group releasing this data after a failed extortion attempt. IDScan confirmed a data breach affecting 150 million individuals, resulting in the theft of personally identifiable information and government-issued documents.
AppWizard
September 10, 2026
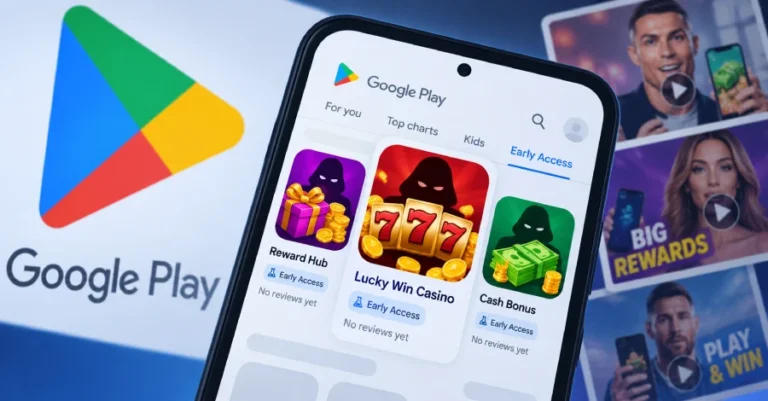
Bad actors are exploiting Google Play's Early Access program to distribute misleading applications that promise money, rewards, and casino winnings. This program allows developers to gather user feedback on unreleased apps but lacks public reviews or star ratings, enabling malicious actors to launch numerous fraudulent applications without immediate scrutiny. An example is the app "Vice Streets: Open World," which mimics Grand Theft Auto, has over 1 million downloads, and recently disappeared from the store without reviews or ratings. These deceptive apps are often promoted on social media with misleading advertisements and promise cash rewards, but users face obstacles when trying to withdraw their earnings. The primary goal of these apps is to generate revenue through excessive advertisements while circumventing regulatory requirements for legitimate gambling apps. Additionally, various malware families targeting Android devices have emerged, including Hagaseca, Mantax Otax, StreamRat, and GoldFactory's use of the Gigabud banking trojan, highlighting ongoing security threats in the digital landscape.
Search