Researcher

Winsage
September 17, 2026
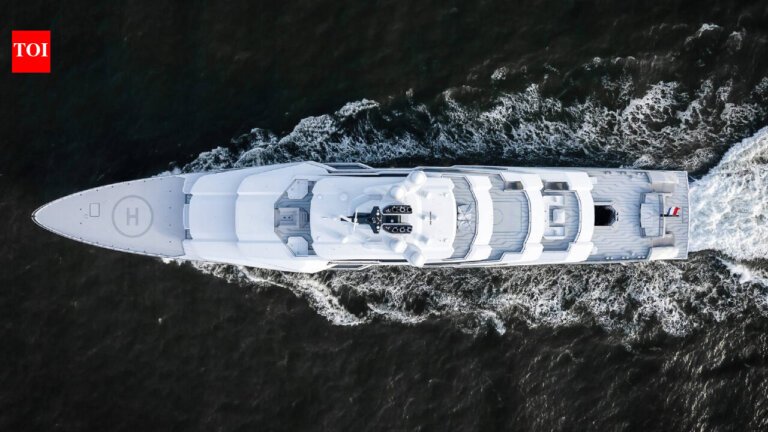
Gabe Newell, co-founder of Valve, created a custom-built superyacht named Leviathan, delivered by Oceanco. The 364-foot yacht features a glass wall etched with the names of nearly 3,000 contributors, honoring the collaborative effort behind its creation. Leviathan includes luxurious amenities like a 10-meter swimming pool and operates as a sophisticated oceanic base, equipped with a dive and scientific workstation, a laboratory, and 3D printing capabilities. The yacht also has an entertainment lounge optimized for holographic displays and a soundproof suite for music and video editing.
AppWizard
September 4, 2026
WhatsApp is rolling out a fix for a privacy vulnerability affecting Android users that could allow individuals with physical access to a locked device to view the owner's photos during a video call. The issue was identified by security researcher Jose Rodriguez, who demonstrated that an incoming WhatsApp video call could provide access from the lock-screen to the device's photo gallery without unlocking the phone. WhatsApp confirmed the implementation of a fix and noted that the issue is limited to situations where someone has physical access to the device. Rodriguez reported the vulnerability to both Meta and Google, receiving limited responses. Users are advised to update WhatsApp and adjust app permissions to enhance privacy.
Tech Optimizer
September 3, 2026
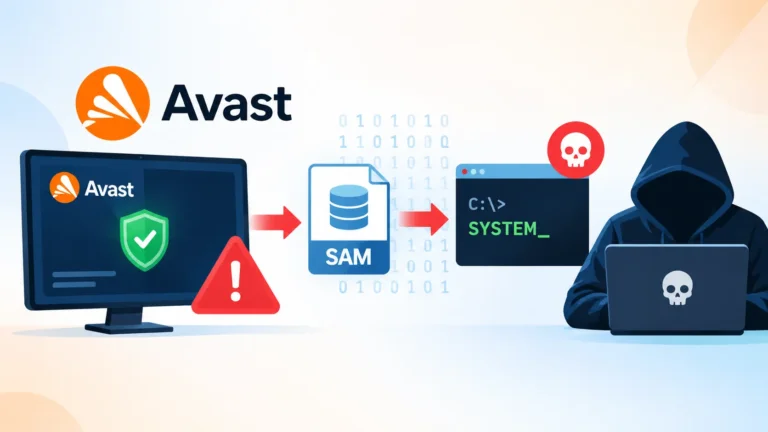
Nightmare Eclipse, a security researcher known for identifying vulnerabilities in Microsoft products, has shifted focus to other vendors, revealing a zero-day vulnerability called FalconFlank that targets CrowdStrike’s Falcon endpoint security platform. FalconFlank is a privilege escalation vulnerability that exploits the Microsoft Office malicious macros remediation feature within CrowdStrike Falcon. CrowdStrike is investigating the claims and advises customers to disable the Microsoft Office File Suspicious Macro Removal Windows policy setting while assuring them of continued protection through Cloud Anti-malware settings. The exploit works on fully updated Windows 11 25H2 and Windows Server 2025 systems running CrowdStrike Falcon with Optimal Protection enabled. Nightmare Eclipse has also discovered other vulnerabilities, including HardBreacher affecting Kaspersky’s endpoint antivirus and PrettyPrague in Gen Digital’s Avast antivirus, which allows attackers to dump the SAM database. Gen Digital is developing a patch for the Avast vulnerability, while Kaspersky has not commented. Additionally, Nightmare disclosed a memory corruption zero-day vulnerability in Nvidia, named GreenSection, which causes system crashes.
Winsage
September 2, 2026
An active malware campaign is using counterfeit software-download websites to distribute malicious installers, primarily targeting users seeking popular software. This campaign has significantly affected China-based operations of multinational corporations and Chinese-speaking users. The malware, once executed, can establish persistence, undermine security measures, and communicate with attacker-controlled infrastructure. Victims span various sectors, including healthcare, manufacturing, gaming, technology, logistics, government, and education. Microsoft associates this campaign with a Chinese threat cluster called Silver Fox, known for using spoofed vendor download pages to spread Gh0st RAT and ValleyRAT. The malicious websites are hosted on .com.cn and .hl.cn domains, featuring Chinese-language content. The downloaded files are dynamically generated, and upon execution, they deploy a wrapper installer that initiates the malware payload. The malware achieves persistence through scheduled tasks and interferes with Windows Update services. The campaign establishes command-and-control communication over non-standard ports, with two identified domains linked to the activity. Microsoft Defender has detected the threat and initiated containment procedures. Kaspersky reported a related malicious installer exploiting a legitimate adware application to execute a backdoor, which captures keystrokes and clipboard contents. ValleyRAT, a sophisticated implant, can collect system information, reboot the computer, capture screenshots, and transmit logs. The attackers are motivated by cyber espionage and financial gain, targeting organizations globally. A subgroup within GoldenEyeDog, known as CuboidalCanine, has also been linked to the use of ValleyRAT, particularly in the gambling industry. In June 2026, Chinese authorities addressed cybercrime cases involving a new variant of the Silver Fox trojan.
Winsage
August 27, 2026
Researcher Dominik Reichel has identified a new malware implant called SLEEPWALKER, which is disguised as an agent from ESET. SLEEPWALKER is unique because it does not contain malicious code and remains dormant until it receives specific network signals to activate. It appears to be designed for targeted attacks, likely orchestrated by nation-states. Although it was submitted to VirusTotal last year, it has not been linked to any active campaigns or confirmed victims. The origins of SLEEPWALKER are unknown, and its code is described as somewhat "rough around the edges," indicating it may still be in development.
Search