Safe Mode

Tech Optimizer
September 22, 2026
LastPass has identified a sophisticated scheme targeting users of its Authenticator app, involving SEO poisoning and deceptive GitHub pages that distribute malicious ZIP files disguised as legitimate software. Users searching for "LastPass Authenticator download" may encounter these counterfeit pages, which redirect them to a malicious server delivering a ZIP file containing vsdbg.exe and vsdbg.dll. The executable is a legitimate Microsoft debugging tool exploited to execute the malicious DLL through DLL sideloading, allowing the malware to run undetected. Named Rapuncel by security researchers from Delphos, this malware is undetectable by antivirus engines and targets a hardcoded list of 145 antivirus and endpoint security products, disabling them upon detection. Rapuncel harvests sensitive information, including saved passwords from over 25 web browsers, cryptocurrency wallet files from more than 30 applications, and session tokens from platforms like Discord and Steam. It also captures screenshots and compiles a profile of the infected system, uploading the stolen data to an attacker-controlled server. The malware includes a kernel driver that intercepts web traffic, allowing for advertisement injection and search result manipulation. This campaign has been active for several months, with LastPass vaults remaining unaffected. Users are advised to download applications only from trusted sources. Rapuncel establishes persistence on infected machines by installing itself as a Windows service that starts with the system and terminates activated security products. Removing the kernel driver requires booting into Safe Mode or using external recovery tools, as standard Windows utilities cannot eliminate software operating at that level.
Winsage
September 7, 2026
Microsoft is facing significant security and reliability issues, particularly related to system startup, BitLocker recovery, and updating Secure Boot certificates. Users have expressed confusion over these complexities, especially regarding Microsoft Defender Antivirus errors. These problems stem from a tumultuous period before the launch of Windows 11, including changes to the TPM requirement and the extension of Windows 10's life. Despite increased security patches, underlying issues remain, leading to user skepticism about the reliability of Windows systems.
AppWizard
September 3, 2026
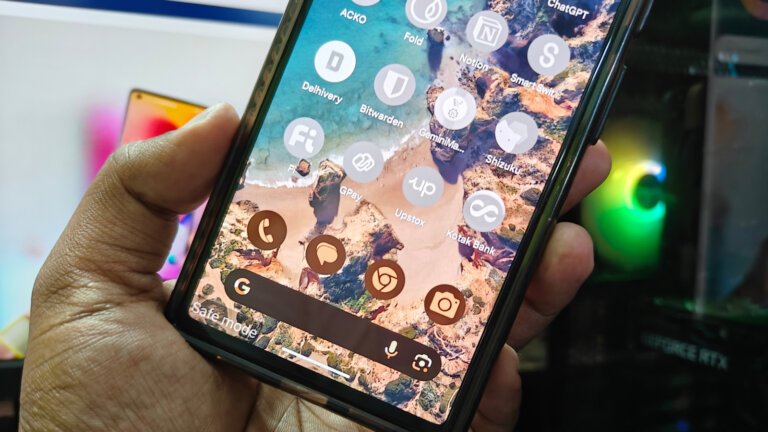
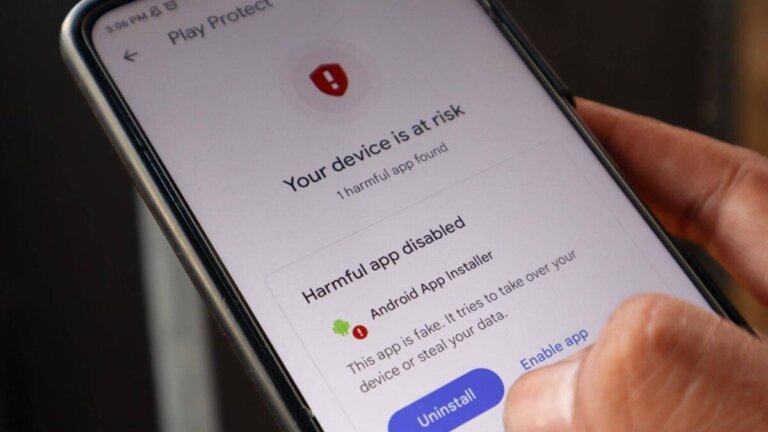
Safe Mode on Android disables all third-party applications and engages Airplane Mode to help troubleshoot device issues. It can be activated by holding down the Power Off button and selecting the Safe Mode option, which may lead to unintentional activation. To disable Safe Mode, users can either restart the device or tap the notification in the Notification Menu indicating Safe Mode is active. After exiting Safe Mode, Airplane Mode may remain active, which can be turned off through the Quick Settings menu. Google Play Protect also provides additional security measures that may cause user frustration.
AppWizard
September 1, 2026
Cybercriminals are targeting Android users with deceptive advertisements for malicious applications disguised as pornographic content on platforms like Facebook and Instagram. The National Cybercrime Threat Analytics Unit (NCTAU) has reported that these ads lead users to phishing traps or malware downloads that can compromise banking credentials. Malicious applications linked to this threat include “Night Play,” “Reloop,” “Kyss,” “Vimo,” “Rivo,” “Nexo,” and “Vixa.” The scam involves promoting these apps through enticing ads, redirecting users to websites offering pornographic content, and prompting them to download APK files directly from these sites, often using “.live” domains. The initial app may request users to download a second package disguised as an update, which can exploit permissions granted to the first app. This malware can gain extensive control over the device, potentially installing a VPN that routes internet traffic through attackers' servers. To protect against this threat, users should download apps only from trusted sources, avoid installing APK files from ads or suspicious links, refrain from granting Accessibility access to unknown apps, regularly review installed apps, keep Google Play Protect enabled, and monitor bank accounts for unusual activity. If a suspicious app cannot be uninstalled, users can try Safe Mode, remove special permissions, or perform a factory reset as a last resort.
AppWizard
August 31, 2026
India's cybercrime authorities have warned about the misuse of dating and adult-themed advertisements on social media platforms like Instagram and Facebook, which are being exploited by criminals to distribute malicious Android applications. These ads redirect users to external websites where they are prompted to download APK files, bypassing security measures of trusted app stores. The Indian Cybercrime Coordination Centre (I4C) has identified several malicious applications, including Night Play, Reloop, Kyss, Vimo, Rivo, Nexo, and Vixa, and cautions against installing unfamiliar applications promoted through unsolicited ads. These apps may request sensitive permissions, such as access to SMS messages, contacts, photos, device storage, and Accessibility Services, which can allow fraudsters to access valuable information. Compromised devices can lead to financial fraud by intercepting OTPs and other verification details. The I4C recommends using trusted app stores, keeping Google Play Protect active, reviewing app permissions, and being cautious with social media ads. If a suspicious app is installed, users should restart their phone in Safe Mode to uninstall it, disable its permissions if necessary, and consider a factory reset if removal fails. Users who suspect fraud are encouraged to report incidents promptly.
Search