scan

Winsage
September 22, 2026
Recent investigations have shown that a specific update to Microsoft Defender has caused performance issues for VLC Media Player, particularly a slowdown in startup times. Jean-Baptiste Kempf, a VideoLAN developer, attributed this sluggishness to a bug in the Microsoft Defender update, which quarantined VLC's plug-in cache. The problematic Defender signature update is version 1.455.50.0, linked to Windows Update KB5121003 released on August 11th. Users can reset the plug-in cache to improve performance by either reinstalling VLC or using the built-in functionality to regenerate the cache with vlc-cache-gen.exe. Alternatively, users can reset preferences and cache files by searching for "VLC" and selecting the reset option. Microsoft has not yet provided a fix for these issues, and users may need to set an exclusion in Microsoft Defender for VLC Media Player to prevent unnecessary scans, enhancing its performance.
Tech Optimizer
September 21, 2026
The landscape of computer security has changed significantly over the past two decades. In 2026, antivirus protection remains important, but the need for separate third-party programs has decreased for many users due to the built-in Microsoft Defender in Windows 11, which is activated by default and effectively blocks 100% of common malware samples according to independent testing by AV-TEST. Windows 11 also includes additional protective features like SmartScreen and a robust Firewall. While dedicated security suites from companies like Norton and Bitdefender offer advanced functionalities, many users may find adequate protection with the built-in tools. Research from AV-Comparatives indicates that performance varies among security programs, particularly against real-world attacks. Phishing attacks accounted for approximately 60% of initial access points in incidents examined by the ENISA Threat Landscape report from 2025, highlighting that user behavior is a significant vulnerability. Modern web browsers and operating systems have enhanced their security measures, with Google Chrome, Microsoft Edge, macOS, and Android incorporating features to protect users from harmful websites and downloads. For the average Windows 11 user who keeps their system updated and practices safe browsing, built-in protection is generally sufficient, though paid antivirus options can provide additional tools.
Tech Optimizer
September 21, 2026
More than 5,400 websites across over 2,200 organizations have been compromised to propagate malware, primarily affecting small businesses like clinics and online retailers. The attack mechanism involves malicious code that triggers a deceptive CAPTCHA, instructing users to execute commands that can download malware. Attackers are using the BNB Smart Chain test network to store instructions, making it harder for investigators to shut down operations. A newer variant of the attack uses WebRTC technology to establish encrypted connections for delivering additional malicious code. To protect against these threats, users should avoid pasting commands from websites, be suspicious of unusual CAPTCHA instructions, use strong antivirus protection, keep systems updated, take action if commands are executed, and small business owners should regularly verify their website's integrity.
Tech Optimizer
September 19, 2026
For nearly two months, Windows 11 users received persistent notifications from the Windows Security app falsely indicating that Microsoft Defender was disabled, despite it functioning properly. This issue, which began in early August, has been addressed with a security update from Microsoft. The false alerts affected all versions of Windows 11, Windows Server, and Windows 10, and were linked to a bug introduced with a recent Defender security update. Microsoft confirmed that no manual action is required from users to resolve the issue, as the fix will be automatically deployed to all PCs with mandatory security updates enabled. The problem was resolved in the Microsoft Defender Antivirus update (version 4.18.26080.4), released on September 17, 2026. Users can verify the status of Defender by checking Windows Security or using a PowerShell command.
Tech Optimizer
September 16, 2026
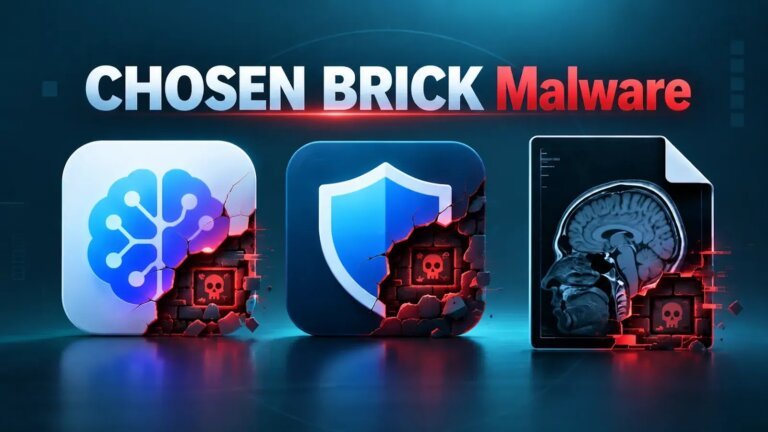
Iranian state-affiliated cyber actors are targeting dissidents, activists, and journalists using fake AI applications, counterfeit antivirus tools, and fabricated MRI scan results, primarily through a spyware family known as CHOSEN BRICK, which is designed for Windows systems. This campaign has been active since at least 2025 and affects individuals globally, including in the UK, US, and Netherlands. The malware establishes persistence via the Windows Registry Run key and communicates through Telegram, utilizing unique Bot IDs for each victim. CHOSEN BRICK is capable of extensive data collection, including capturing screenshots, recording audio, and stealing email content. Personal information from victims has been found on pro-Iranian leak sites, increasing harassment risks. Security measures should include monitoring for suspicious Registry entries and unusual communications, while users are advised to avoid unsolicited software installations and keep their systems updated. The FBI refers to this malware family as HEAVYGRAM.
Search