security controls

Winsage
October 5, 2026
Microsoft is enhancing Intune and Configuration Manager to support the transition to Windows 11 version 26H2 for enterprise administrators. Intune now offers day zero support for Windows 11 version 26H2 settings, allowing IT administrators to configure new Windows policies through the Intune admin center. An updated security baseline for Windows 11 version 26H2 will also be released. Configuration Manager versions 2603 and 2609 support Windows 11 version 26H2, providing platform enhancements and updated security controls. IT teams are advised to review new settings, test on representative devices, ensure OS compatibility, and monitor deployments. Organizations using Configuration Manager may need to upgrade their environments and address the discontinuation of support for older platforms like Windows Server 2012/2012 R2 and SQL Server 2016.
Winsage
September 30, 2026
WSL has introduced a new feature called WSL containers, enabling users to build, run, and deploy Linux containers on Windows. Users can access this feature by executing wsl --update or downloading the latest release from GitHub. Key capabilities include: - WSL containers CLI (PLACEHOLDER8a7e9b6f37799ba2 and PLACEHOLDERcff917ded0a54dfd) for managing Linux containers. - WSL containers API for programmatic execution of Linux containers within Windows applications. New commands and enhancements include: - PLACEHOLDER9a5ce8c0763b7886, PLACEHOLDER3ee1e1334fe287fb, PLACEHOLDER4860ddbd841eef41, PLACEHOLDERe699cb1a0eaadb6e, wslc network disconnect, and support for container health checks. - Integration of Microsoft Intune and Microsoft Defender for Endpoint for security and governance in container workflows. - New settings in Intune for managing WSL container access and registry controls. Community integrations include support for VS Code dev containers and various tools for managing WSL containers. Future plans involve adding wslc compose support and improving core platform capabilities for WSL, including networking and cross-OS file performance.
Winsage
September 29, 2026
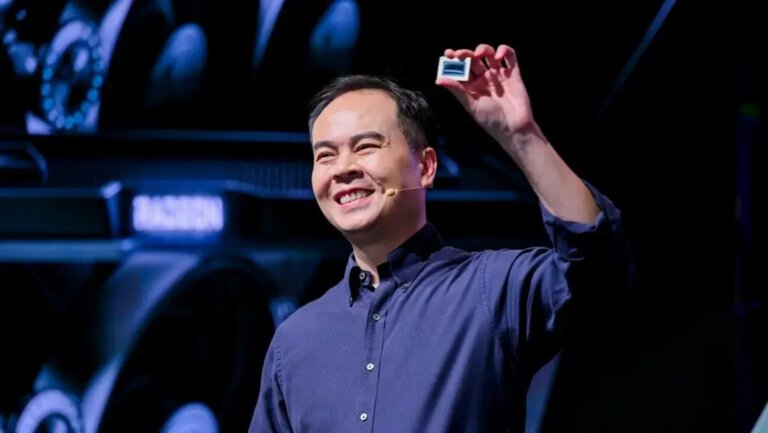
AMD and Perplexity have launched Portable Computer, a software solution for Windows PCs with Ryzen AI Max Series processors, enabling local AI tasks and workflow management for Pro and Max subscribers. This allows users to run extensive AI models on their devices without relying on cloud processing, enhancing privacy and conserving Perplexity Computer credits. The software integrates local models with agent orchestration, scheduling, and security controls, and connects with popular workplace applications like Gmail and Slack. AMD's AI PCs, introduced in 2023, feature a neural processing unit that allows local AI operations alongside standard applications. This collaboration signifies a shift towards more AI processing on personal devices, aiming to automate tasks and improve user experience. Jack Huynh from AMD highlighted the transformation of PCs into intelligent partners, emphasizing the coexistence of local and cloud AI in their strategy.
AppWizard
September 17, 2026
Security researchers at Zimperium have identified a new strain of Android malware called RatHat, which is linked to threat actors from China and is designed to steal sensitive credentials and banking information. RatHat infiltrates devices through phishing sites, malvertising, and SMS phishing (smishing), tricking users into downloading malicious Android package kits (APKs). The malware uses a dropper to activate its payload, which is hidden in encrypted assets, and employs techniques to bypass Android's security measures. RatHat consists of three main components: a malicious Android application, a Go agent (liblocal-service.so), and an FRP client (libmedia_codec.so). The app collects sensitive information such as banking credentials, notifications, 2FA codes, OTP keys, and screen inputs. It features a generative AI user interface-automation engine that communicates in Mandarin and can perform various tasks like determining screen coordinates and issuing navigation commands. The Go agent acts as a command-and-control executor, executing commands to bypass app-level security and manage system-level tasks. The FRP client maintains a secure reverse tunnel to the attacker's server, allowing ongoing remote access to the device. The architecture of RatHat demonstrates the inadequacy of traditional mobile security measures against such advanced threats.
Winsage
September 10, 2026
Microsoft's Patch Tuesday on September 8, 2026, addressed two critical Windows privilege escalation vulnerabilities: CVE-2026-85880 and CVE-2026-81963, both with a CVSS score of 7.8. CVE-2026-85880 is a heap-based buffer overflow in the Windows Advanced Local Procedure Call (ALPC), allowing attackers with low-privilege local access to escalate privileges to SYSTEM. CVE-2026-81963 involves improper link resolution in the Windows Update Stack, enabling similar privilege escalation. Both vulnerabilities require no user interaction and have been actively exploited prior to the patch release. CISA added them to its Known Exploited Vulnerabilities catalog on September 8, 2026, with a remediation deadline of September 22 for U.S. federal agencies. CVE-2026-85880 affects various Windows 10 and Server versions but excludes Windows 11 and Windows Server 2025. CVE-2026-81963 impacts newer Windows platforms, including Windows 11 and Windows Server 2025. Microsoft released security updates for both vulnerabilities on September 8, 2026, and organizations are advised to prioritize these updates. Security teams should monitor for signs of privilege escalation and unusual SYSTEM-level activities related to these vulnerabilities.
Tech Optimizer
September 10, 2026
Bitdefender is recognized for its strong detection capabilities, mid-range pricing, and minimal system impact. Malwarebytes offers a free scanner for cleaning infected Macs, while Intego specializes in macOS with features tailored for Apple users. Norton provides a comprehensive security package with VPN, backup, and identity monitoring features. Gen Digital owns Norton, Avast, AVG, and Avira, indicating that these brands share threat intelligence and engineering resources. The 2026 Mac Antivirus Scorecard ranks Bitdefender highest with a score of 8.8, followed by Intego (8.2), Malwarebytes (8.3), ESET (8.3), and Norton (7.4). Pricing structures often include discounted first-year rates that can double upon renewal. Free options include Avast and Avira with real-time protection, while Malwarebytes offers a free on-demand scanner. Multi-device licensing can provide better value, and business Macs should use business licenses for essential features. macOS has built-in protections like XProtect and Gatekeeper, but third-party antivirus solutions can enhance security against newer threats.
Winsage
September 2, 2026
An active malware campaign is using counterfeit software-download websites to distribute malicious installers, primarily targeting users seeking popular software. This campaign has significantly affected China-based operations of multinational corporations and Chinese-speaking users. The malware, once executed, can establish persistence, undermine security measures, and communicate with attacker-controlled infrastructure. Victims span various sectors, including healthcare, manufacturing, gaming, technology, logistics, government, and education. Microsoft associates this campaign with a Chinese threat cluster called Silver Fox, known for using spoofed vendor download pages to spread Gh0st RAT and ValleyRAT. The malicious websites are hosted on .com.cn and .hl.cn domains, featuring Chinese-language content. The downloaded files are dynamically generated, and upon execution, they deploy a wrapper installer that initiates the malware payload. The malware achieves persistence through scheduled tasks and interferes with Windows Update services. The campaign establishes command-and-control communication over non-standard ports, with two identified domains linked to the activity. Microsoft Defender has detected the threat and initiated containment procedures. Kaspersky reported a related malicious installer exploiting a legitimate adware application to execute a backdoor, which captures keystrokes and clipboard contents. ValleyRAT, a sophisticated implant, can collect system information, reboot the computer, capture screenshots, and transmit logs. The attackers are motivated by cyber espionage and financial gain, targeting organizations globally. A subgroup within GoldenEyeDog, known as CuboidalCanine, has also been linked to the use of ValleyRAT, particularly in the gambling industry. In June 2026, Chinese authorities addressed cybercrime cases involving a new variant of the Silver Fox trojan.
Tech Optimizer
August 31, 2026
Silver Fox is linked to the distribution of a backdoor malware called ValleyRAT, disguised as the legitimate QN Wallpaper adware application. Once installed, ValleyRAT provides complete control over the compromised machine. The malware uses DLL sideloading to operate under the guise of a legitimate process, bypassing security measures. It disables Windows Defender and adds itself to autorun entries, and can mark its process as critical, causing system crashes if terminated. Kaspersky has identified specific indicators of compromise (IoCs) including hashes, command-and-control servers, and associated domains. In 2026, Kaspersky recorded over 100,000 detections of ValleyRAT affecting more than 1,500 unique users, mainly in China and India.
Winsage
August 24, 2026
The configuration reveals a sequence of actions including file and directory deletions, relocations, and registry operations, such as deleting and modifying registry keys and values. The file-move primitive can transform into an arbitrary file-write capability when directed to the System32 directory. The automation of these actions is achieved through a tool called BTRCLI, which extracts a legitimate driver from Windows Defender, constructs an encrypted transaction, and loads the driver, using the target machine's version of BTR.sys to avoid external drivers.
Search