security flaws

Winsage
October 15, 2026
Microsoft has identified 1,416 vulnerabilities in its systems, with 85 classified as “critical.” Among these, 67 are categorized as remote code execution (RCE) vulnerabilities. One vulnerability is actively exploited, and two have been publicly disclosed. The upcoming Patch Tuesday is on November 10th, 2026, and users are advised to upgrade to Windows 11 25H2 or 26H2. A specific vulnerability, CVE-2026-96951, allows attackers to bypass system defenses by masking the origin of executable files. Microsoft has flagged 42 critical vulnerabilities, including 30 RCE vulnerabilities, which can allow attackers to execute malicious code remotely.
Winsage
October 14, 2026
Microsoft has identified 1,416 vulnerabilities within its systems, with 85 classified as "critical." Among these, 67 are remote code execution (RCE) vulnerabilities. One vulnerability is actively exploited, and two others were disclosed prior to the assessment. The next opportunity for users to address these vulnerabilities will be on November 10th, 2026, during Patch Tuesday. Users are encouraged to upgrade to Windows 11 versions 25H2 or 26H2. A specific vulnerability, CVE-2026-96951, allows attackers to bypass system defenses by masking executable file origins. Of the critical vulnerabilities, 30 are RCE vulnerabilities that enable remote execution of malicious code without authentication or user interaction.
Winsage
October 14, 2026
Z.ai's GLM model identified 23 vulnerabilities in the Windows operating system, confirmed by Microsoft's Security Response Center (MSRC). This marks a significant advancement in commercial software security, demonstrating the model's autonomous capability in independent vulnerability discovery. Since the release of GLM-5.2, Z.ai has uncovered over 4,200 vulnerabilities across about 390 open-source projects, with over a thousand categorized as critical to high severity. Z.ai has established a public Security Disclosure Ledger to track its findings through a coordinated disclosure process. The confirmation of vulnerabilities by MSRC is notable due to the rigorous nature of their vulnerability triage operations. Z.ai's GLM-5.3 achieved a score of 84.5% on CyberGym, outperforming competitors like Anthropic's Mythos 5 and OpenAI's GPT-5.6 Sol. Reports indicate that NIST's AI safety division has flagged GLM-5.3 due to concerns about its cyber capabilities, particularly regarding the potential for modified versions to reduce safety features. Z.ai plans to continue targeting commercial software in its efforts.
Winsage
September 24, 2026
Security researchers from Graz University of Technology in Austria have discovered significant vulnerabilities in the file notification systems of major operating systems: Android, Linux, macOS, and Windows. These flaws have existed for decades and can lead to the leakage of sensitive system information. The affected systems include inotify on Linux (since 2005), FileObserver on Android (since 2008), ReadDirectoryChangesW on Windows (since 2000), and FSEvents on macOS (since 2007). The vulnerabilities allow unprivileged users to monitor file events without explicit read permissions, enabling potential attacks such as inter-keystroke timing attacks and website fingerprinting. For example, on Linux, monitoring a readable directory can leak events on files that cannot be read, allowing attackers to achieve a 93.1% to 100% accuracy rate in monitoring keystrokes. Specific vulnerabilities include CVE-2025-68788 on Linux, which received a partial fix in December 2025, and issues on Android where FileObserver can bypass app storage isolation. On macOS, limited information is available due to a lack of bypasses for private directories, while on Windows, monitoring the root directory can reveal the full path of every accessed file, allowing real-time tracking of web activity with a 97.8% accuracy rate. Microsoft has described the issue as "by-design," which has faced criticism. The researchers propose stronger mitigations, such as disallowing monitoring of entire drives on Windows and introducing a permission system for file monitoring on Windows and macOS. Their findings will be presented at the ACM CCS 2026 conference in November in The Hague, Netherlands.
Winsage
September 9, 2026
Microsoft's September Patch Tuesday update for Windows 11 introduces several enhancements, including the ability to reposition the taskbar to the top, left, or right sides of the screen. Users can adjust the taskbar's alignment, height, and icon size, though the auto-hide feature is limited to the bottom position. The Start menu now allows users to select between Small and Large sizes, with the Recommended section rebranded as Recent, and options to hide their name and profile picture. The Search window has been streamlined to focus on suggested or recent searches. The update addresses 995 security vulnerabilities, including 121 critical vulnerabilities and two zero-day flaws (CVE-2026-81963 and CVE-2026-85880), which could allow attackers to gain system-level privileges.
Winsage
September 9, 2026
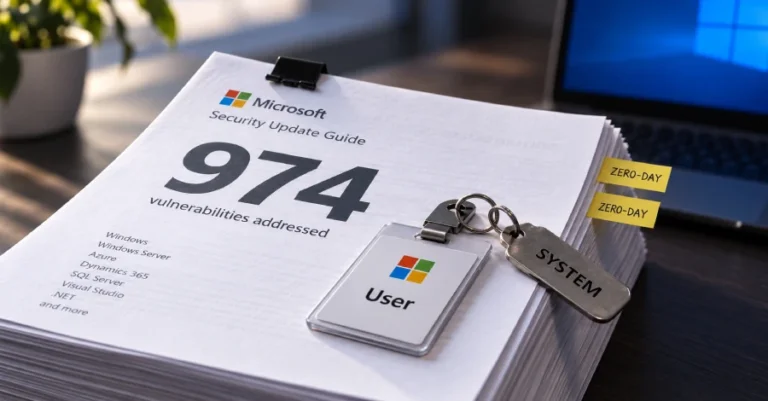
Microsoft addressed 974 vulnerabilities in its software suite during its recent Patch Tuesday, marking a record high. The breakdown includes 723 flaws in Windows, 111 in Office, 62 in SQL, and 22 in Developer Tools, with over 110 rated as critical. Two actively exploited vulnerabilities are CVE-2026-85880 and CVE-2026-81963, both allowing local privilege elevation. Other notable vulnerabilities include CVE-2026-55007 (8.1), CVE-2026-80097 (8.6), CVE-2026-69465 (8.8), and several with CVSS scores of 9.6 and above. Microsoft has patched a total of 2,760 security flaws this year, reflecting a trend of increasing vulnerability discoveries. Despite the extensive patching, no significant spike in active exploits has been observed.
Winsage
August 11, 2026
A consortium of tech companies, including Microsoft, Google, Amazon, Nvidia, Apple, and Anthropic, is working on cybersecurity by identifying and fixing vulnerabilities. The platform Mythos has made it easier to find security flaws, but it has resulted in more vulnerabilities than companies, especially Microsoft, can manage. Microsoft is currently focusing on high-severity security threats, with plans to address moderate-severity flaws later, but lacks an immediate strategy for low-severity issues.
Winsage
August 6, 2026
Windows operating systems have hidden functionalities and privacy enhancements introduced through regular updates, which are crucial for maintaining system security. Neglecting updates leaves known vulnerabilities open to exploitation by malicious actors, as Microsoft typically addresses security flaws only after they are identified. Windows Update is the primary mechanism for addressing these vulnerabilities. Unpatched systems become targets for cyber threats, leading to severe consequences such as remote code execution, privilege escalation, ransomware attacks, and boot-level compromises. The PrintNightmare vulnerability (CVE-2021-34527) was acknowledged by Microsoft after active exploitation was detected, leading to the release of patches. The WannaCry cyberattack in May 2017 affected over 300,000 computers due to an unpatched SMB flaw, highlighting the risks of outdated systems. Timely updates can prevent vulnerabilities that may lead to ransomware, credential theft, and other compromises. Users are advised to install updates promptly and avoid connecting unsupported versions to the internet.
Search