security framework

Winsage
September 20, 2026
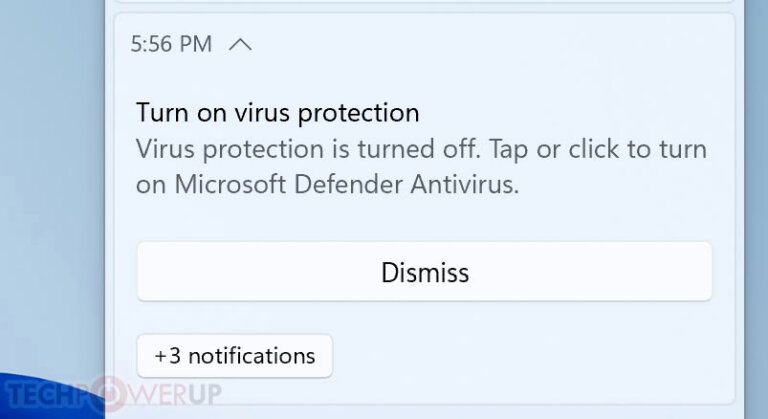
Microsoft resolved an issue in its Windows Security framework that incorrectly indicated Microsoft Defender Antivirus was disabled. This fix was implemented through Defender platform update 4.18.26080.4, released on September 17. The update installs automatically unless users have blocked mandatory security updates. Users had been receiving false alerts during system boot and intermittently afterward, which redirected them to the Windows Security home tab where settings appeared normal. Microsoft acknowledged the issue on August 28, affecting all supported versions of Windows and Windows Server with the latest Defender updates, but did not specify the triggering update. Users in the Windows Insider program reported similar warnings as early as June.
AppWizard
September 18, 2026
Google has launched the AndroidX Security State and Security State Provider libraries, enhancing Android's security framework. These tools allow applications to assess the security status of individual components on a device, rather than relying solely on the overall security patch level. Applications can now verify specific security fixes, identify available updates, and check for pending installations. This is particularly useful for security-sensitive applications, such as banking software, which can confirm the presence of necessary security fixes before allowing transactions. The libraries also enable apps to check for the resolution of specific vulnerabilities (CVEs), ensuring critical fixes are in place before enabling features like tap-to-pay. Phone manufacturers can communicate specific security fixes without changing the overall security patch date, meaning a device may show an outdated patch date while still having resolved certain vulnerabilities.
AppWizard
September 18, 2026
The new AndroidX Security State libraries, with stable releases of Security State v1.1.0 and Security State Provider v1.0.0, allow developers to evaluate the security status of individual device components. They provide three levels of security patch information: Device Security Patch Level (DSPL), Published Security Patch Level (PSPL), and Available Security Patch Level (ASPL). These libraries enable checks on critical components of the Android operating system, including system modules and the Linux kernel, which are represented by version numbers rather than monthly patch dates. Applications that prioritize security can utilize this detailed patch information to assess vulnerabilities, particularly those tracked as Common Vulnerabilities and Exposures (CVEs). The libraries also integrate with the Open Source Vulnerabilities (OSV) database for access to Android Security Bulletin data and device-specific vulnerability reports. Additionally, Android 17 allows manufacturers to declare individual security fixes beyond the stated security patch level, and Google is working with manufacturers to transition their OTA update clients to this new standardized system.
Tech Optimizer
September 13, 2026
The landscape of encryption engines has stabilized, with Microsoft BitLocker and Apple FileVault being the primary solutions. As of 2026, the emphasis is on management rather than just acquiring encryption technology. Key management elements include audit proofing, key escrow and recovery, policy enforcement, and pre-boot options. Native encryption solutions lack features such as fleet-wide compliance proof, centralized key escrow, consistent policy enforcement, advanced pre-boot authentication, and removable-media encryption. Various management models are available for different environments, including: 1. Microsoft BitLocker with Intune: Free for Windows Pro/Enterprise, integrates with Entra ID for key management. 2. Sophos: Manages both BitLocker and FileVault from a single console. 3. ESET: Offers lightweight management and removable-media protection. 4. Trend Micro: Integrates encryption with DLP capabilities. 5. Check Point: Provides advanced pre-boot options and policy management. 6. Trellix: Comprehensive enterprise encryption suite with a complex management interface. 7. WinMagic: Focuses on cross-platform encryption and strong pre-boot options. 8. Broadcom (Symantec): Manages native engines within its broader security framework. 9. Dell: OEM-integrated encryption management for Dell hardware. 10. Kaspersky: Provides encryption management but is restricted in the U.S. Key considerations before deploying encryption include ensuring key escrow is in place, conducting recovery tests, and being mindful of removable media and server encryption. Common mistakes include using outdated freeware and not verifying key escrow. Organizations should request auditor reports for compliance verification and confirm claims of compatibility and pre-boot functionality. Native encryption engines are free, while management layers typically charge on a per-endpoint basis.
Tech Optimizer
September 7, 2026
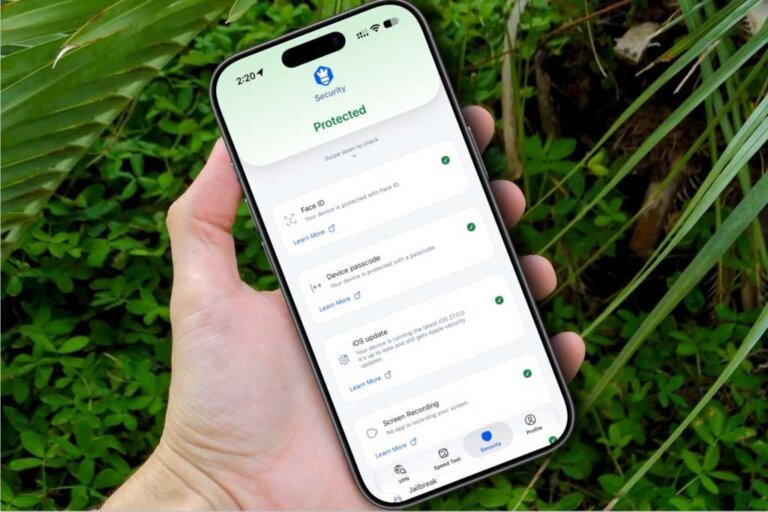
Intego ONE Complete has launched the Intego ONE: VPN & Wi-Fi Security app for iPhone, available at no extra charge to Complete subscribers. The app provides VPN protection, Wi-Fi security assessments, and checks on built-in iPhone security settings but does not function as antivirus software. It enhances existing Apple security measures by addressing vulnerabilities related to insecure Wi-Fi connections and unprotected internet access. The app is accessible to both new and existing subscribers, and Intego is currently offering a 50% discount on subscriptions until September 30, 2026. Intego ONE is available in three tiers: Essential, Advanced, and Complete, with the Complete tier including the new iPhone app. The app features a VPN that encrypts internet connections on public Wi-Fi, Wi-Fi security checks, and assessments of iPhone security settings. While traditional viruses are rare on iPhones, threats like spyware and exploits still exist. The app does not replace Apple's malware protection but complements it. Intego ONE Complete is recommended for Mac and iPhone owners, particularly those who travel frequently or connect to public Wi-Fi. The pricing includes various deals, with a 50% discount currently available and a subsequent 35% discount after the promotional period.
Winsage
September 3, 2026
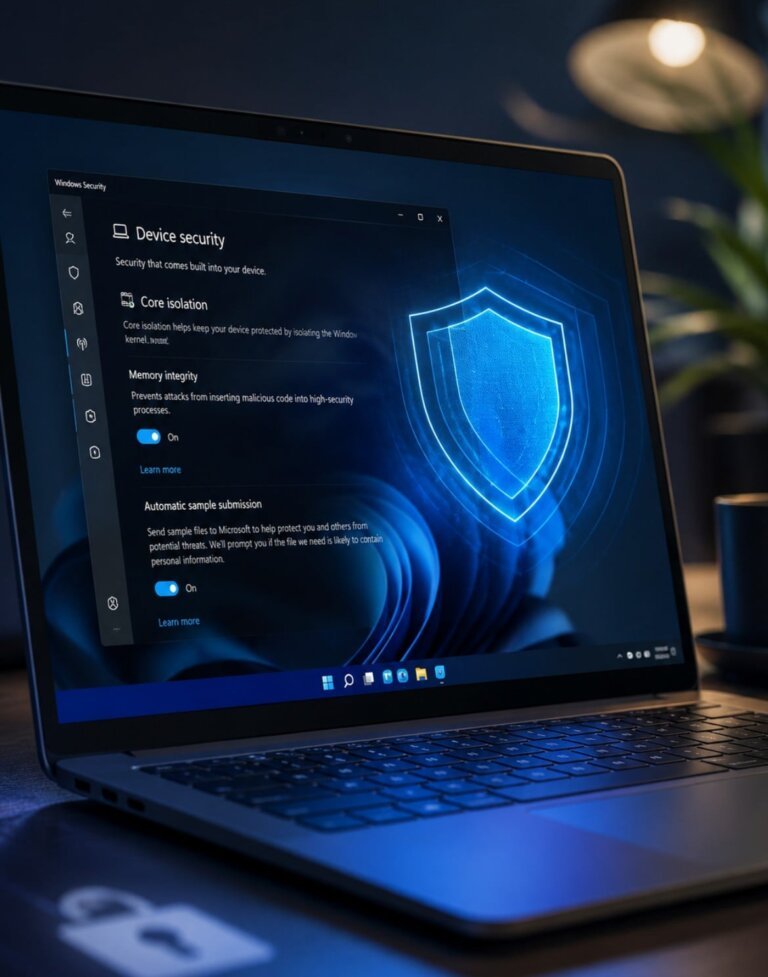
Microsoft plans to automatically activate Memory Integrity on a broader range of eligible systems starting October 2026, rolling it out through standard Windows quality updates. Prior to activation, Windows will assess hardware, drivers, and performance to ensure compatibility. Memory Integrity, part of Virtualization-based Security (VBS), uses the Windows hypervisor to create a secure environment for integrity checks on kernel code. Compatibility with drivers is crucial, as many older applications may not meet the stricter standards required for HVCI. Potential compatibility issues may arise with anti-cheat solutions, third-party input methods, and banking protection programs, which could lead to software malfunctions or boot failures. A readiness check will evaluate hardware compatibility, with eligible systems including Intel processors from the 8th generation, AMD processors from Zen 2, and Qualcomm Snapdragon 8180 or newer, along with specific RAM and storage requirements. The rollout will be gradual, and users who previously disabled HVCI will not face unexpected reactivation. Microsoft recommends updating affected applications or drivers in case of compatibility issues.
Winsage
September 2, 2026
Microsoft will automatically enable its Memory Integrity feature on more eligible Windows PCs starting in October 2026, enhancing kernel-level protection. PCs with Memory Integrity currently disabled will retain their settings. Windows will also activate Virtualization-based Security (VBS) where necessary, which supports Memory Integrity. An automatic assessment will determine device eligibility based on hardware capabilities and compatibility. The rollout applies to Windows 11 installations meeting specific hardware specifications, including an 8th Generation or newer Intel processor or AMD Zen 2 or newer processor, at least 8GB of RAM, an SSD with a minimum of 64GB, compatible drivers, and enabled hardware virtualization. Memory Integrity, also known as Hypervisor-Protected Code Integrity (HVCI), has been part of Windows since the Windows 10 era and is now more integral to Windows 11 security for new installations. However, it may impact gaming performance, leading some gamers to disable it, which Microsoft has acknowledged in its recommendations.
AppWizard
August 28, 2026
Significant strides have been made in enhancing the security framework for Android applications, with developers encouraged to stay informed about best practices to fortify their apps against vulnerabilities. Key recommendations include regularly updating libraries, implementing secure coding practices, and utilizing Android’s built-in security features like Play Protect. The Android Developers team has released new resources to help developers integrate these security measures. Additionally, the OkHttp Changelog has introduced updates for improved performance and reliability, including improved connection pooling, bug fixes, and new features to streamline development.
Tech Optimizer
August 17, 2026
The landscape of mobile security has shifted away from traditional third-party antivirus software, as modern Android devices are equipped with built-in security features. Key components of this security framework include Google Play Protect, which blocked 27 million malicious apps in 2025; application sandboxing that isolates apps; proactive permissions that enhance user privacy; AI-powered threat detection for sophisticated attacks; and strict sideloading policies to limit risks from off-market malware. Despite these defenses, threats such as social engineering, phishing, malicious push notifications, and unsecured public Wi-Fi remain prevalent, often evading traditional antivirus solutions. However, certain scenarios, such as frequent sideloading, using older devices, connecting to public Wi-Fi, or suspected infections, may warrant the use of third-party antivirus apps for additional protection. Overall, the built-in security features of Android provide a strong defense for most users, with user education being crucial for effective smartphone protection.
Tech Optimizer
August 16, 2026
The relevance of third-party antivirus software for mobile devices has declined as modern Android devices come with robust built-in security features. Google Play Protect blocks millions of harmful apps and conducts regular scans of installed apps. Android employs sandboxing technology to isolate applications, has a proactive permissions system, and provides regular security updates. While Android is not immune to malware, many threats now arise from social engineering tactics rather than technical vulnerabilities. Users face risks when connecting to public Wi-Fi networks, and malicious push notifications can mislead them. Third-party antivirus may be beneficial for users who sideload apps or notice signs of infection, but for most users, Google's Play Protect suffices. Older devices lacking updates are at higher risk, and while antivirus apps can provide additional protection, education and user vigilance are crucial for minimizing risk.
Search