security measures

Tech Optimizer
September 22, 2026
LastPass has identified a sophisticated scheme targeting users of its Authenticator app, involving SEO poisoning and deceptive GitHub pages that distribute malicious ZIP files disguised as legitimate software. Users searching for "LastPass Authenticator download" may encounter these counterfeit pages, which redirect them to a malicious server delivering a ZIP file containing vsdbg.exe and vsdbg.dll. The executable is a legitimate Microsoft debugging tool exploited to execute the malicious DLL through DLL sideloading, allowing the malware to run undetected. Named Rapuncel by security researchers from Delphos, this malware is undetectable by antivirus engines and targets a hardcoded list of 145 antivirus and endpoint security products, disabling them upon detection. Rapuncel harvests sensitive information, including saved passwords from over 25 web browsers, cryptocurrency wallet files from more than 30 applications, and session tokens from platforms like Discord and Steam. It also captures screenshots and compiles a profile of the infected system, uploading the stolen data to an attacker-controlled server. The malware includes a kernel driver that intercepts web traffic, allowing for advertisement injection and search result manipulation. This campaign has been active for several months, with LastPass vaults remaining unaffected. Users are advised to download applications only from trusted sources. Rapuncel establishes persistence on infected machines by installing itself as a Windows service that starts with the system and terminates activated security products. Removing the kernel driver requires booting into Safe Mode or using external recovery tools, as standard Windows utilities cannot eliminate software operating at that level.
Tech Optimizer
September 21, 2026
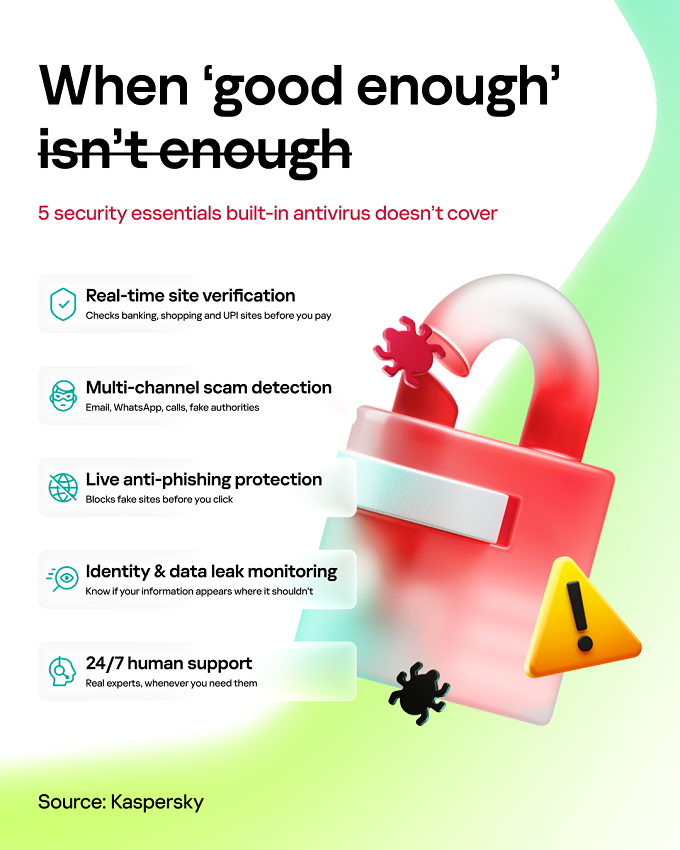
The landscape of computer security has changed significantly over the past two decades. In 2026, antivirus protection remains important, but the need for separate third-party programs has decreased for many users due to the built-in Microsoft Defender in Windows 11, which is activated by default and effectively blocks 100% of common malware samples according to independent testing by AV-TEST. Windows 11 also includes additional protective features like SmartScreen and a robust Firewall. While dedicated security suites from companies like Norton and Bitdefender offer advanced functionalities, many users may find adequate protection with the built-in tools. Research from AV-Comparatives indicates that performance varies among security programs, particularly against real-world attacks. Phishing attacks accounted for approximately 60% of initial access points in incidents examined by the ENISA Threat Landscape report from 2025, highlighting that user behavior is a significant vulnerability. Modern web browsers and operating systems have enhanced their security measures, with Google Chrome, Microsoft Edge, macOS, and Android incorporating features to protect users from harmful websites and downloads. For the average Windows 11 user who keeps their system updated and practices safe browsing, built-in protection is generally sufficient, though paid antivirus options can provide additional tools.
Winsage
September 19, 2026
Windows XP was released in two versions: Retail for individual consumers and Volume for Microsoft's partners and OEMs. The product key FCKGW-RHQQ2-YXRKT-8TG6W-2B7Q8 became widely recognized due to a potential leak by an insider at a major OEM, which was then spread by the pirate group Devils0wn. The Volume version's activation system required a unique key, but the FCKGW key was incompatible with the standard installation CD. To verify the legitimacy of Volume discs, the activation system searched for a secret 10MB binary blob exclusive to the Volume media. Microsoft blacklisted the FCKGW key with Service Pack 1 and implemented further security measures with Service Pack 2, restricting access to certain updates. Contrary to prior beliefs, the key's functionality was not due to a simple key generation algorithm but was designed by skilled engineers.
AppWizard
September 19, 2026
ESG reporting standards are becoming increasingly important in mobile technology, affecting various aspects such as data management, material sourcing, energy consumption, privacy, supply chain dynamics, and product accountability. The lifecycle of mobile devices involves raw material sourcing, component manufacturing, device assembly, shipping, marketing, sales, updates, repairs, trade-ins, and disposal. Companies must understand ESG standards to create coherent sustainability narratives and may need to disclose supplier practices, carbon emissions, and governance documentation when partnering with larger firms. Consumers are now asking more questions about the longevity of software updates, repairability, data collection, packaging design, and the accountability of product creators. The rise of connected devices complicates ESG reporting due to extended product lifecycles and the need for ongoing software support. Companies should track product lifespan estimates, warranty data, repair trends, and update schedules to improve product quality and ESG reporting credibility. Emerging tech companies can start their ESG journey by cataloging product claims, consolidating evidence, designating ownership of records, and reviewing product lifecycle information. Global sustainability frameworks exist but may not align with consumer needs for straightforward product information. Successful mobile tech companies will need to bridge formal reporting requirements with accessible product-level communication. Trust and transparency in practices will increasingly influence consumer choices in mobile technology.
AppWizard
September 18, 2026
Cybersecurity experts have identified a new Android malware named RatHat, believed to be operated by Chinese threat actors. RatHat is distributed primarily through smishing and malvertising campaigns, leading users to deceptive download portals. It employs an automated multi-stage infection process and exploits Accessibility features along with a local ADB self-pairing mechanism to escape the Android application sandbox. The malware uses various anti-analysis techniques, including container tampering, manifest bombs, DEX bytecode poisoning, and dual string-encryption. RatHat's architecture consists of a malicious Android application, a Go agent, and an FRP reverse-proxy client, which together enable it to gain critical system permissions and perform various malicious activities such as credential capturing, screen recording, and SMS interception. Even if uninstalled, the malware retains shell access to the device, allowing attackers to reinstall it. RatHat can serialize the device's Accessibility tree to XML and communicate with a Generative AI assistant for tasks like screen coordinate determination and text extraction. The Go Agent, masquerading as a native library, exploits shell access to execute commands and establish a persistent connection to a command-and-control server via the FRP client. The C2 server can issue extensive commands to collect sensitive information, including SMS messages, credentials, files, and keystrokes, and RatHat also features a hardware-level keylogger.
AppWizard
September 17, 2026
Security researchers at Zimperium have identified a new strain of Android malware called RatHat, which is linked to threat actors from China and is designed to steal sensitive credentials and banking information. RatHat infiltrates devices through phishing sites, malvertising, and SMS phishing (smishing), tricking users into downloading malicious Android package kits (APKs). The malware uses a dropper to activate its payload, which is hidden in encrypted assets, and employs techniques to bypass Android's security measures. RatHat consists of three main components: a malicious Android application, a Go agent (liblocal-service.so), and an FRP client (libmedia_codec.so). The app collects sensitive information such as banking credentials, notifications, 2FA codes, OTP keys, and screen inputs. It features a generative AI user interface-automation engine that communicates in Mandarin and can perform various tasks like determining screen coordinates and issuing navigation commands. The Go agent acts as a command-and-control executor, executing commands to bypass app-level security and manage system-level tasks. The FRP client maintains a secure reverse tunnel to the attacker's server, allowing ongoing remote access to the device. The architecture of RatHat demonstrates the inadequacy of traditional mobile security measures against such advanced threats.
Search