SEO

Tech Optimizer
September 22, 2026
LastPass has identified a sophisticated scheme targeting users of its Authenticator app, involving SEO poisoning and deceptive GitHub pages that distribute malicious ZIP files disguised as legitimate software. Users searching for "LastPass Authenticator download" may encounter these counterfeit pages, which redirect them to a malicious server delivering a ZIP file containing vsdbg.exe and vsdbg.dll. The executable is a legitimate Microsoft debugging tool exploited to execute the malicious DLL through DLL sideloading, allowing the malware to run undetected. Named Rapuncel by security researchers from Delphos, this malware is undetectable by antivirus engines and targets a hardcoded list of 145 antivirus and endpoint security products, disabling them upon detection. Rapuncel harvests sensitive information, including saved passwords from over 25 web browsers, cryptocurrency wallet files from more than 30 applications, and session tokens from platforms like Discord and Steam. It also captures screenshots and compiles a profile of the infected system, uploading the stolen data to an attacker-controlled server. The malware includes a kernel driver that intercepts web traffic, allowing for advertisement injection and search result manipulation. This campaign has been active for several months, with LastPass vaults remaining unaffected. Users are advised to download applications only from trusted sources. Rapuncel establishes persistence on infected machines by installing itself as a Windows service that starts with the system and terminates activated security products. Removing the kernel driver requires booting into Safe Mode or using external recovery tools, as standard Windows utilities cannot eliminate software operating at that level.
AppWizard
September 5, 2026
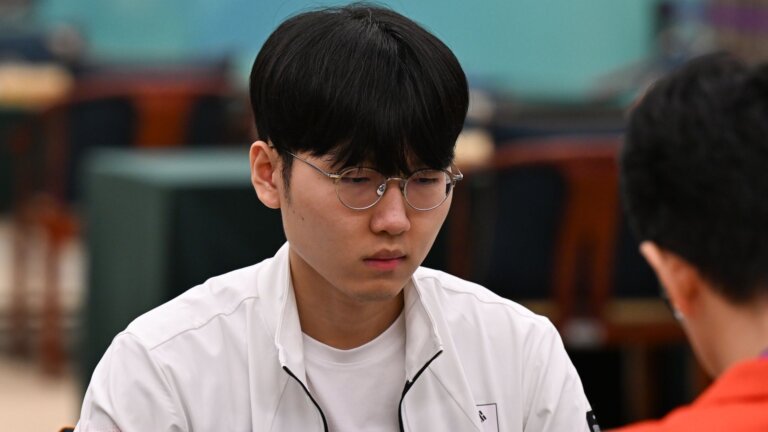
Go grandmaster Shin Jin-seo became the first human to win against the AI platform KataGo on July 21, achieving victory in an official three-game series with a final score of 2-1. Shin, who is 26 years old, played with a two-stone handicap and initially lost the first match before winning the next two. His victory is significant as it contrasts with the previous defeat of grandmaster Lee Sedol by Google's AlphaGo a decade ago. Shin expressed the desire to challenge AI under more difficult conditions in the future and emphasized the importance of personal strategy over imitating AI moves.
Tech Optimizer
September 4, 2026
Organizations are increasingly aiming to establish their own governed AI and data platforms, with 95% of enterprises planning to develop such platforms within the next three years, though only 13% have done so. EDB has reported significant traction for its EDB Postgres® AI (EDB PG AI) platform, which unifies transactional, analytical, and agentic workloads into a single system. PAC 2000A Conad has revamped its data infrastructure using EDB PG AI to support over 1,600 stores and 7,000 connected devices, ensuring compliance with NIS2 regulations. C Platform in Korea is experiencing a surge in demand for hybrid and on-premises capabilities, driven by significant investment in sovereign AI and the AI Basic Act mandating governance for AI deployment. Notable adopters of EDB PG AI include the Industrial Bank of Korea, Shinhan EZ Insurance, NTT East, MNTN, Euronext FX, and Kyobo Book Centre.
Tech Optimizer
September 4, 2026
EnterpriseDB (EDB) has reported advancements in the adoption of its EDB Postgres AI (EDB PG AI) platform, which integrates transactional, analytical, and AI workloads. While 95% of enterprises aspire to become their own AI and data platforms within three years, only 13% have achieved this. EDB PG AI supports existing systems and prepares enterprises for future AI capabilities. A case study highlights PAC 2000A Conad, which restructured its data infrastructure with EDB PG AI, serving over 1,600 stores and 7,000 devices. In Korea, over billion has been invested in the sovereign AI market, with organizations seeking hybrid and on-premises solutions despite challenges from fragmented data environments. Notable users of EDB PG AI include the Industrial Bank of Korea and Shinhan EZ Insurance. EDB PG AI is built on Postgres and allows enterprises to optimize data and AI capabilities with governance at the data layer.
AppWizard
June 9, 2026
Old-school gaming consoles are seeing a resurgence, but hackers are exploiting this trend with a malware campaign called "WeedHack," which emerged in January. This malware operates on a "Malware-as-a-Service" model, allowing users to purchase it to infect victims. WeedHack functions as a remote access infostealer, compromising computers to manipulate screens, access webcams, and steal sensitive data. It propagates by enticing users with unofficial "Minecraft" mods and clients, often using videos and download links as bait. Additionally, it employs "SEO poisoning" to promote fake websites as legitimate sources for these mods on platforms like Discord and Reddit. WeedHack disguises itself as a JAR file, similar to the official "Minecraft" client, and once executed, it installs its payload from Ethereum server domains. It can insert itself into antivirus exclusion lists, evading detection, and McAfee's tests show that Windows Defender is ineffective against it. The malware collects extensive information, including Wi-Fi networks and browser cookies, and grants hackers complete control over infected computers. The WeedHack virus serves as both malware and a training ground for aspiring hackers, structured into two tiers: a free version with core capabilities and a paid subscription for advanced features. A community has formed around WeedHack, offering tutorials, a Discord server, and a website for feature requests and custom payload creation. This community aspect lowers the barrier for newcomers, particularly targeting a younger audience that may not understand online safety.
AppWizard
June 4, 2026
A recent cybersecurity analysis from McAfee Labs has revealed a malware campaign involving WeedHack, which has garnered over 116,000 hits and is accumulating 2,000 to 3,000 malicious hits daily. WeedHack is marketed as malware-as-a-service (MaaS) and is accessible on the internet, allowing individuals with minimal technical skills to use it for harmful activities. A dedicated Telegram channel for WeedHack has over 850 members, many of whom are teenagers and young adults using the malware for cyberbullying. The malware spreads primarily through YouTube videos promoting Minecraft mods, which often conceal the WeedHack malware. Additionally, bad actors use SEO poisoning tactics to elevate fake websites posing as legitimate Minecraft clients. McAfee lists several legitimate clients targeted by WeedHack, including Meteor Client, Radium Client, and Wurst Client. For an additional fee, attackers can access premium features like webcam access, keylogging, and file management. McAfee advises players to be cautious when downloading mods and to seek help from trusted adults if approached by individuals claiming to have compromised their systems.
AppWizard
June 3, 2026
A malware campaign named WeedHack has impacted over 116,000 Minecraft players since its inception earlier this year, according to a report from McAfee. Cybercriminals are using SEO poisoning to exploit gamers searching for mods, particularly targeting those hosted on GitHub and creating deceptive web pages that mimic official mod sites. Notable affected projects include Meteor Client, Radium Client, Wurst Client, Aristois, LiquidBounce, and Impact Client. Attackers also produce polished YouTube videos to promote malware, with comments guiding viewers on installation and links to malicious sites. The malware operates in two tiers: a free tier that steals cookies and passwords, targets crypto wallets, captures screenshots, and extracts credentials, and a premium tier that offers advanced capabilities like webcam control and keylogging for a monthly fee. The accessibility of such malware is concerning, prompting Minecraft users to be cautious when searching for and installing mods.
AppWizard
June 3, 2026
Cybercriminals are using YouTube to distribute malware targeting Minecraft users, identified as Weedhack by McAfee Labs. This malware disables security defenses and allows attackers remote access to infected computers. The campaign offers both free and paid versions, making it accessible, especially to younger audiences. It also has the capability to steal Minecraft accounts, increasing its appeal.
Search