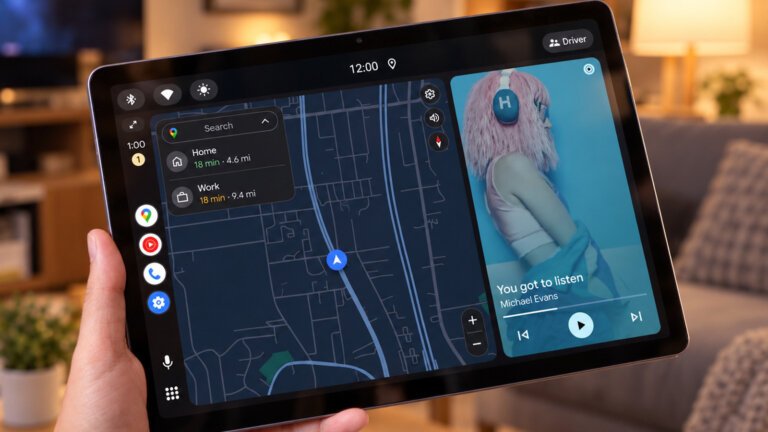
A spare tablet, a USB cable, and a small investment can turn a workspace or kitchen counter into a hub for Android Auto, allowing users to repurpose older devices. To set up Android Auto without a car, you need an Android phone running Android 11 or newer, a spare Android tablet or phone, and a data-capable USB cable. A receiver app, such as Open Headunit or Headunit Reloaded, must be installed on the secondary device. The setup involves connecting the tablet to the phone via USB, selecting Android Auto in the phone's USB options, and following prompts to grant permissions. Android Auto is designed for driving, simplifying interactions with larger controls and allowing voice commands for messages. It can manage smart home devices through Google Home but may not always function reliably. A spare tablet can be positioned conveniently for essential tasks, but trade-offs include limited app availability and the need for the primary phone to remain connected.
Microsoft has expanded its Defender security software to Linux desktop environments, currently in public preview. Microsoft Defender for Endpoint is designed for organizations using Linux workstations and aims to enhance security for developers who interact with sensitive resources. Key features include real-time antivirus protection, endpoint detection and response, threat investigation, vulnerability management, and centralized security monitoring. The software uses the same deployment packages and installation methods as those for Linux servers, supporting distributions like Ubuntu LTS, Debian, Fedora, Red Hat Enterprise Linux, openSUSE Leap, SUSE Linux Enterprise, Rocky Linux, and AlmaLinux. Compatibility with desktop environments is based on the underlying distribution and kernel. The software identifies devices by assessing operating system metadata, and if it cannot classify a machine as a workstation, it defaults to identifying it as a server. This development follows the introduction of Defender for Linux servers in 2020. Organizations need a Microsoft Defender for Endpoint subscription and must meet Linux system requirements to use the software.
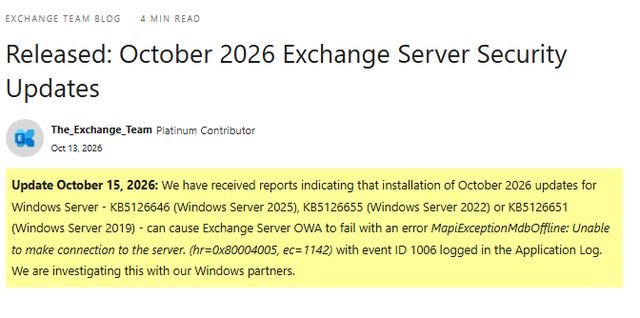
On October 13, 2026, Microsoft released security updates for Windows Server that unintentionally affected Microsoft Exchange Server, causing significant disruptions approximately 24 hours after installation. Users reported issues such as database services failing, resulting in unresponsive email and Outlook Web Access access. Microsoft acknowledged the problem and is investigating it. The updates targeted supported Windows Server and Microsoft Exchange versions 2016, 2019, and SE. By October 15, reports of severe issues, including the inability to connect to the server and halted email delivery, emerged. The error message associated with the disruption is "MapiExceptionMdbOffline: Unable to make connection to the server. (hr=0x80004005, ec=1142)." Despite these issues, the Exchange Admin Center still showed databases as connected and mounted. Unofficial workarounds, including a registry edit and a PowerShell script, have been suggested to mitigate the problems.
The Windows security update scheduled for October 2026 will block requests using the outdated NTLMv1 security protocol. The BlockNtlmSSO registry value governs this change; if unset, Windows will default to Enforce mode, blocking NTLMv1-derived credentials. Administrators can temporarily set this value to 0 to allow NTLMv1, but Microsoft warns this reduces security. The deprecation of NTLM was first announced in 2024, with audit logs for NTLMv1 usage introduced in August 2025. NTLM was first introduced in 1993, and while it has been removed from Windows 11 24H2 and Windows Server 2025, traces remain in certain configurations. Credential Guard must be enabled, and the BlockNtlmSSO value must not be set to Audit mode for NTLMv1-derived credentials to be allowed. Microsoft aims to eliminate NTLM entirely, and the upcoming update signals the need for organizations to accelerate their transition away from NTLMv1.
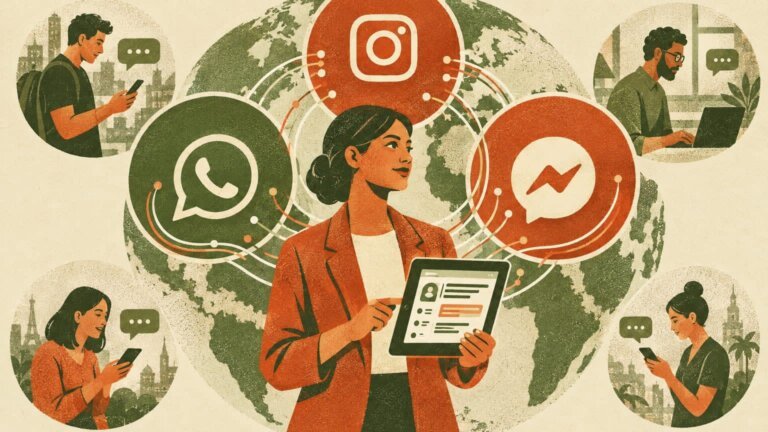
The Meta Enterprise Platform, unveiled on September 28, includes four products: Muse, Meta Business Agent, Muse API, and Muse Code, aimed at enhancing business operations with AI. CJ Desai leads the new business unit, which focuses on providing AI agents and developer tools. The Meta Business Agent has been operational since June, automating customer interactions across WhatsApp, Instagram, and Messenger, while Muse was launched on September 8 as a personal AI agent. Muse API offers programmatic access to Meta's AI models, and Muse Code is a developer tool for coding tasks.
Analysts emphasize Meta's advantage in customer messaging due to its ownership of popular communication channels, but also note concerns about its credibility in the enterprise space, given its lack of foundational business systems. The discontinuation of previous products like Workplace and Horizon Workrooms raises questions about Meta's commitment to enterprise solutions. The platform's pricing strategy may leverage Meta's computing resources, but organizations need to evaluate its effectiveness based on cost per completed tasks. Initial feedback from marketing professionals highlights potential benefits of the Muse platform for smaller enterprises.
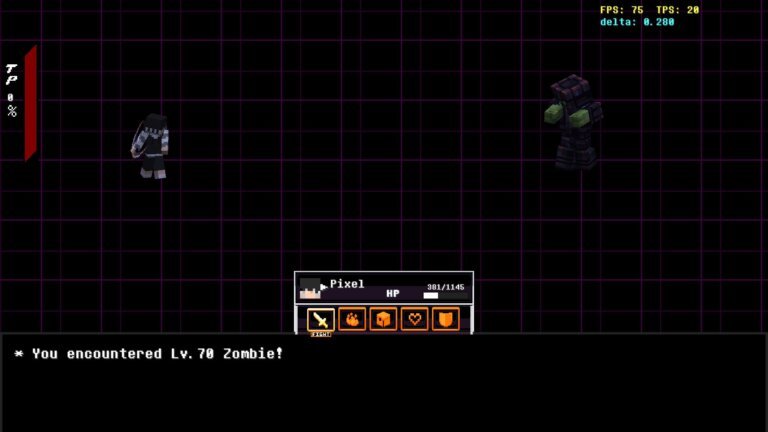
Minecraft's combat mechanics have been considered monotonous, leading players to seek mods for a more dynamic experience. The mod Soulbound, launched by Pixelcite about seven months ago and recently updated to version 2.0, has gained popularity with 140,000 downloads on Modrinth. Soulbound transforms Minecraft into a turn-based RPG inspired by Undertale and Deltarune, allowing players to create characters with customizable stats and combat styles. The mod features original bullet-hell attack patterns and procedurally generated dark worlds that reflect themes from Deltarune. Soulbound was developed without the use of generative AI, as confirmed by moderators on its Discord server.
Windows Server 2022 has transitioned from mainstream support to extended support, which will last until October 2031. Mainstream support will end on October 13, 2026, with the last security update released in that month. Extended support will continue to provide essential security updates at no additional cost until October 14, 2031. Hotpatching for Windows Server 2022 will be available until October 2027 for Datacenter: Azure Edition. Microsoft recommends upgrading to Windows Server 2025, which will have mainstream support until November 2029 and extended support until November 14, 2034. Windows Server 2025 is set for general availability by November 2024. A free 180-day trial of Windows Server 2025 is available. Additionally, devices running Windows 11 24H2 Home and Pro editions will no longer receive updates, and users are advised to upgrade to Windows 11 26H2 to maintain security. Microsoft warns users of unsupported Windows versions to upgrade to avoid losing access to critical security updates after next year's Windows Update certificate rotation.
Microsoft has acknowledged an issue affecting non-admin users connecting to devices via Remote Desktop after recent Windows updates, specifically when the "Administrator protection" feature is enabled. This feature, introduced with the KB5067036 update for Windows 11 versions 24H2 and 25H2 in October 2025, restricts users to standard permissions and requires authentication through Windows Hello for certain actions. Users may encounter connection failures with error code 0xC000000D after applying the KB5124010 September 2026 non-security preview update on systems running Windows 11 versions 24H2, 25H2, 26H1, or 26H2. This issue primarily affects enterprise-managed remote devices configured as Remote Desktop hosts with Administrator protection enabled. Organizations using Windows security baselines have this feature enabled by default unless configured otherwise. A temporary workaround involves disabling Administrator protection, and IT administrators can reset the "User Account Control Type Of Admin Approval Mode" policy using Microsoft Intune or Group Policy. Similar issues have been addressed by Microsoft in the past, including a problem resolved in March 2025 and emergency updates issued last month for Remote Desktop Services failures on Windows Server devices.
Researchers have identified a new Android malware called Hirudo, which steals bank account credentials by replacing legitimate banking applications with modified versions that disable security checks. Hirudo impersonates at least seven banks in Indonesia and targets financial institutions in China, India, Mexico, Morocco, and Thailand. It is delivered through seemingly legitimate applications related to shopping, adult content, or short drama, which prompt users to grant permissions, including Accessibility services.
Once installed, Hirudo uninstalls the genuine banking app, downloads a patched version, and uses Accessibility permissions to complete the installation. The malicious app retains nearly all of the original app's code but integrates a hooking engine based on open-source frameworks YAHFA and Dobby, employing evasion tactics such as substituting signing certificates, concealing Accessibility services, disabling screenshot protection, and altering key-attestation certificates.
Despite its advanced capabilities, Hirudo has limitations, including a publicly leaked attestation keybox and compromised certificates flagged by Google. Once operational, it can extract sensitive information, stream the screen, access cameras, and use fake checkout pages to collect payment PINs while misleading victims with fabricated success messages.
Hirudo represents an escalation in Android banking malware tactics, focusing on the security mechanisms of banking applications. Researchers recommend that banks enhance security measures and that Android users keep devices updated, avoid unofficial APK files, and conduct regular Play Protect scans.