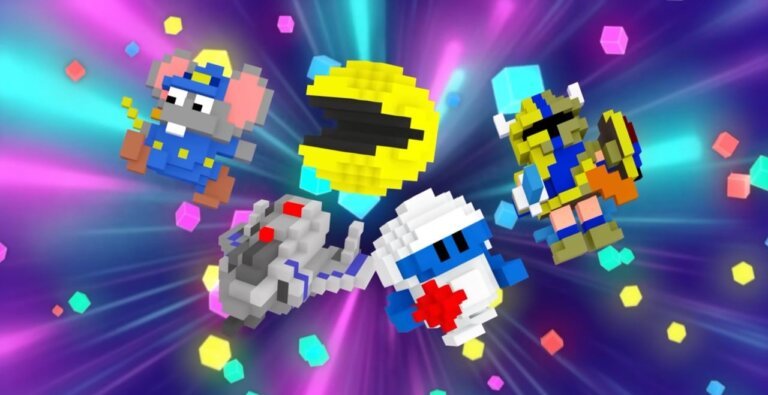
BeXide has released Namco Legendary Mountains on iOS and Android, a Voxel-based puzzler where players match up iconic characters from Namco's classic coin-op era to create chains and prevent a stack from spilling over a bowl's edge.
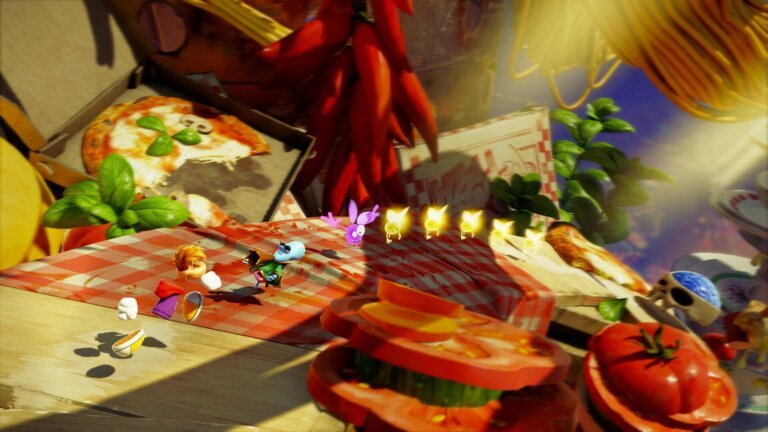
Ubisoft has revealed the system requirements for Rayman Legends Retold on PC, which are significantly higher than those of the original 2013 game. The game will launch on December 3, 2026, for consoles and PC, having experienced a slight delay. The remake features advanced 3D graphics powered by the Snowdrop engine, known for its use in other Ubisoft titles like Star Wars Outlaws and Avatar: Frontiers of Pandora.
Developer Another Angle Games and publisher Owlcat Games announced that the tactical RPG Shadow of the Road will be available for PC on November 12, 2026. The game is set in a war-torn Japan where players form a diverse party to face various adversaries. Players must strategically develop their characters and manipulate the environment during tactical combat. Key features include a story-driven journey, impactful choices, team assembly, and turn-based combat. A demo is currently available on Steam.
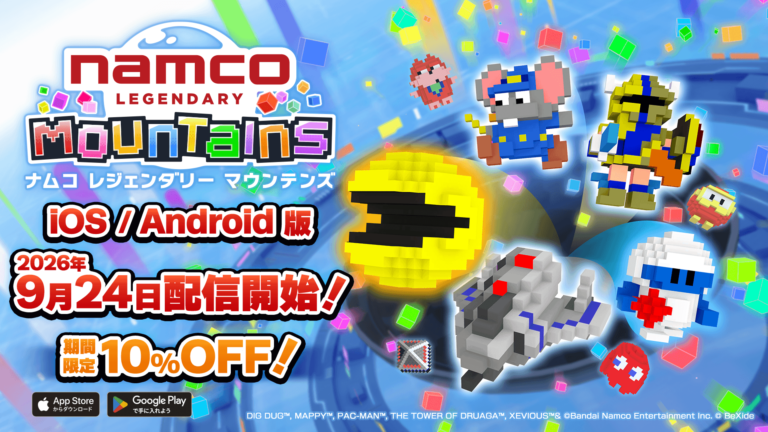
NAMCO LEGENDARY Mountains is a 3D puzzle game set to launch for iOS and Android on September 24, priced at .99. The game features classic Namco arcade games in voxel form, with players tossing, stacking, and merging Voxels to achieve high scores. Key features include dedicated stages and sounds from classic titles like DIG DUG and PAC-MAN, over 100 unique Voxels to collect, and online rankings for score attack.
Microsoft has released preview updates for Windows 11 versions 24H2, 25H2, and 26H1 as part of its Week D schedule. Users of versions 24H2 and 25H2 can install the preview cumulative update KB5124010, updating their systems to builds 26100.9550 and 26200.9550, respectively. Enhancements include refinements to File Explorer, support for Emoji 17.0, a new Tips widget, improved desktop backgrounds, enhanced Bluetooth functionality, upgrades to the Settings app, additional touchpad gesture controls, new key remapping options in Copilot, and Wi-Fi support in the Windows Recovery Environment. The final monthly update for Windows 11 version 24H2 will be shipped next month, with the version set to reach the end of its support lifecycle on October 13, 2026. Users of version 26H1 can install the preview cumulative update KB5124006 to upgrade to build 28000.3086. This update includes a resizable Taskbar, customizable Start menu, revamped Windows Search, improvements to File Explorer, enhanced progress indicators, and better app update support.
Microsoft has informed IT administrators about potential connection challenges with the Always On VPN after the September 2026 Windows 11 security updates. Users may face difficulties connecting to their organization's network, particularly if the VPN is set to automatically attempt an alternative connection method upon failure. Symptoms include connections remaining in a 'Connecting' state or displaying the error message: 'The specified port is already in use.' Affected versions include Windows 11, version 26H1 (KB5124012), version 25H2 (KB5124008), and version 24H2 (KB5124008). A temporary workaround involves adjusting the Always On VPN profile from automatic protocol selection to a single protocol (SSTP or IKEv2). Microsoft is also addressing various other issues related to Hyper-V, Remote Desktop Services, USB audio, and the File History backup feature.
A glitch in Google Maps is affecting Android Auto users, causing the speedometer feature to switch inconsistently between miles per hour (MPH) and kilometers per hour (KPH), regardless of user settings. Reports from users indicate that some see MPH when they prefer KPH and vice versa. The cause of the inconsistency is unclear, though one theory suggests proximity to international borders may be a factor.
A new tool named BigDiskBuster has been released on GitHub, which disrupts Microsoft Defender Antivirus by preventing it from installing updates. It does this by consuming available disk space during the update process, causing Defender to remain on its current version and unable to receive new platform or signature updates. BigDiskBuster operates as a local denial-of-service technique and requires prior access to the target machine to execute. The tool was created by researcher Abdelhamid Naceri, known as Nightmare Eclipse, who has previously worked on similar projects. As of now, there is no CVE identifier, patch, or advisory from Microsoft regarding this issue.
Cisco Talos has disclosed a new Windows implant called CLOSEDQUORUM, which operates without human operators by using four commercial large language models (LLMs) to autonomously decide on actions after deployment. The implant is a 16.4-megabyte executable that conducts reconnaissance on the target system and sends structured prompts to the LLMs, which respond with one of four actions: steal, inject, persist, or move. When the "steal" action is chosen, it simultaneously attacks three credential stores, extracting Windows credentials, browser passwords, and cryptocurrency wallet data. The "inject" action uses either Early Bird APC injection or process hollowing based on model recommendations. For persistence, it employs three overlapping mechanisms, including a Registry Run key, a scheduled task, and a WMI event subscription. To evade detection, CLOSEDQUORUM suppresses ETW telemetry and introduces delays before executing actions. It circumvents traditional command-and-control structures by calling legitimate API endpoints, making blocking these domains impractical. Talos introduced the CAIRN toolkit for detecting AI-integrated malware, which operates on metadata and employs rule-based detection. Unlike previous AI-assisted malware, CLOSEDQUORUM automates decision-making processes entirely, highlighting a significant evolution in malware capabilities. Security teams are advised to focus on behavioral detection strategies and utilize the YARA rule and CAIRN toolkit for identifying this threat.
Cisco Talos has disclosed a Windows implant called CLOSEDQUORUM, which automates cyberattack execution using four advanced commercial large language models: DeepSeek, Qwen, Mistral, and Google Gemini. The implant is a 16.4-megabyte executable that conducts reconnaissance on the system and formats the gathered data into prompts for the AI models. Each model votes on one of four actions: steal, inject, persist, or move, with the action receiving the most votes being executed.
When stealing, CLOSEDQUORUM targets three credential stores, dumping LSASS memory and retrieving saved passwords from browsers and cryptocurrency wallets. The stolen data is encrypted and sent to the operator via Discord. For injection, it uses Early Bird APC injection or process hollowing based on model responses. The persist action creates three mechanisms for longevity, including a Registry Run key, a scheduled task, and a WMI event subscription.
CLOSEDQUORUM evades detection by suppressing ETW telemetry and delaying activity to avoid sandbox analyses. It connects to legitimate API endpoints, making blocking ineffective without disrupting enterprise applications. Talos recommends behavioral combination detection strategies and the use of a YARA rule for detection. The CAIRN toolkit has been introduced to detect AI-integrated malware without executing binaries. Unlike previous AI-assisted malware, CLOSEDQUORUM removes human decision-making from the attack process.