shell

Winsage
September 22, 2026
Changing the desktop wallpaper to a solid color in Windows 7 caused a 30-second delay on the Welcome screen after entering a password. This issue arose because the system waited for a signal from the wallpaper component, which only sent its "I'm ready" signal when an image file was used. When a solid color was selected, this signal was not sent, leading to unnecessary waiting. The problem was acknowledged by Microsoft for both Windows 7 and Windows Server 2008 R2, and it was resolved with a Hotfix update in November 2009. Users found workarounds, such as switching to an image or creating a small solid-color image, to eliminate the delay.
Winsage
September 19, 2026
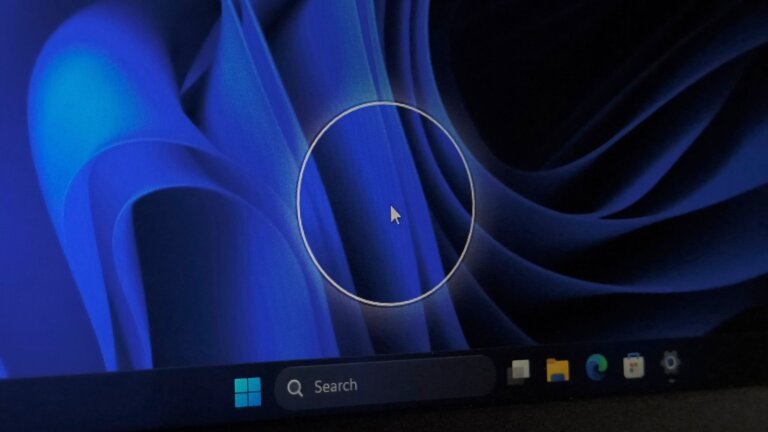
Microsoft has released a modernized version of the Mouse Indicator in Windows 11 Insider Preview Build 26340.9502 on September 18, 2026. This update features a new animation that can be activated through Accessibility settings, allowing users to keep the indicator on until they press the Esc key. Users can choose to activate the Mouse Indicator with a single or double Ctrl press. The previous version displayed a simplistic circle around the pointer briefly, while the new version offers a smoother, more dynamic animation. The feature is currently available only in the Insider build for the Experimental channel, and users can enable it by navigating to Settings > Accessibility > Mouse pointer and touch > Mouse indicator.
AppWizard
September 19, 2026
A new Android malware called RatHat has emerged, analyzed by researchers from Zimperium's zLabs. It spreads through deceptive smishing texts and malicious ads that lead users to counterfeit download pages for popular apps. Once installed, it manipulates Android's Accessibility Service to gain elevated access by enabling Wireless Debugging and retrieving authentication codes without user intervention. RatHat targets finance and banking apps to steal user IDs, passwords, and MFA codes, using techniques to obtain touch coordinates for PIN recovery. It can intercept SMS messages, gain limited control of the device, and reinstall itself. Users are advised against sideloading apps and granting unnecessary accessibility permissions. Google's Advanced Protection Mode and Malwarebytes for Android can help mitigate risks associated with RatHat.
AppWizard
September 19, 2026
Security researchers have identified an Android banking Trojan named RatHat, which utilizes artificial intelligence, accessibility features, and Android Debug Bridge (ADB) to steal financial credentials, PINs, and one-time passcodes. Unlike traditional malware, RatHat employs a live AI assistant that interacts with the Android accessibility tree, allowing it to make real-time decisions based on the victim's screen content. The infection typically starts with social-engineering tactics, leading victims to counterfeit download pages where they are tricked into sideloading a malicious APK. Once installed, RatHat prompts users to enable Android Accessibility Service permissions, which it exploits to navigate Developer Options and enable Wireless Debugging. This grants it shell-level ADB access, allowing it to bypass application sandbox restrictions. RatHat deploys two native binaries for executing commands and maintaining a connection to the attacker's infrastructure. It targets banking applications through credential-stealing overlays and can intercept SMS messages for transaction verification codes. Additionally, it can record touch coordinates to reconstruct PINs and unlock patterns. RatHat includes persistence mechanisms to restore itself after removal, and users are advised to perform a factory reset if they suspect compromise. To reduce infection risk, users should avoid sideloading apps from unknown links, deny unnecessary Accessibility Service requests, and refrain from enabling Developer Options or Wireless Debugging for unfamiliar applications.
AppWizard
September 18, 2026
Cybersecurity experts have identified a new Android malware named RatHat, believed to be operated by Chinese threat actors. RatHat is distributed primarily through smishing and malvertising campaigns, leading users to deceptive download portals. It employs an automated multi-stage infection process and exploits Accessibility features along with a local ADB self-pairing mechanism to escape the Android application sandbox. The malware uses various anti-analysis techniques, including container tampering, manifest bombs, DEX bytecode poisoning, and dual string-encryption. RatHat's architecture consists of a malicious Android application, a Go agent, and an FRP reverse-proxy client, which together enable it to gain critical system permissions and perform various malicious activities such as credential capturing, screen recording, and SMS interception. Even if uninstalled, the malware retains shell access to the device, allowing attackers to reinstall it. RatHat can serialize the device's Accessibility tree to XML and communicate with a Generative AI assistant for tasks like screen coordinate determination and text extraction. The Go Agent, masquerading as a native library, exploits shell access to execute commands and establish a persistent connection to a command-and-control server via the FRP client. The C2 server can issue extensive commands to collect sensitive information, including SMS messages, credentials, files, and keystrokes, and RatHat also features a hardware-level keylogger.
AppWizard
September 17, 2026
Security researchers at Zimperium have identified a new strain of Android malware called RatHat, which is linked to threat actors from China and is designed to steal sensitive credentials and banking information. RatHat infiltrates devices through phishing sites, malvertising, and SMS phishing (smishing), tricking users into downloading malicious Android package kits (APKs). The malware uses a dropper to activate its payload, which is hidden in encrypted assets, and employs techniques to bypass Android's security measures. RatHat consists of three main components: a malicious Android application, a Go agent (liblocal-service.so), and an FRP client (libmedia_codec.so). The app collects sensitive information such as banking credentials, notifications, 2FA codes, OTP keys, and screen inputs. It features a generative AI user interface-automation engine that communicates in Mandarin and can perform various tasks like determining screen coordinates and issuing navigation commands. The Go agent acts as a command-and-control executor, executing commands to bypass app-level security and manage system-level tasks. The FRP client maintains a secure reverse tunnel to the attacker's server, allowing ongoing remote access to the device. The architecture of RatHat demonstrates the inadequacy of traditional mobile security measures against such advanced threats.
Winsage
September 10, 2026
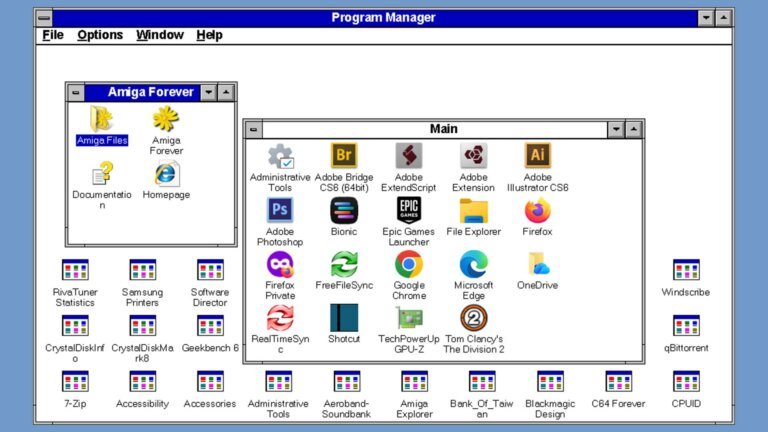
Developer Mayuki has introduced ReProgman, a homage to the classic Windows 3.1 Program Manager ('progman.exe'). The application captures the essence of its predecessor and was created by Claude Code within an hour. The initial version is lightweight, ranging from 12 to 16MB, and requires the .NET SDK 10.0 or higher to build and run. The source code is available on GitHub under the MIT license. Some enthusiasts prefer the authentic experience of running MS-DOS and Windows 3.1 on vintage hardware, with recent demonstrations showing the capability to run Windows 3.1X on modern hardware.
Winsage
September 9, 2026
Microsoft addressed 974 vulnerabilities in its software suite during its recent Patch Tuesday, marking a record high. The breakdown includes 723 flaws in Windows, 111 in Office, 62 in SQL, and 22 in Developer Tools, with over 110 rated as critical. Two actively exploited vulnerabilities are CVE-2026-85880 and CVE-2026-81963, both allowing local privilege elevation. Other notable vulnerabilities include CVE-2026-55007 (8.1), CVE-2026-80097 (8.6), CVE-2026-69465 (8.8), and several with CVSS scores of 9.6 and above. Microsoft has patched a total of 2,760 security flaws this year, reflecting a trend of increasing vulnerability discoveries. Despite the extensive patching, no significant spike in active exploits has been observed.
Winsage
September 8, 2026
Kumander Linux is set to launch version 3.0, built on Debian 13.6 with the Xfce 4.20 desktop environment. It aims to replicate the look and feel of Windows 7 using free and open-source software, including LibreOffice 25.2 and GIMP 3.0.4. The distribution replaces the default Task Manager with a new System Manager and includes an intuitive Software Center. It has a download size of 4.25 GB and requires 11 GB of disk space, consuming approximately 725 MB of RAM when idle. The name "Kumander" references Commodore computers and reflects its Filipino origins. The distribution is currently in its Release Candidate 2 phase.
Search