options are MuMu Player Pro for Apple Silicon Macs, which offers a 7-day free trial and then subscription pricing. KOPLAYER does not have evidence of a maintained paid tier or current official distribution.
DroidDeck differs from Steam Link, GameNative, and Winlator by running games on the phone itself, using FEX to translate x86 PC code for ARM-based Snapdragon chips. DroidDeck also supports GOG, Epic Games, and Amazon Games, installs a Linux desktop mode, Linux apps, emulators, Decky plugins, and LSFG frame generation. DroidDeck is compatible with phones with Adreno 730 or newer GPUs, excluding most Google and Samsung models. To set up DroidDeck, download the APK, install the Linux runtime, adjust developer options, and sign in to Steam.
LDPlayer, MuMu Player, and NoxPlayer are BlueStacks alternatives that are popular among users. LDPlayer and MuMu Player each have roughly 22,200 monthly searches in the US, putting them on par with BlueStacks in search demand. NoxPlayer trails with around 2,400 monthly searches. LDPlayer is marketed towards gamers who want multi-instance farming for mobile RPGs, MuMu Player boasts a newer Android core and high-refresh gaming modes, and NoxPlayer is known for its automation and scripting tools. LDPlayer's latest version is LDPlayer 14, MuMu Player is on version 6.0, and NoxPlayer is still on Android 7. LDPlayer has no native macOS build, MuMu Player has official Windows and macOS installers, and NoxPlayer's macOS build may need to be checked for update recency.
Researchers from Bitdefender have discovered that thousands of inexpensive Android devices are preloaded with malware called "Midnight Mimosa," which generates fraudulent advertising revenue. This malware is embedded in the device firmware before the first power-up, making it impossible for users to uninstall. It operates with system-level privileges, allowing it to install or remove applications without user consent and to download additional code. The malware primarily aims for financial gain through advertising and click fraud, while also gathering information about devices.
Bitdefender has detected this malware on thousands of devices across over 150 countries, with the highest concentrations in Mexico, France, and Italy, followed by the United States, Germany, Brazil, and Spain. Many affected devices are low-cost, white-label, or counterfeit models, often sold online. The malware stealthily installs legitimate-looking applications that display ads in invisible windows, generating ad impressions without user awareness. Bitdefender identified at least 32 disguised applications and found 13 apps in the Google Play Store with similar ad-fraud code.
The source of the malware remains unidentified, but some affected firmware was signed with certificates from Shenzhen Zediel, a Chinese company. The researchers suggest that the malware could have been introduced at various stages of the supply chain, potentially by manufacturers or intermediaries.
LDPlayer, MuMu Player, and NoxPlayer are popular alternatives to BlueStacks in the Android emulator market. LDPlayer and MuMu Player each have a significant number of monthly searches in the US, while NoxPlayer has lower search volume. LDPlayer is focused on multi-instance farming for mobile RPGs, MuMu Player boasts a newer Android core and high-refresh gaming modes, and NoxPlayer is known for automation and scripting tools. LDPlayer's latest version is LDPlayer 14, MuMu Player runs on Android 15, and NoxPlayer is still based on Android 7.
A democratic process has begun to determine the greatest RTS unit, with 16 units competing and eight advancing to the quarterfinals. The initial battles saw the Rohirrim defeat the Psyker and the Warcraft Peon overcome the Glass Dragon. The quarterfinal matchups include:
- Peon (Warcraft 3) vs. Mammoth Tank
- Rohirrim (Battle for Middle-earth) vs. Pride of Hiigara (Homeworld 2)
- Mirage Tank (Command and Conquer: Red Alert 3) vs. Executor Super Star Destroyer (Star Wars: Empire at War)
- Dolphin (Command and Conquer: Red Alert 2) vs. Priest (Age of Empires)
Each unit has distinct characteristics that influence their appeal and strategy in the competition.
Lemuroid is an open-source Android frontend built on top of the Libretro core ecosystem, maintained by developer Swordfish90. It is distributed under the GNU General Public License v3.0 and has 4,371 stars, 366 forks, and 595 open issues on GitHub. Late 2026 is a good time to set it up due to its active development. It is available on Google Play, F-Droid, and GitHub, providing redundancy in case of policy changes. Lemuroid supports twenty systems, each mapped to a specific Libretro core. PlayStation 2, GameCube, and Nintendo Switch are not supported. It requires Android 6.0, 500MB of storage, 3GB of RAM for 8-bit and 16-bit systems, and legally dumped ROMs/ISOs. BIOS files are required for PS1, PSP, and DS cores. It is recommended for managing multiple systems in one library.
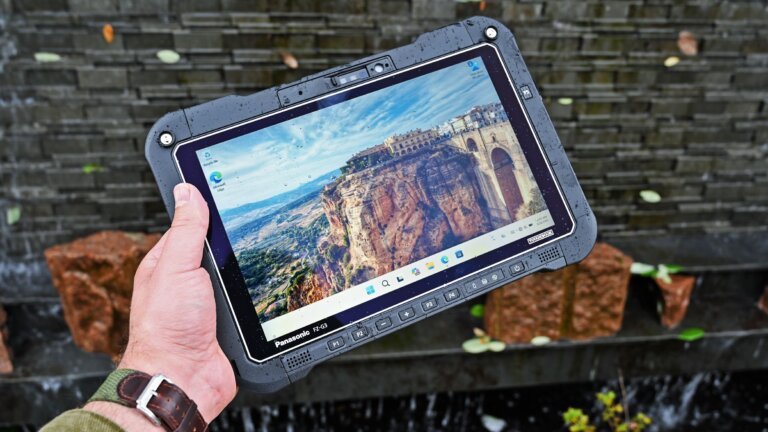
Panasonic's TOUGHBOOK lineup is celebrating its 30th anniversary, with a focus on evolving from rugged devices to intelligent edge computers. The TOUGHBOOK 33 and G3 models feature Intel's latest Core Ultra processors with AI capabilities, enabling local data processing and reducing reliance on cloud connectivity. The TOUGHBOOK 34 has a 12.4-inch display for in-vehicle use, while the G3 is compact with a 10.1-inch display for fieldwork. Both devices support unmanned systems and fleet intelligence applications, allowing for real-time data retrieval and management. The modular xPAK ecosystem enables users to adapt hardware configurations based on specific needs. Connectivity upgrades include 5G support and enhanced Wi-Fi and Bluetooth capabilities. The devices are designed for use in military, emergency response, and utility sectors, emphasizing their role as secure, connected, and AI-capable tools for critical missions.
Researchers at Graz University of Technology discovered significant vulnerabilities in the file-notification subsystems of major operating systems: Linux, Windows, macOS, and Android. These flaws, present for decades, allow side-channel attacks that can infer sensitive information like keystrokes and visited websites. The vulnerabilities are rooted in components such as inotify (Linux, since 2005), FileObserver (Android, since 2008), ReadDirectoryChangesW (Windows, since 2000), and FSEvents (macOS, since 2007). Unprivileged users can exploit these subsystems to observe file events, potentially leading to keystroke timing attacks and credential theft. While Linux has implemented partial mitigations (CVE-2025-68788), Microsoft and Apple have acknowledged the issues but have not provided substantial patches.