signatures

Tech Optimizer
September 23, 2026
A new tool named BigDiskBuster has been released on GitHub, which disrupts Microsoft Defender Antivirus by preventing it from installing updates. It does this by consuming available disk space during the update process, causing Defender to remain on its current version and unable to receive new platform or signature updates. BigDiskBuster operates as a local denial-of-service technique and requires prior access to the target machine to execute. The tool was created by researcher Abdelhamid Naceri, known as Nightmare Eclipse, who has previously worked on similar projects. As of now, there is no CVE identifier, patch, or advisory from Microsoft regarding this issue.
AppWizard
September 23, 2026
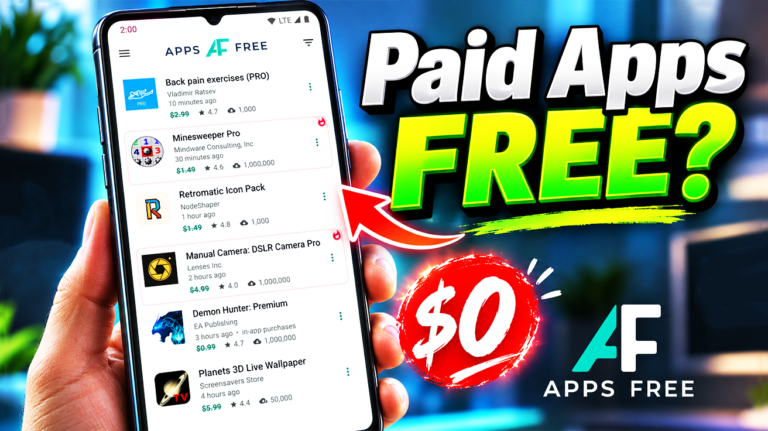
More than 70% of the world’s smartphones operate on the Android platform. Users often struggle to find apps that address specific issues, leading to a time-consuming search through numerous options. A curated list presents five applications that provide practical solutions to common mobile frustrations. 1. AppsFree: Monitors Google Play for premium apps, games, and wallpapers that temporarily drop to free, allowing users to snag deals that would otherwise be missed. Developed by ts-apps GmbH, it enables users to blacklist developers and filter low-quality offers. 2. Monocles Browser: Prioritizes user privacy by disabling JavaScript and cookies by default, reducing tracking. It has an APK size of approximately 13–14 MB and integrates ad blocking and supports Tor/Orbot proxy networks. Created by Arne-Brün Vogelsang, it offers a clean browsing experience. 3. Amarok: Allows users to instantly hide files and applications without resource-intensive encryption by obfuscating filenames and signatures. It supports multiple hiding modes and includes a “panic button” feature for quick data concealment. 4. Buckwheat: Budget manager: Requires manual input of total budget and days to cover, promoting financial reflection. It calculates daily spending allowances and provides detailed analytics. Developed by Danil Zakhvatkin, it has a user rating of around 4.6–4.7/5. 5. Chill Live Wallpaper: Offers minimalist landscapes that sync with local time and weather, providing a visually soothing experience. Compatible with Android 7.1+, it is ad-free and has a compact APK size of 5–6 MB.
Tech Optimizer
September 12, 2026
If you hold Microsoft 365 E5, you already have access to Microsoft Defender for Endpoint, which provides enterprise-grade endpoint protection at no additional cost. For organizations without a dedicated security specialist, Sophos is recommended. CrowdStrike is suitable for those with a mature Security Operations Center (SOC) and sufficient budget. Other options include SentinelOne for mid-sized organizations needing automation, ESET for older hardware and virtual desktops, Avast Business for very small businesses without IT staff, VIPRE for budget-conscious organizations, and Expel for tool-agnostic managed detection and response. It is essential to assess your organization's current situation honestly when evaluating endpoint protection options. Antivirus and EDR are now essentially the same agent, and organizations should inquire about update staging processes and review independent tests for protection rates. Coverage for servers and Linux environments is often overlooked but crucial, as Linux servers are prime targets for ransomware. Key recommendations include: - Microsoft Defender for Endpoint for organizations already on Microsoft 365 E5. - Sophos for organizations with 25-500 staff relying on IT generalists. - CrowdStrike for enterprises with a well-funded security operations function. - SentinelOne for mid-sized organizations needing autonomous operation. - ESET for organizations with older hardware or virtual desktop infrastructure. - Avast Business for micro and small businesses. - VIPRE for budget-conscious organizations. - Expel for those seeking managed detection across various environments. During deployment, avoid running two real-time agents simultaneously, ensure prevention features are activated, and test on line-of-business applications first. Verify update staging and rollback procedures with vendors, and confirm whether Microsoft licensing covers your needs to avoid unnecessary purchases.
Tech Optimizer
September 10, 2026
If you hold Microsoft 365 E5, you have access to Microsoft Defender for Endpoint, which provides enterprise-grade endpoint protection at no additional cost. For organizations without a dedicated security specialist, Sophos is recommended for its user-friendly platform. CrowdStrike is suggested for those with a mature Security Operations Center (SOC) and sufficient budget. Other options include SentinelOne for mid-sized organizations needing automation, ESET for older hardware and virtual desktops, Avast Business for very small businesses, VIPRE for budget-conscious mixed estates, and Expel for tool-agnostic managed detection and response. Antivirus and EDR are now unified under a single agent, and organizations should inquire about update staging processes to avoid issues like those experienced in July 2024 with a major vendor's faulty content update. Independent tests from organizations like AV-Comparatives and AV-TEST are crucial for evaluating protection rates and false positives. Linux servers require attention as they are often targeted by ransomware. When deploying endpoint protection, avoid running two real-time agents simultaneously, activate prevention features promptly, and test deployments on critical applications first. Organizations should confirm their Microsoft licensing covers necessary features and ensure there is a plan for responding to alerts. Common pitfalls include neglecting identity management and failing to test response workflows before incidents occur.
Tech Optimizer
September 10, 2026
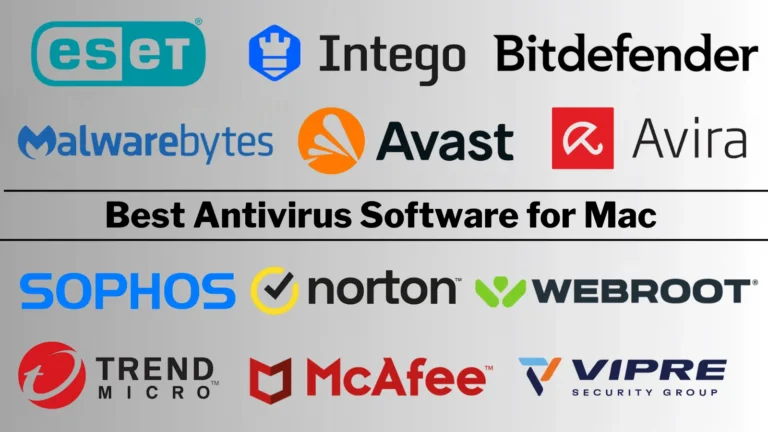
Apple provides built-in security features for macOS, including XProtect, Gatekeeper, and automatic malware removal, which contribute to the safety of Macs. However, these protections do not effectively address threats like infostealers, phishing, and adware. For enhanced security, third-party antivirus solutions are recommended. Bitdefender is noted for its strong detection rates and minimal system impact, making it suitable for most users. Intego specializes in Mac-specific threats and is ideal for users focused solely on Apple products. ESET and Trend Micro are recommended for businesses needing centralized management. F-Secure is recognized for its privacy-focused approach, while Norton offers a comprehensive suite of security features. AVG provides free real-time protection suitable for low-risk personal use, but may not be adequate for business needs. CleanMyMac is a maintenance tool rather than a traditional antivirus, focusing on system cleanup and optimization. Users should avoid running multiple real-time scanners simultaneously and ensure they purchase appropriate licenses for business use. It's important to evaluate the necessity of additional features and consider long-term pricing when selecting antivirus software.
Tech Optimizer
September 10, 2026
Bitdefender is recognized for its strong detection capabilities, mid-range pricing, and minimal system impact. Malwarebytes offers a free scanner for cleaning infected Macs, while Intego specializes in macOS with features tailored for Apple users. Norton provides a comprehensive security package with VPN, backup, and identity monitoring features. Gen Digital owns Norton, Avast, AVG, and Avira, indicating that these brands share threat intelligence and engineering resources. The 2026 Mac Antivirus Scorecard ranks Bitdefender highest with a score of 8.8, followed by Intego (8.2), Malwarebytes (8.3), ESET (8.3), and Norton (7.4). Pricing structures often include discounted first-year rates that can double upon renewal. Free options include Avast and Avira with real-time protection, while Malwarebytes offers a free on-demand scanner. Multi-device licensing can provide better value, and business Macs should use business licenses for essential features. macOS has built-in protections like XProtect and Gatekeeper, but third-party antivirus solutions can enhance security against newer threats.
Winsage
September 9, 2026
Microsoft's September 2026 security update revealed 973 vulnerabilities, with 113 classified as critical. Two actively exploited vulnerabilities are CVE-2026-81963 (Windows Update Stack, elevation of privilege, CVSS 7.8) and CVE-2026-85880 (Windows ALPC, elevation of privilege, CVSS 7.8). Among the 113 critical vulnerabilities, 82 are remote code execution (RCE) vulnerabilities. Notable vulnerabilities include: - CVE-2026-69676: RCE in Windows Kerberos, CVSS 8.8, authentication bypass. - CVE-2026-69852: RCE in Windows RRAS, CVSS 7.5, heap-based buffer overflow. - CVE-2026-72957: RCE in Windows Deployment Services, CVSS 7.8. - CVE-2026-69854: Elevation of privilege in Spring Cloud Azure, CVSS 9.0, improper authentication. - CVE-2026-83501: Information disclosure in Windows VBS, CVSS 5.5. - CVE-2026-69730: RCE in Windows DNS Server, CVSS 9.8. Less likely to be exploited vulnerabilities include: - CVE-2026-69845: RCE in Windows DHCP Server, CVSS 9.8, heap-based buffer overflow. - CVE-2026-65772: Vulnerability in Microsoft Dynamics 365 On-Premises, CVSS 8.8, deserialization of untrusted data. - CVE-2026-66302: RCE in Skype for Business, CVSS 9.8. Additional critical vulnerabilities include: - CVE-2026-62916: Elevation of privilege in Microsoft Entra ID, CVSS 9.1. - CVE-2026-83941: Elevation of privilege in Entra ID, CVSS 9.9. - CVE-2026-80098: Vulnerability in Copilot Studio, CVSS 9.3, improper verification of cryptographic signatures. Talos is releasing a new Snort ruleset to detect attempts to exploit these vulnerabilities, with specific SIDs for Snort 2 and Snort 3 rule coverage.
Search