SMS messages

AppWizard
September 19, 2026
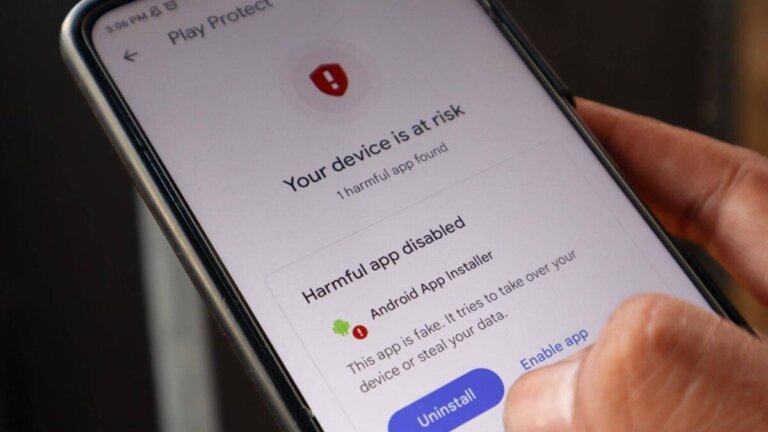
A new Android malware called RatHat has emerged, analyzed by researchers from Zimperium's zLabs. It spreads through deceptive smishing texts and malicious ads that lead users to counterfeit download pages for popular apps. Once installed, it manipulates Android's Accessibility Service to gain elevated access by enabling Wireless Debugging and retrieving authentication codes without user intervention. RatHat targets finance and banking apps to steal user IDs, passwords, and MFA codes, using techniques to obtain touch coordinates for PIN recovery. It can intercept SMS messages, gain limited control of the device, and reinstall itself. Users are advised against sideloading apps and granting unnecessary accessibility permissions. Google's Advanced Protection Mode and Malwarebytes for Android can help mitigate risks associated with RatHat.

AppWizard
September 19, 2026
Security researchers have identified an Android banking Trojan named RatHat, which utilizes artificial intelligence, accessibility features, and Android Debug Bridge (ADB) to steal financial credentials, PINs, and one-time passcodes. Unlike traditional malware, RatHat employs a live AI assistant that interacts with the Android accessibility tree, allowing it to make real-time decisions based on the victim's screen content. The infection typically starts with social-engineering tactics, leading victims to counterfeit download pages where they are tricked into sideloading a malicious APK. Once installed, RatHat prompts users to enable Android Accessibility Service permissions, which it exploits to navigate Developer Options and enable Wireless Debugging. This grants it shell-level ADB access, allowing it to bypass application sandbox restrictions. RatHat deploys two native binaries for executing commands and maintaining a connection to the attacker's infrastructure. It targets banking applications through credential-stealing overlays and can intercept SMS messages for transaction verification codes. Additionally, it can record touch coordinates to reconstruct PINs and unlock patterns. RatHat includes persistence mechanisms to restore itself after removal, and users are advised to perform a factory reset if they suspect compromise. To reduce infection risk, users should avoid sideloading apps from unknown links, deny unnecessary Accessibility Service requests, and refrain from enabling Developer Options or Wireless Debugging for unfamiliar applications.
AppWizard
September 18, 2026
Cybersecurity experts have identified a new Android malware named RatHat, believed to be operated by Chinese threat actors. RatHat is distributed primarily through smishing and malvertising campaigns, leading users to deceptive download portals. It employs an automated multi-stage infection process and exploits Accessibility features along with a local ADB self-pairing mechanism to escape the Android application sandbox. The malware uses various anti-analysis techniques, including container tampering, manifest bombs, DEX bytecode poisoning, and dual string-encryption. RatHat's architecture consists of a malicious Android application, a Go agent, and an FRP reverse-proxy client, which together enable it to gain critical system permissions and perform various malicious activities such as credential capturing, screen recording, and SMS interception. Even if uninstalled, the malware retains shell access to the device, allowing attackers to reinstall it. RatHat can serialize the device's Accessibility tree to XML and communicate with a Generative AI assistant for tasks like screen coordinate determination and text extraction. The Go Agent, masquerading as a native library, exploits shell access to execute commands and establish a persistent connection to a command-and-control server via the FRP client. The C2 server can issue extensive commands to collect sensitive information, including SMS messages, credentials, files, and keystrokes, and RatHat also features a hardware-level keylogger.
AppWizard
September 5, 2026
Audio ducking is a feature in Android Auto that temporarily lowers the volume of the primary app to allow important notifications to be heard clearly. This feature has been part of Android since version 8.0 and is triggered by notifications and navigation prompts. Audio ducking can vary in duration and intensity between different applications. Users can disable notifications for specific apps to prevent audio ducking, but this may result in missing alerts. Additionally, Android 14 introduced hearing safety features that monitor audio levels and lower the volume if prolonged exposure to loud sounds is detected. Users can activate do not disturb mode to silence message notifications, but this won't affect navigation alerts. Audio behavior can also be influenced by settings within the car's audio system. Restarting the device, re-pairing it with the car, or switching cables can resolve connectivity issues.
AppWizard
August 31, 2026
India's cybercrime authorities have warned about the misuse of dating and adult-themed advertisements on social media platforms like Instagram and Facebook, which are being exploited by criminals to distribute malicious Android applications. These ads redirect users to external websites where they are prompted to download APK files, bypassing security measures of trusted app stores. The Indian Cybercrime Coordination Centre (I4C) has identified several malicious applications, including Night Play, Reloop, Kyss, Vimo, Rivo, Nexo, and Vixa, and cautions against installing unfamiliar applications promoted through unsolicited ads. These apps may request sensitive permissions, such as access to SMS messages, contacts, photos, device storage, and Accessibility Services, which can allow fraudsters to access valuable information. Compromised devices can lead to financial fraud by intercepting OTPs and other verification details. The I4C recommends using trusted app stores, keeping Google Play Protect active, reviewing app permissions, and being cautious with social media ads. If a suspicious app is installed, users should restart their phone in Safe Mode to uninstall it, disable its permissions if necessary, and consider a factory reset if removal fails. Users who suspect fraud are encouraged to report incidents promptly.
AppWizard
August 23, 2026
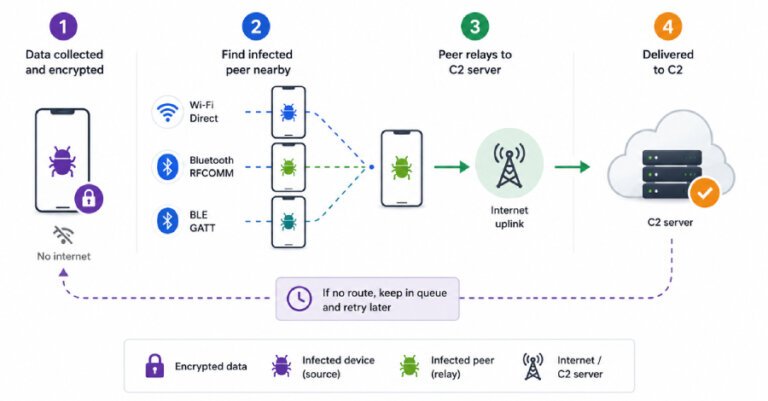
A new Android malware threat, codenamed Manic, poses significant risks to Ukrainian banks, government services, and messaging applications, with a reach extending to Russian and European financial institutions, global fintech platforms, cryptocurrency services, and military communication channels. Manic combines Android banking malware and mobile spyware, targeting sensitive applications and enabling comprehensive device takeover. It features a novel Wi-Fi mesh technique for data relay through compromised devices and utilizes phishing sites and dropper apps. The malware originated in February 2026, with initial development leading to its first deployment by late May. It monitors 169 package IDs related to banks, payment services, and messaging applications, primarily affecting Ukrainian targets but also impacting applications in Russia and Europe. Manic can infiltrate commercial and military messaging apps, track locations, monitor notifications, and collect files. It exploits Android's accessibility services to capture sensitive data and employs a store-and-forward relay mechanism for data exfiltration through nearby compromised devices. Google has stated that no apps containing this malware are found on Google Play, and Android users are protected by Google Play Protect.
BetaBeacon
August 21, 2026
Android is used across a wide range of devices, encouraging developers to create applications for various use cases. Android users can find apps for messaging, video editing, photography, productivity, music, navigation, fitness, education, file management, streaming, social networking, and mobile gaming. Modern phones can run games with console-like graphics, multiplayer systems, cloud synchronization, controller support, and large open worlds. Users can download APK files outside Google Play for various reasons, such as version availability and geographic restrictions. A reliable APK download website should provide detailed information about the application before installation. Users should verify the application name, package name, version, Android compatibility, and permissions before installing an APK. XAPK files package the APK with additional resources required by larger applications or games. Android security is becoming stricter, with more protections around application permissions, background activity, storage access, outdated applications, and unknown installation sources. Access to previous app versions can be useful in case updates introduce issues. Android applications are becoming more powerful, performing tasks that previously required computers, thanks to hardware improvements such as powerful processors, large memory, high-refresh-rate displays, fast storage, and capable GPUs.
Search