social engineering tactics

AppWizard
September 22, 2026
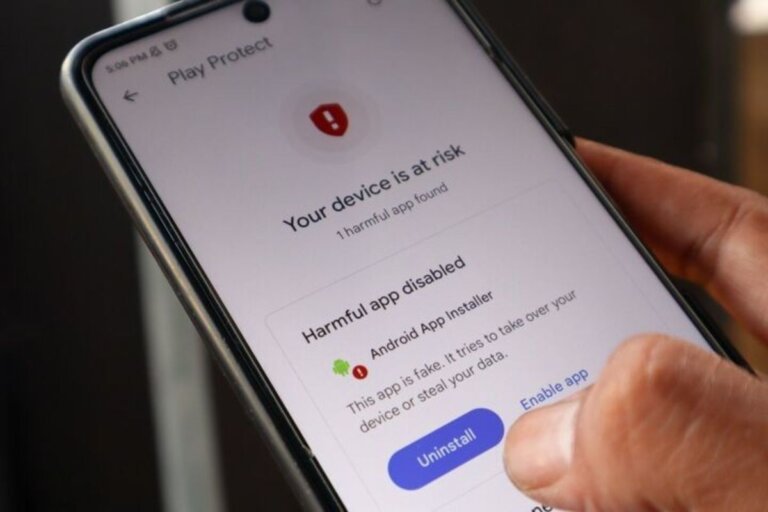
Cybersecurity researchers at Zimperium have identified a new strain of malware called RatHat, targeting Android devices and linked to threat actors from China. RatHat uses generative AI to maintain persistence and control over infected devices. The malware is typically spread through social engineering, tricking users into downloading counterfeit applications that appear legitimate. Once installed, RatHat requests accessibility permissions, activates Wireless Debugging, and can capture text messages, create overlays, and steal passwords and multi-factor authentication codes. Its AI capabilities allow it to navigate the device interface in real-time, making detection by security software more difficult. To protect against RatHat, users should avoid downloading apps from untrustworthy sources, and removal requires a factory reset of the device.
AppWizard
September 14, 2026
Malicious Android applications are being promoted through social media advertisements, particularly on platforms like Instagram and Facebook, posing significant risks to users. The Indian Cyber Crime Coordination Centre (I4C) has warned about deceptive apps advertised under names such as Night Play, Reloop, Kyss, Vimo, Rivo, Nezo, and Vixa, which often redirect users to pornographic websites to download APK files. These applications can exploit sensitive device permissions, leading to malware infections, unauthorized financial transactions, and various forms of cyber fraud. Users may be tricked into granting accessibility permissions that allow the malware to operate in the background and potentially install a VPN, rerouting internet traffic through servers controlled by attackers. Cybersecurity experts advise users to verify the legitimacy of applications before installation and to be cautious of permissions requested by unknown apps.
Tech Optimizer
September 10, 2026
Bitdefender is recognized for its strong detection capabilities, mid-range pricing, and minimal system impact. Malwarebytes offers a free scanner for cleaning infected Macs, while Intego specializes in macOS with features tailored for Apple users. Norton provides a comprehensive security package with VPN, backup, and identity monitoring features. Gen Digital owns Norton, Avast, AVG, and Avira, indicating that these brands share threat intelligence and engineering resources. The 2026 Mac Antivirus Scorecard ranks Bitdefender highest with a score of 8.8, followed by Intego (8.2), Malwarebytes (8.3), ESET (8.3), and Norton (7.4). Pricing structures often include discounted first-year rates that can double upon renewal. Free options include Avast and Avira with real-time protection, while Malwarebytes offers a free on-demand scanner. Multi-device licensing can provide better value, and business Macs should use business licenses for essential features. macOS has built-in protections like XProtect and Gatekeeper, but third-party antivirus solutions can enhance security against newer threats.
Winsage
September 4, 2026
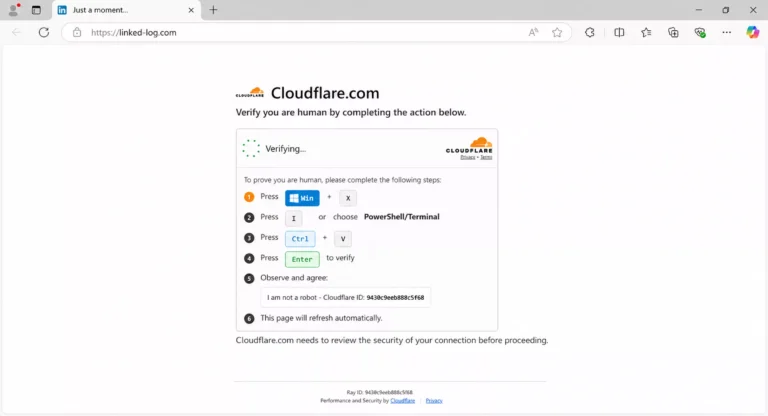
Microsoft has identified a new malware campaign called TerminalFix that uses fake CAPTCHA prompts to trick Windows users into executing malicious commands. This campaign is a variation of ClickFix attacks and employs deceptive pages that impersonate reputable services like Cloudflare. Instead of traditional CAPTCHA challenges, users are instructed to open PowerShell or Command Prompt and paste in commands, allowing attackers to execute complex scripts more easily. TerminalFix initiates a multi-stage intrusion, granting attackers persistent proxy access to the infected machine, which can lead to further exploitation of the company's network. The campaign relies on social engineering tactics, requiring user compliance with counterfeit verification instructions. Microsoft has released mitigation guidance, recommending restrictions on PowerShell access, monitoring for DLL sideloading, blocking outdated Flash plugins, and enabling cloud-delivered protection in Microsoft Defender Antivirus. The campaign poses significant risks to enterprise networks, but individual users should also be cautious about executing commands requested by websites.
AppWizard
August 18, 2026
Most Android users consider third-party antivirus apps unnecessary due to the robust built-in security features of modern Android smartphones. However, Android devices are still vulnerable to viruses, malware, and security breaches, with a 2025 Gen threat report indicating a tripling of malicious push notifications and an increase in spyware issues. Google Play Protect blocked 27 million malicious apps in 2025 and conducts scans to manage security. Android employs sandboxing, regular security updates, and an opt-in permissions system to protect users. Upcoming features include phone call spoofing protection and enhanced live threat detection capabilities. Social engineering tactics, such as phishing and fake tech support calls, pose significant risks that antivirus software cannot address. Connecting to open Wi-Fi networks can expose devices to risks, and malicious push notifications can mislead users. Third-party antivirus apps may be beneficial in high-risk scenarios, such as public Wi-Fi networks or when sideloading apps, providing an additional layer of protection.
Winsage
August 17, 2026
A suspected advanced persistent threat (APT) group linked to China exploited a newly patched vulnerability in VMware vCenter (CVE-2026-59310), which has a critical CVSS score of 9.8, allowing for arbitrary code execution and the deployment of Babuk-derived ransomware. A recently patched vulnerability in Apple macOS (CVE-2026-65400) has been exploited to deploy a cryptocurrency miner, granting unauthorized root access. The Lazarus Group from North Korea exploited a zero-day vulnerability in Microsoft Windows, targeting defense and aerospace sectors. GeoServer patched a critical SQL injection vulnerability that was actively exploited. A new macOS malware, Amnesia Stealer, targets users through ClickFix attacks, stealing data and allowing real-time access to authenticated sessions. A novel attack technique named GhostSplice can manipulate AI coding assistants. Research revealed a method exploiting Chromium's DevTools Protocol for data theft. Noteworthy CVEs this week include CVE-2026-68820, CVE-2026-58231, and multiple others across various platforms. A high-severity command injection flaw in FileRun allows remote code execution. An advanced ClickFix attack has been reported, deploying sophisticated malware. A heap overflow vulnerability in Citrix NetScaler was patched after indications of exploitation. A new malware loader targeting Portuguese-speaking users has been identified. A significant reduction in exposed Automatic Tank Gauge systems has been observed. A phishing campaign targeting Brazil has been detected, and an F.B.I. agent faces charges for unauthorized crypto withdrawals. Authorities in Ukraine dismantled fraudulent call centers, and a North Carolina man was sentenced for cyber extortion. Unauthorized access to sensitive data by the ExfilSquad group has been confirmed. LightSpy activity linked to China has been detected in over 13 countries. A supply chain attack exposed over 2,500 companies, and an Azure exfiltration campaign has exposed millions of enterprise records.
Tech Optimizer
August 16, 2026
The relevance of third-party antivirus software for mobile devices has declined as modern Android devices come with robust built-in security features. Google Play Protect blocks millions of harmful apps and conducts regular scans of installed apps. Android employs sandboxing technology to isolate applications, has a proactive permissions system, and provides regular security updates. While Android is not immune to malware, many threats now arise from social engineering tactics rather than technical vulnerabilities. Users face risks when connecting to public Wi-Fi networks, and malicious push notifications can mislead them. Third-party antivirus may be beneficial for users who sideload apps or notice signs of infection, but for most users, Google's Play Protect suffices. Older devices lacking updates are at higher risk, and while antivirus apps can provide additional protection, education and user vigilance are crucial for minimizing risk.
Search