A study by Proton found tracker code associated with companies in China and Russia in many of the most downloaded free Android games in the US and Europe.
A newly identified strain of Android malware, RatHat, utilizes generative AI to manipulate infected devices in real time. It is linked to threat actors believed to be operating out of China. RatHat serializes the device’s live Accessibility tree into XML format and communicates with a generative AI assistant to return screen coordinates, identify text, and issue navigation commands. The malware employs WebView-based HTML overlays to capture login credentials from banking and cryptocurrency applications and can infiltrate payment apps like WeChat and Alipay to extract PINs. It also features an SMS receiver and notification listener to intercept OTPs and 2FA codes.
RatHat is disseminated through smishing, malvertising campaigns, and misleading third-party forums. It employs anti-analysis techniques such as container tampering, manifest bombing, DEX bytecode poisoning, string encryption, and anti-debugging. Once installed, it gains Accessibility access, activates Developer Options, and enables Wireless Debugging, allowing it to connect to the device's local ADB service and launch control agents with shell-level privileges.
The malware captures raw touch coordinates to reconstruct PINs and unlock patterns, bypassing screenshot protections. It also includes persistence mechanisms that prevent uninstallation by presenting a fake Google Play failure overlay and automatically reinstalling itself if removed.
Scammers are exploiting the Indeed platform to target job seekers by using counterfeit Android "interview" applications. Users in the UK and Brazil reported being instructed by supposed employers to download fraudulent apps like MyInterview, which compromised their devices. These scammers post fake job listings and prompt applicants to install apps that mimic Indeed's login page and establish a VPN connection. The malicious apps, classified as Trojan.Droppers, can install additional untrusted software and gain control over devices, complicating uninstallation efforts. Indeed confirmed that their interview process does not require downloading any separate app and warned job seekers against such scams. Indicators of compromise include specific MD5 hashes and package names associated with the Trojan droppers and dropped malware payloads.
Interactions with antivirus software occur during installation and when issues arise, while the software operates quietly in the background. Modern antivirus solutions continuously monitor for threats using various detection methods, including real-time scanning, which actively scrutinizes files as they are downloaded or accessed.
The signature database is essential for identifying malware by comparing files against known signatures, but it can only detect documented threats. Heuristic detection and behavioral analysis help catch unknown malware by evaluating suspicious characteristics and monitoring file actions during execution.
Sandboxing allows suspicious files to run in a controlled environment, logging their behavior to determine if they are malicious. Quarantine neutralizes threats by locking files in a secure location, allowing users to review them before deletion.
Full scans are resource-intensive and can slow down system performance, while real-time scanning is less demanding. Users can schedule scans during idle times, exclude trusted folders, or consider cloud-based solutions to mitigate performance impacts.
OnyxC2 is a sophisticated credential stealer available for a subscription fee of 0 per month, distributed through disguised lures such as fake Windows updates and legitimate software installers. It functions as a commercial product with features like an automated payload builder, tiered licensing, and a centralized web dashboard. The malware boasts a 99% detection-evasion rate, successfully evading major antivirus solutions during tests. It is developed in C++, utilizing direct system calls and mutating with each build to avoid detection. OnyxC2 collects data from around 210 applications, targeting 45 web browsers, password managers, cryptocurrency wallets, and FTP clients.
The malware is delivered using DLL sideloading, where a password-protected archive contains a legitimate application and a malicious DLL. The attacker's DLL is disguised by inflating its size and is loaded by a trusted binary. The malicious code remains encrypted on disk and decrypts in memory to evade analysis. OnyxC2 communicates with a Cloudflare-fronted command-and-control server to manage infected hosts and execute commands like hardware registration and cookie uploads. The threat extends to business environments, targeting FTP and email clients, with stolen session cookies allowing ongoing access to corporate infrastructure. Implementing anti-data exfiltration controls is recommended as a mitigation strategy.
New variants of the NFCShare Android malware are disguised as fake updates for legitimate banking applications and are targeting customers of various banks in Europe through a phishing campaign to steal sensitive payment card data. The malware prompts victims to place their cards near the NFC chip of their mobile devices, using Android’s IsoDep interface to read card information, including card number, type, expiry date, and a 4-digit PIN. The stolen data is exfiltrated to the attacker’s command-and-control host via a WebSocket channel. Recent attacks began on May 14, with victims directed to a phishing site that impersonates a legitimate bank and then to a GitHub repository hosting a malicious APK file. The repository has hosted 56 unique APKs impersonating banking applications primarily from Italy and Spain. The malware has evolved from initially targeting Deutsche Bank in Germany to a broader range of banks. The latest version features malformed APK packaging to complicate automated analysis. Users are advised to download banking applications only from Google Play and to be cautious of verification requests that ask for NFC card scans.
Microsoft has refreshed its driver documentation for Windows 11 version 26H1, focusing on enhancements within the driver ecosystem rather than user-centric features. The Windows Driver Kit 10.0.28000.1839, released on May 4, 2026, is designated for driver development on this version and supports Visual Studio 2026. Networking drivers have been updated to support WPA3 Compatibility Mode Security, with an upgraded WiFiCx TLV parser and the removal of outdated WDI datapath definitions. The storage driver stack now accommodates SD Ultra Capacity (SDUC) for cards exceeding 2 TB and up to 128 TB. In graphics, kernel header definitions for GPU Process Debug Blob Collection have been introduced, and static analysis integration has been intensified with updated CodeQL suites. These updates aim to prepare the driver base for future hardware demands and improve driver quality and compatibility.
Attackers are using social media advertising, specifically paid Facebook ads, to promote a malware campaign disguised as legitimate Microsoft promotions. They create near-exact replicas of the official Windows 11 download page to lure users into downloading malicious software. The deceptive domains used include ms-25h2-download[.]pro and ms-25h2-update[.]pro. The malware campaign employs geofencing to selectively target victims, redirecting security researchers to benign sites while delivering malware to unsuspecting users. The malicious file, named ms-update32.exe, is hosted on GitHub and mimics the size of a legitimate Windows installer. Once executed, it checks for monitoring tools and, if none are detected, installs an application named "Lunar" that collects sensitive data, including cryptocurrency wallet information. The malware maintains persistence by writing data to the Windows registry and employs various obfuscation techniques to evade detection. The attackers run parallel ad campaigns with different Facebook Pixel IDs to ensure continued operation even if one is suspended. Indicators of compromise include specific file hashes, domains, file system artifacts, and registry keys associated with the malware.
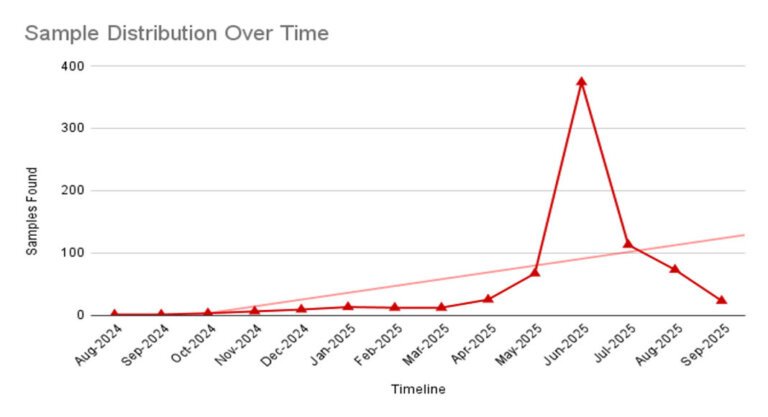
Cybersecurity researchers at zLabs have identified over 760 malicious Android applications that exploit Near Field Communication (NFC) and Host Card Emulation (HCE) technologies to steal payment data and facilitate fraudulent transactions. Since April 2024, these applications have evolved into a coordinated global operation targeting financial institutions in countries such as Russia, Poland, the Czech Republic, Slovakia, and Brazil. The threat actors have established around 70 command-and-control servers and use Telegram bots for data exfiltration. The malicious apps impersonate about 20 legitimate entities, focusing on Russian banks and international institutions like Santander and Google Pay. They utilize various strategies to compromise payment credentials, including scanner and tapper tools, and employ simplified interfaces resembling legitimate banking portals. The malware activates a Host Card Emulation service during NFC payment events for real-time data relay. To evade detection, the threat actors use name masquerading, code obfuscation, and software packing techniques. This campaign represents a significant escalation in NFC-based financial fraud, highlighting the risks associated with NFC payment privileges.
Mobile applications account for 70% of global interactions, with over 6.8 billion smartphone users. In 2023, 40% of data breaches are linked to vulnerabilities in mobile applications. The OWASP Mobile Top 10 outlines critical security risks for mobile apps, including:
1. Improper Credential Usage: Mishandling of passwords and session tokens.
2. Inadequate Supply Chain Security: Risks from unverified third-party components.
3. Insecure Authentication/Authorization: Failures in verifying user identities.
4. Insufficient Input/Output Validation: Lack of checks on incoming and outgoing data.
5. Insecure Communication: Unprotected data during transmission.
6. Inadequate Privacy Controls: Poor safeguards for personal data.
7. Insufficient Binary Protections: Lack of defenses against reverse engineering.
8. Security Misconfiguration: Improperly secured application settings.
9. Insecure Data Storage: Weak protection of sensitive information on devices.
10. Insufficient Cryptography: Use of weak or improperly implemented encryption.
AutoSecT, an AI-driven mobile app security testing platform, detects these risks through various methods, including static code analysis, software composition analysis, and dynamic testing. It helps developers identify and mitigate vulnerabilities effectively.