storyline

AppWizard
September 21, 2026
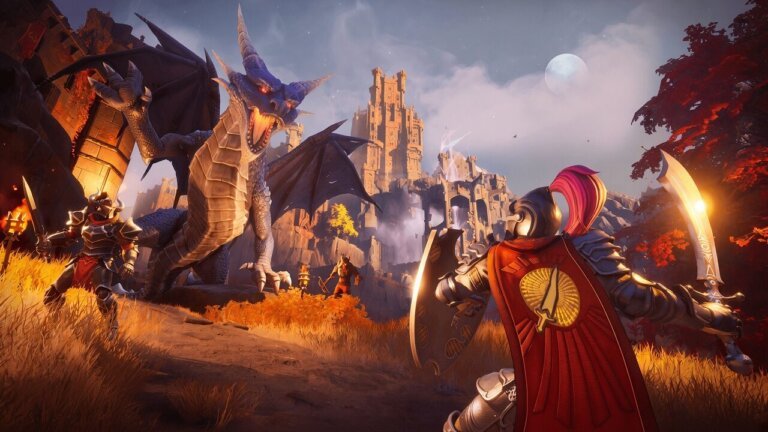
RuneScape: Dragonwilds introduces players to the new continent of Ashenfall, where they face the Dragon Queen Kuldra amidst a significant dragon threat. The game features a new biome called the Scorned Wilderness and a raid-style dungeon, requiring 40 to 60 hours of gameplay to complete its story content. It includes a sophisticated crafting system that allows for extensive customization of the game world. The combat system has been modernized, incorporating various weapon types and a nuanced parrying system, while the magic system offers unique runes that alter spell effects. Players experience skill progression through the use of tools or weapons, but the early game lacks healing potions, making it challenging. The game encourages exploration with a robust crafting system and in-game mounts, as well as the ability to create travel routes using loadstone teleporter panels. It also features dungeons with platforming elements and diverse enemy encounters. RuneScape: Dragonwilds supports full crossplay for consoles and has a roadmap for future updates.
AppWizard
September 20, 2026
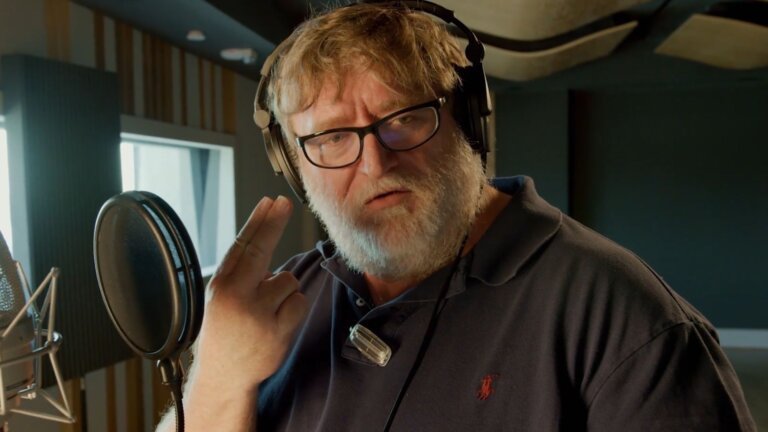
Gabe Newell, co-founder of Valve, spoke at the LBJ School of Public Affairs in 2013 about the relationship between hacking and player engagement in gaming. He highlighted an incident from Ultima Online where the character Lord British was killed during his speech, which led developers to roll back the game instead of embracing the event. Newell argued that recognizing the significance of player-driven narratives could enhance the game's lore and experience, emphasizing the importance of flexibility and creativity in game design. He noted that stories arising from player interactions are often more compelling than those created by developers.
AppWizard
September 16, 2026
Game Source Entertainment, in collaboration with SuperNiche and Clover Lab, is set to release a game titled Noroi Ayashi: The ∞th Oddity in 2027. It is a "time-loop horror RTA stealth action adventure" available on Switch 2, Switch, and PC via Steam, supporting English, Japanese, Traditional Chinese, and Simplified Chinese. The protagonist, Seira, explores her school at night, facing seven mysteries and the curse of a doll named Aya. The narrative is told through Yuriko, a member of the U High School News Club, who investigates the urban legend of the Cursed Doll Aya. Key characters include Seira, Hime, and Tae, each with distinct traits and backgrounds. Gameplay involves navigating the school, avoiding and sealing the Seven Mysteries, and learning from repeated deaths to develop survival strategies. The development team includes Rensuke Oshikiri, known for his work in manga, and Sohei Niikawa, a former Nippon Ichi Software contributor. An announcement trailer has been released.
AppWizard
September 13, 2026
At BlizzCon 2026, it was announced that Diablo 5 will be set a century after Diablo 4, exploring the aftermath of the demon's impact on Sanctuary. The game is projected for release in spring 2029 and aims to address player feedback from Diablo 4. The narrative will feature Diablo as a central character rather than just a final boss, and players will work to restore Westmarch. Key features include procedurally-generated dungeons, a caravan of NPCs instead of traditional towns, returning classes like the demon hunter and monk, and new classes such as the plague knight. The game will launch with more classes than any previous installment, and items will have a tiered system and occupy multiple inventory slots. Blizzard plans to provide regular updates on the game's development starting next year.
Tech Optimizer
September 12, 2026
If you hold Microsoft 365 E5, you already have access to Microsoft Defender for Endpoint, which provides enterprise-grade endpoint protection at no additional cost. For organizations without a dedicated security specialist, Sophos is recommended. CrowdStrike is suitable for those with a mature Security Operations Center (SOC) and sufficient budget. Other options include SentinelOne for mid-sized organizations needing automation, ESET for older hardware and virtual desktops, Avast Business for very small businesses without IT staff, VIPRE for budget-conscious organizations, and Expel for tool-agnostic managed detection and response. It is essential to assess your organization's current situation honestly when evaluating endpoint protection options. Antivirus and EDR are now essentially the same agent, and organizations should inquire about update staging processes and review independent tests for protection rates. Coverage for servers and Linux environments is often overlooked but crucial, as Linux servers are prime targets for ransomware. Key recommendations include: - Microsoft Defender for Endpoint for organizations already on Microsoft 365 E5. - Sophos for organizations with 25-500 staff relying on IT generalists. - CrowdStrike for enterprises with a well-funded security operations function. - SentinelOne for mid-sized organizations needing autonomous operation. - ESET for organizations with older hardware or virtual desktop infrastructure. - Avast Business for micro and small businesses. - VIPRE for budget-conscious organizations. - Expel for those seeking managed detection across various environments. During deployment, avoid running two real-time agents simultaneously, ensure prevention features are activated, and test on line-of-business applications first. Verify update staging and rollback procedures with vendors, and confirm whether Microsoft licensing covers your needs to avoid unnecessary purchases.
Tech Optimizer
September 10, 2026
If you hold Microsoft 365 E5, you have access to Microsoft Defender for Endpoint, which provides enterprise-grade endpoint protection at no additional cost. For organizations without a dedicated security specialist, Sophos is recommended for its user-friendly platform. CrowdStrike is suggested for those with a mature Security Operations Center (SOC) and sufficient budget. Other options include SentinelOne for mid-sized organizations needing automation, ESET for older hardware and virtual desktops, Avast Business for very small businesses, VIPRE for budget-conscious mixed estates, and Expel for tool-agnostic managed detection and response. Antivirus and EDR are now unified under a single agent, and organizations should inquire about update staging processes to avoid issues like those experienced in July 2024 with a major vendor's faulty content update. Independent tests from organizations like AV-Comparatives and AV-TEST are crucial for evaluating protection rates and false positives. Linux servers require attention as they are often targeted by ransomware. When deploying endpoint protection, avoid running two real-time agents simultaneously, activate prevention features promptly, and test deployments on critical applications first. Organizations should confirm their Microsoft licensing covers necessary features and ensure there is a plan for responding to alerts. Common pitfalls include neglecting identity management and failing to test response workflows before incidents occur.
AppWizard
September 10, 2026
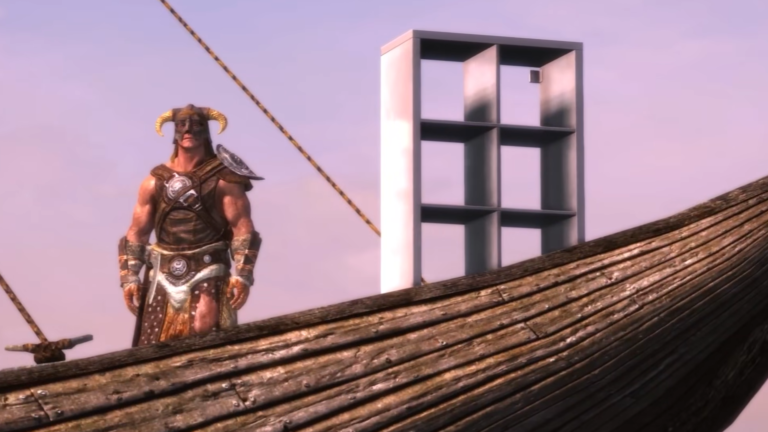
IKEA has created a mod for The Elder Scrolls V: Skyrim™ called Kallax Storageborn, featuring a companion that acts as a shelf and is voiced by Matt Berry. The mod includes a new questline where players visit an abandoned dwemer emporium to uncover the origins of a mysterious master. The quest offers engagement and dialogue, although it is less intricate than those in other games like The Witcher 3. The Kallax Storageborn mod is available for free on Bethesda's Creations page, and YouTuber ESO has streamed a complete playthrough.
AppWizard
September 8, 2026
Grand Theft Auto 6 features a detailed environment where player choices significantly impact the narrative. Unlike previous games, it offers immersive gameplay with various actions reflecting players' moral decisions. Recent leaks reveal chaotic behaviors, such as violent outbursts and confrontations with NPCs, emphasizing player freedom in Vice City. Rockstar Games is not implementing punitive measures for player behavior but instead introduces a 'Criminal Profiles' system categorizing behavior into four states: Professional, Aggressive, Violent, and Psycho, with a fifth state called 'shattered' for disengaged players. Players can disable Criminal Profile notifications for a tailored experience. Protagonists Jason and Lucia can display different Criminal Profile states, influencing their interactions. Maintaining a 'Professional' state requires restraint, encouraging reflection on actions and consequences. Player actions are expected to impact narrative outcomes, with comments from Rob Nelson highlighting the interconnected systems of the game. Players will navigate choices that affect their experience, balancing chaos with a more measured approach.
Tech Optimizer
September 7, 2026
Endpoint detection and response (EDR) continuously records process, file, registry, and network activity on endpoints, applying behavioral analytics to identify attacker techniques while providing tools for investigation and containment. Several EDR platforms have emerged, each catering to different organizational needs: 1. CrowdStrike: Best overall for its rich telemetry and elite threat intelligence. 2. SentinelOne: Best for autonomous response, featuring strong containment and rollback capabilities. 3. Microsoft Defender for Endpoint: Best value for organizations already using Microsoft 365 E5. 4. Palo Alto Cortex XDR: Best for native data fusion across endpoint, network, and cloud telemetry. 5. Sophos: Best for generalist IT teams due to its user-friendly interface. 6. Trend Micro: Best for server and workload coverage, focusing on cloud and hybrid environments. 7. Bitdefender: Best mid-market value with strong detection capabilities at an accessible price. 8. Trellix: Best for organizations already using Trellix products, offering integrated solutions. 9. Huntress Managed EDR: Best for managed endpoint security, ideal for teams lacking full staffing. 10. Cisco Secure Endpoint: Best for Cisco environments, integrating well with Cisco security solutions. Key differentiators among these platforms include the analyst burden, alert management efficiency, and the impact of retention policies on investigation quality. The evaluation of EDR solutions should consider detection depth, response capabilities, operational costs, and the specific needs of the organization.
Search