system access

Winsage
September 23, 2026
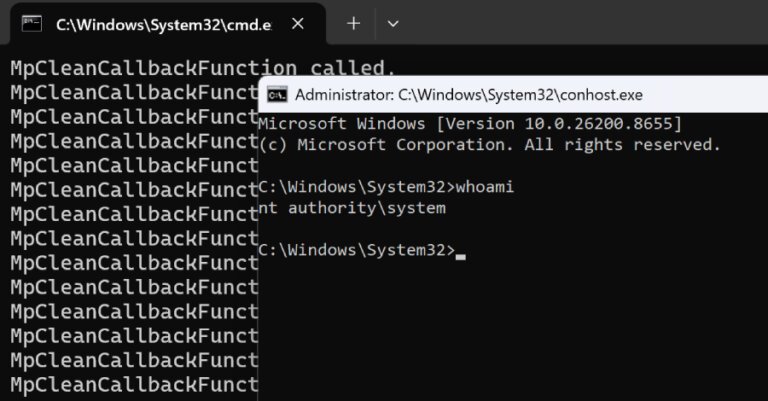
Security researcher Abdelhamid Naceri, known as Nightmare Eclipse, released a zero-day exploit called BigDiskBuster that targets Microsoft Defender, preventing antivirus updates and leaving systems vulnerable. BigDiskBuster operates across all supported Windows versions and must run in the background to block updates. Naceri has previously released a similar exploit called UnDefend and has a history of releasing multiple zero-day exploits since April 2026 amid a dispute with Microsoft. Two weeks before BigDiskBuster, he introduced another exploit named ShieldCrash, which grants SYSTEM access and circumvents a patched flaw. Naceri's recent exploits include tools like LegacyHive, BlueHammer, RedSun, YellowKey, GreenPlasma, and MiniPlasma, all targeting Microsoft Defender and other Windows components. Microsoft has warned of potential legal action against malicious activities but has not commented on BigDiskBuster.
Winsage
September 10, 2026
Microsoft's Patch Tuesday on September 8, 2026, addressed two critical Windows privilege escalation vulnerabilities: CVE-2026-85880 and CVE-2026-81963, both with a CVSS score of 7.8. CVE-2026-85880 is a heap-based buffer overflow in the Windows Advanced Local Procedure Call (ALPC), allowing attackers with low-privilege local access to escalate privileges to SYSTEM. CVE-2026-81963 involves improper link resolution in the Windows Update Stack, enabling similar privilege escalation. Both vulnerabilities require no user interaction and have been actively exploited prior to the patch release. CISA added them to its Known Exploited Vulnerabilities catalog on September 8, 2026, with a remediation deadline of September 22 for U.S. federal agencies. CVE-2026-85880 affects various Windows 10 and Server versions but excludes Windows 11 and Windows Server 2025. CVE-2026-81963 impacts newer Windows platforms, including Windows 11 and Windows Server 2025. Microsoft released security updates for both vulnerabilities on September 8, 2026, and organizations are advised to prioritize these updates. Security teams should monitor for signs of privilege escalation and unusual SYSTEM-level activities related to these vulnerabilities.
Winsage
July 15, 2026
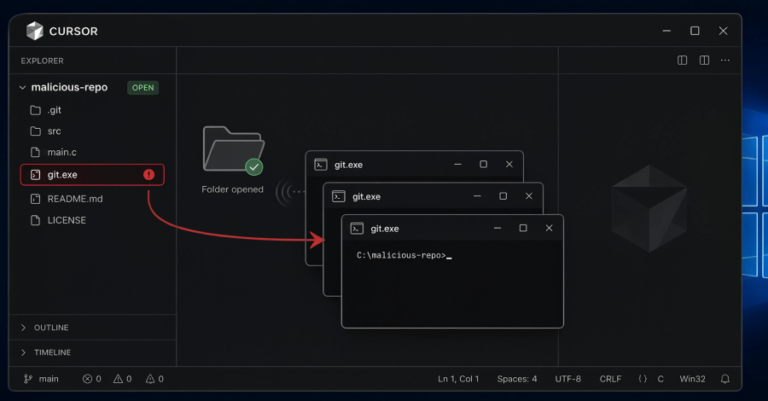
Cursor, a development tool, has a security vulnerability that allows arbitrary code execution by simply opening a project repository on Windows. This flaw, reported by AI security firm Mindgard, is due to the presence of a file named git.exe in the project root, which Cursor executes automatically without user prompts. Mindgard demonstrated this vulnerability by renaming Windows Calculator to git.exe and placing it in the project root, leading to multiple instances of Calculator launching upon opening the repository. Cursor has not yet released a patch or advisory for this issue, which was first reported on December 15, 2025, and remains in the latest version, 3.11, released on July 10, 2026. Users are advised to implement workarounds, such as using AppLocker or Windows App Control to block executables by name and path. Other vendors, including GitHub and Google, have encountered similar vulnerabilities, but none have released fixes. The issue highlights the risks associated with untrusted search paths in software development.
Search