system failures

Tech Optimizer
September 12, 2026
If you hold Microsoft 365 E5, you already have access to Microsoft Defender for Endpoint, which provides enterprise-grade endpoint protection at no additional cost. For organizations without a dedicated security specialist, Sophos is recommended. CrowdStrike is suitable for those with a mature Security Operations Center (SOC) and sufficient budget. Other options include SentinelOne for mid-sized organizations needing automation, ESET for older hardware and virtual desktops, Avast Business for very small businesses without IT staff, VIPRE for budget-conscious organizations, and Expel for tool-agnostic managed detection and response. It is essential to assess your organization's current situation honestly when evaluating endpoint protection options. Antivirus and EDR are now essentially the same agent, and organizations should inquire about update staging processes and review independent tests for protection rates. Coverage for servers and Linux environments is often overlooked but crucial, as Linux servers are prime targets for ransomware. Key recommendations include: - Microsoft Defender for Endpoint for organizations already on Microsoft 365 E5. - Sophos for organizations with 25-500 staff relying on IT generalists. - CrowdStrike for enterprises with a well-funded security operations function. - SentinelOne for mid-sized organizations needing autonomous operation. - ESET for organizations with older hardware or virtual desktop infrastructure. - Avast Business for micro and small businesses. - VIPRE for budget-conscious organizations. - Expel for those seeking managed detection across various environments. During deployment, avoid running two real-time agents simultaneously, ensure prevention features are activated, and test on line-of-business applications first. Verify update staging and rollback procedures with vendors, and confirm whether Microsoft licensing covers your needs to avoid unnecessary purchases.
Tech Optimizer
September 10, 2026
If you hold Microsoft 365 E5, you have access to Microsoft Defender for Endpoint, which provides enterprise-grade endpoint protection at no additional cost. For organizations without a dedicated security specialist, Sophos is recommended for its user-friendly platform. CrowdStrike is suggested for those with a mature Security Operations Center (SOC) and sufficient budget. Other options include SentinelOne for mid-sized organizations needing automation, ESET for older hardware and virtual desktops, Avast Business for very small businesses, VIPRE for budget-conscious mixed estates, and Expel for tool-agnostic managed detection and response. Antivirus and EDR are now unified under a single agent, and organizations should inquire about update staging processes to avoid issues like those experienced in July 2024 with a major vendor's faulty content update. Independent tests from organizations like AV-Comparatives and AV-TEST are crucial for evaluating protection rates and false positives. Linux servers require attention as they are often targeted by ransomware. When deploying endpoint protection, avoid running two real-time agents simultaneously, activate prevention features promptly, and test deployments on critical applications first. Organizations should confirm their Microsoft licensing covers necessary features and ensure there is a plan for responding to alerts. Common pitfalls include neglecting identity management and failing to test response workflows before incidents occur.
Winsage
August 18, 2026
Microsoft has introduced updates in Windows 11 Insider Preview builds, including the removal of the Drag Tray experience and the discontinuation of the Windows Management Instrumentation Command-line (WMIC) tool. The Windows Recovery Environment (WinRE) has been upgraded to improve connectivity options, allowing users to automatically utilize eligible saved Wi-Fi profiles, including those with certificate-based authentication. Previously, WinRE's networking capabilities were limited, requiring manual connections for certain networks. This enhancement is currently being rolled out to Windows 11 Beta Insiders and is expected to be available to broader Windows 11 version 26H2 users later this year.
Winsage
August 6, 2026
Windows operating systems have hidden functionalities and privacy enhancements introduced through regular updates, which are crucial for maintaining system security. Neglecting updates leaves known vulnerabilities open to exploitation by malicious actors, as Microsoft typically addresses security flaws only after they are identified. Windows Update is the primary mechanism for addressing these vulnerabilities. Unpatched systems become targets for cyber threats, leading to severe consequences such as remote code execution, privilege escalation, ransomware attacks, and boot-level compromises. The PrintNightmare vulnerability (CVE-2021-34527) was acknowledged by Microsoft after active exploitation was detected, leading to the release of patches. The WannaCry cyberattack in May 2017 affected over 300,000 computers due to an unpatched SMB flaw, highlighting the risks of outdated systems. Timely updates can prevent vulnerabilities that may lead to ransomware, credential theft, and other compromises. Users are advised to install updates promptly and avoid connecting unsupported versions to the internet.
Winsage
July 10, 2026
Microsoft has acknowledged a significant issue affecting Windows 11 users on versions 24H2 and 25H2, where a bug can consume up to 500GB of storage, leading to critical space shortages and potential system failure. This bug has been reported since May 2025, with a solution disclosed on June 29, but it will not be automatically rolled out until July 14. Users can check if they are affected by navigating to Settings > System > Storage and examining the “System files” category; if it exceeds 100GB, they are likely impacted. The issue is linked to a hidden file named CapabilityAccessManager.db-wal in the “%ProgramData%MicrosoftWindowsCapabilityAccessManager” directory. Microsoft has released an optional update (KB5095093) to address the bug, which also includes feature previews that may affect performance. Users are advised against deleting the problematic file to avoid disrupting WiFi connectivity and screen capture functionalities. An automatic fix will be deployed during the July 14 update.
Winsage
July 8, 2026
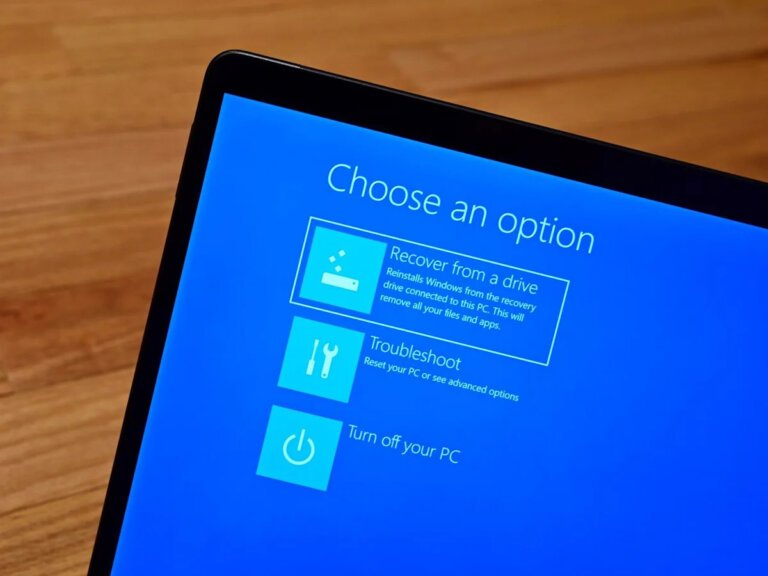
Microsoft is previewing a recovery tool called Cloud rebuild for Windows 11, which allows for a clean reinstallation of the operating system even if it fails to boot. This tool automatically downloads the latest updates and drivers, eliminating the need for manual installations after recovery. Unlike the existing "Reset this PC" feature, Cloud rebuild does not retain personal files, settings, or applications, requiring users to restore these independently. To use Cloud rebuild, users need the latest Windows 11 insider build (Preview Build 26300.8772 or higher) and must follow specific steps in the Windows Recovery Environment. The timeline for broader availability of Cloud rebuild is uncertain, depending on ongoing testing and feedback. Other recovery options in Windows 11 include recovery drives, reset functions, Quick Machine Recovery, and a testing feature called Point-in-Time restore.
Winsage
July 7, 2026
Microsoft has introduced a new recovery solution for Windows 11 users called Cloud Rebuild, which allows for the reinstallation of the operating system directly from the cloud, restoring a PC to a clean state. This feature downloads the Windows OS and necessary device drivers, enabling recovery even when the OS is unbootable, unlike the existing Reset this PC option. However, Cloud Rebuild does not retain applications and files during the process. Currently, it is being rolled out in preview to Windows Insiders and is expected to be available to the general public in the coming months.
Search