tactics

Tech Optimizer
September 29, 2026
Traditional antivirus software relies on a signature-based model that compares files against a database of known malware, which limits its effectiveness against modern threats. Cybercriminals have adapted by using polymorphic malware and fileless techniques that evade detection. Endpoint Detection and Response (EDR) continuously monitors device activities, tracking process activity, network connections, and file changes to detect behavioral patterns indicative of attacks. EDR also enables rapid response actions, such as isolating affected devices and terminating malicious processes. Small and medium businesses are increasingly targeted by attackers who exploit the limitations of traditional antivirus solutions. Relying solely on antivirus software creates vulnerabilities, making it essential for organizations to incorporate EDR for enhanced security.
AppWizard
September 27, 2026
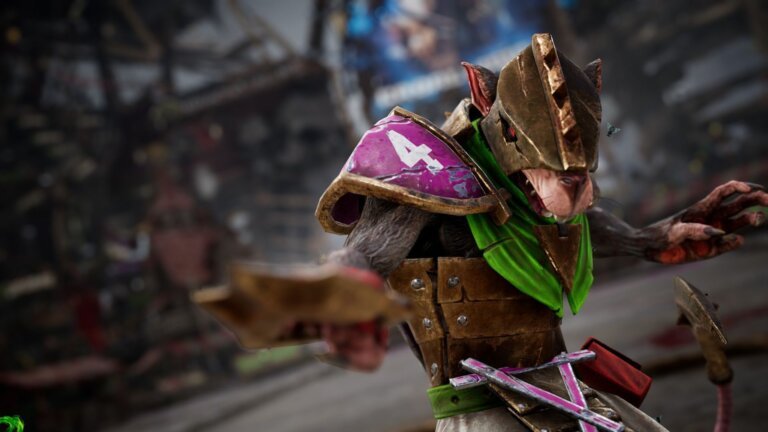
A significant majority of players engage with Blood Bowl 3 in solo mode, with 70 to 80% of games played in the Eternal Leagues being solo endeavors. The game is set to transition to Warhammer Blood Bowl, which will feature a more sophisticated AI and a revamped user interface. The new version will be available as a free upgrade for existing owners of Blood Bowl 3 and is scheduled for release by the end of the year.
Tech Optimizer
September 26, 2026
Endpoint security is a suite of technologies and processes designed to protect devices connected to a business network from cyber threats. It includes various devices such as laptops, smartphones, tablets, servers, and IoT devices. Endpoint security employs a multi-layered approach, scanning for malware, regulating applications, and monitoring device activity for unusual behavior. It is distinct from antivirus software, encompassing a broader range of protective measures, including firewalls, encryption, application controls, patch management, and Endpoint Detection and Response (EDR). The rise of remote work and the increasing number of devices create a larger attack surface, making endpoint security essential for preventing breaches and safeguarding business operations.
Tech Optimizer
September 25, 2026
Cybercriminals have developed an infostealer called MacSync, targeting Mac devices by using iCloud calendar events and cloud storage. This malware disguises itself as fake cryptocurrency wallets and pirated software. It begins with a loader that retrieves instructions from calendar entries and deploys malware to exfiltrate sensitive information, including credentials and cryptocurrency wallets. Recent versions have introduced an Objective-C backdoor that mimics Finder. Victims are often tricked into downloading these malicious applications, and effective antivirus solutions can prevent damage. Cybercriminals use tactics like SEO poisoning and phishing to direct victims to fraudulent websites or social media promoting pirated software. In one case, the loader was marketed as a cryptocurrency wallet, and victims encountered a misleading ClickFix error message that prompted them to execute a command in the Terminal.
AppWizard
September 24, 2026
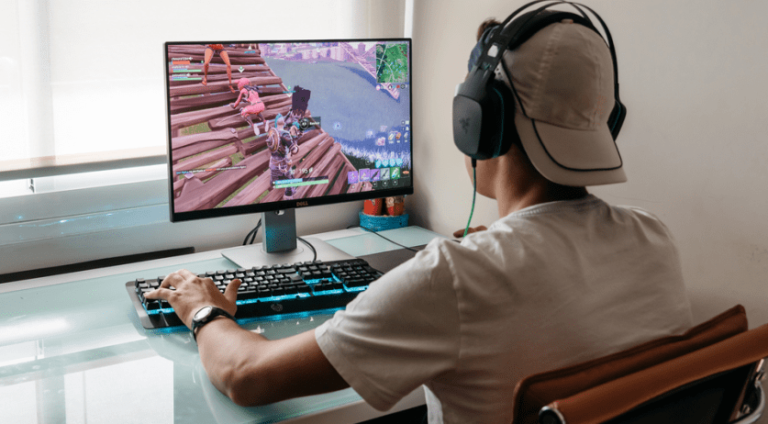
The Massaschade & Consument Foundation has filed a lawsuit against Epic Games, alleging that Fortnite uses deceptive marketing tactics targeting younger players. The foundation claims that countdown clocks during gameplay create a false sense of urgency for limited-time offers, which often remain available after the timers expire, leading to confusion and potential overspending. The lawsuit raises ethical concerns about the responsibility of game developers to protect young gamers. The outcome could impact marketing strategies and consumer protection laws in the gaming industry.
AppWizard
September 22, 2026
Cybersecurity researchers at Zimperium have identified a new strain of malware called RatHat, targeting Android devices and linked to threat actors from China. RatHat uses generative AI to maintain persistence and control over infected devices. The malware is typically spread through social engineering, tricking users into downloading counterfeit applications that appear legitimate. Once installed, RatHat requests accessibility permissions, activates Wireless Debugging, and can capture text messages, create overlays, and steal passwords and multi-factor authentication codes. Its AI capabilities allow it to navigate the device interface in real-time, making detection by security software more difficult. To protect against RatHat, users should avoid downloading apps from untrustworthy sources, and removal requires a factory reset of the device.
Tech Optimizer
September 21, 2026
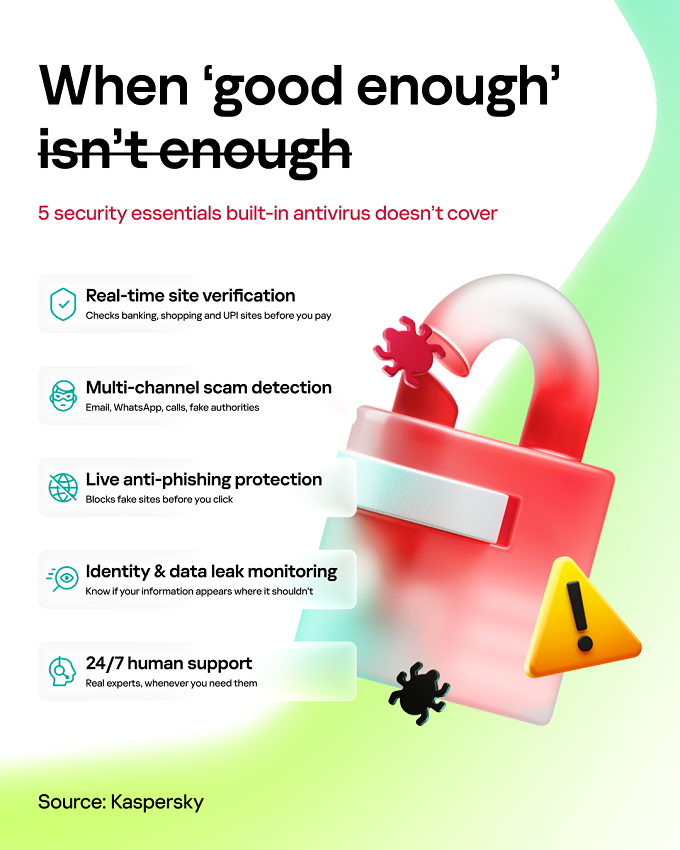
The landscape of computer security has changed significantly over the past two decades. In 2026, antivirus protection remains important, but the need for separate third-party programs has decreased for many users due to the built-in Microsoft Defender in Windows 11, which is activated by default and effectively blocks 100% of common malware samples according to independent testing by AV-TEST. Windows 11 also includes additional protective features like SmartScreen and a robust Firewall. While dedicated security suites from companies like Norton and Bitdefender offer advanced functionalities, many users may find adequate protection with the built-in tools. Research from AV-Comparatives indicates that performance varies among security programs, particularly against real-world attacks. Phishing attacks accounted for approximately 60% of initial access points in incidents examined by the ENISA Threat Landscape report from 2025, highlighting that user behavior is a significant vulnerability. Modern web browsers and operating systems have enhanced their security measures, with Google Chrome, Microsoft Edge, macOS, and Android incorporating features to protect users from harmful websites and downloads. For the average Windows 11 user who keeps their system updated and practices safe browsing, built-in protection is generally sufficient, though paid antivirus options can provide additional tools.
Search