telemetry

AppWizard
September 21, 2026
In August 2026, Google Play announced new performance requirements for memory management that will be enforced starting February 2027. These requirements include metrics for dynamic memory usage, bitmap memory, and DEX code optimization. Applications that exceed these thresholds may face reduced visibility and publishing capabilities on the platform. Dynamic memory usage is defined as the sum of anonymous RSS and swap, excluding file-backed data. Google is focused on whether applications retain non-visible bitmaps and requires at least 25% coverage in DEX optimization. Memory issues can be difficult to reproduce, and developers are encouraged to use Android Studio’s Memory Profiler to investigate memory growth. A thorough investigation involves monitoring memory changes, taking heap dumps, and understanding reference paths. Bitmap memory should be carefully managed, as the runtime cost of images can exceed their file size. Google will provide real-world memory metrics through the Play Console, and teams are advised to establish memory budgets and perform pre-release checks to identify potential issues before they lead to out-of-memory (OOM) crashes.
AppWizard
September 20, 2026
The growing interest in minimalist phones, or "dumbphones," is prompting users to seek ways to transform existing smartphones into more focused devices. Key strategies include managing notifications by turning off alerts for most apps and allowing only essential updates, utilizing app blockers like Switchly to limit distractions from social media, and employing BlockAds to eliminate intrusive ads. Users can also opt for minimalist, ad-free versions of apps, such as the Fossify suite for essential functions and Breezy Weather for weather updates. Customizing the home screen to reduce clutter, such as simplifying it to a single page and disabling unnecessary widgets, can further enhance focus. Additionally, customizing popular apps like Chrome, Gmail, and Google Maps by disabling features and notifications helps create a calmer experience. Overall, intentional choices and the right tools can lead to a more serene smartphone environment.
Winsage
September 17, 2026
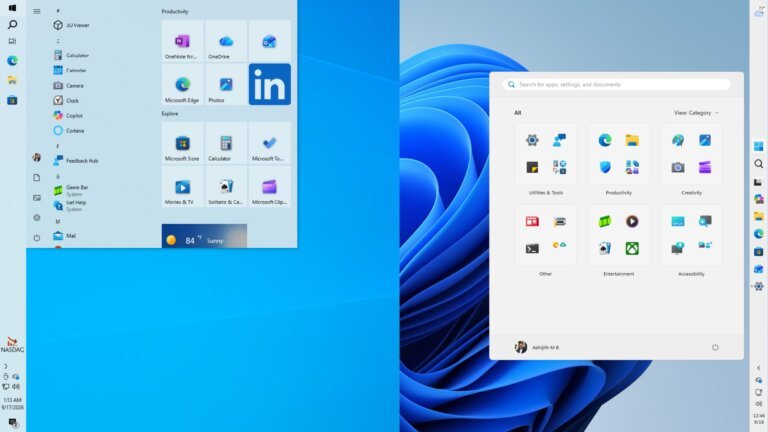
Windows 11 was released in 2021 and received mixed reactions, with users noting the removal of several familiar features from Windows 10. The taskbar was locked in place, preventing repositioning, and the ability to drag files onto taskbar applications was initially absent but restored within a year. The Start menu lost flexible resizing options, and Microsoft faced challenges in transferring established features due to the new framework. By 2026, Microsoft announced changes allowing users to relocate the taskbar, responding to user demand. The Start menu remained less flexible than its predecessor, leading to user frustration. Microsoft acknowledged the need for a movable taskbar, which was implemented in a preview by May 2026, coinciding with the September 2026 Patch Tuesday update. The integration of AI into development processes has accelerated feature implementation, but also introduced new stability issues.
Tech Optimizer
September 14, 2026
The encryption landscape has shifted significantly, with Microsoft’s BitLocker and Apple’s FileVault becoming the primary free and integrated solutions for disk encryption. Organizations are encouraged to focus on comprehensive management capabilities rather than just acquiring encryption technology. Key management, compliance proof for auditors, and consistent policy enforcement across devices are critical. Native encryption solutions do not provide fleet-wide compliance, centralized key escrow, or advanced pre-boot authentication options. Various management models exist for different organizational needs, including options from Microsoft, Sophos, ESET, Trend Micro, Check Point, Trellix, WinMagic, Broadcom (Symantec), Dell, and Kaspersky. It is essential to ensure proper key management and recovery procedures before enforcing encryption to avoid data loss. Organizations should verify claims of compatibility and effectiveness of encryption solutions, especially regarding pre-boot authentication and cryptographic standards. Native encryption solutions are free, but management layers typically incur costs. Open-source solutions like VeraCrypt lack necessary management features, making them impractical for businesses.
Tech Optimizer
September 13, 2026
The landscape of encryption engines has stabilized, with Microsoft BitLocker and Apple FileVault being the primary solutions. As of 2026, the emphasis is on management rather than just acquiring encryption technology. Key management elements include audit proofing, key escrow and recovery, policy enforcement, and pre-boot options. Native encryption solutions lack features such as fleet-wide compliance proof, centralized key escrow, consistent policy enforcement, advanced pre-boot authentication, and removable-media encryption. Various management models are available for different environments, including: 1. Microsoft BitLocker with Intune: Free for Windows Pro/Enterprise, integrates with Entra ID for key management. 2. Sophos: Manages both BitLocker and FileVault from a single console. 3. ESET: Offers lightweight management and removable-media protection. 4. Trend Micro: Integrates encryption with DLP capabilities. 5. Check Point: Provides advanced pre-boot options and policy management. 6. Trellix: Comprehensive enterprise encryption suite with a complex management interface. 7. WinMagic: Focuses on cross-platform encryption and strong pre-boot options. 8. Broadcom (Symantec): Manages native engines within its broader security framework. 9. Dell: OEM-integrated encryption management for Dell hardware. 10. Kaspersky: Provides encryption management but is restricted in the U.S. Key considerations before deploying encryption include ensuring key escrow is in place, conducting recovery tests, and being mindful of removable media and server encryption. Common mistakes include using outdated freeware and not verifying key escrow. Organizations should request auditor reports for compliance verification and confirm claims of compatibility and pre-boot functionality. Native encryption engines are free, while management layers typically charge on a per-endpoint basis.
Tech Optimizer
September 12, 2026
If you hold Microsoft 365 E5, you already have access to Microsoft Defender for Endpoint, which provides enterprise-grade endpoint protection at no additional cost. For organizations without a dedicated security specialist, Sophos is recommended. CrowdStrike is suitable for those with a mature Security Operations Center (SOC) and sufficient budget. Other options include SentinelOne for mid-sized organizations needing automation, ESET for older hardware and virtual desktops, Avast Business for very small businesses without IT staff, VIPRE for budget-conscious organizations, and Expel for tool-agnostic managed detection and response. It is essential to assess your organization's current situation honestly when evaluating endpoint protection options. Antivirus and EDR are now essentially the same agent, and organizations should inquire about update staging processes and review independent tests for protection rates. Coverage for servers and Linux environments is often overlooked but crucial, as Linux servers are prime targets for ransomware. Key recommendations include: - Microsoft Defender for Endpoint for organizations already on Microsoft 365 E5. - Sophos for organizations with 25-500 staff relying on IT generalists. - CrowdStrike for enterprises with a well-funded security operations function. - SentinelOne for mid-sized organizations needing autonomous operation. - ESET for organizations with older hardware or virtual desktop infrastructure. - Avast Business for micro and small businesses. - VIPRE for budget-conscious organizations. - Expel for those seeking managed detection across various environments. During deployment, avoid running two real-time agents simultaneously, ensure prevention features are activated, and test on line-of-business applications first. Verify update staging and rollback procedures with vendors, and confirm whether Microsoft licensing covers your needs to avoid unnecessary purchases.
Tech Optimizer
September 11, 2026
Microsoft BitLocker and Apple FileVault are free, integrated encryption solutions within their respective operating systems. As of 2026, the focus is on investing in management solutions that provide compliance proof, key escrow, recovery options, and policy enforcement across devices. Native encryption solutions lack certain management features, prompting the need for additional management layers from various vendors. Legacy freeware like TrueCrypt is no longer maintained, posing risks for business use, while VeraCrypt is a credible open-source alternative but lacks centralized management. Management options include Microsoft Intune for Windows, Sophos for mixed fleets, and specialized providers like Check Point and WinMagic for advanced needs. Organizations should ensure proper key management before enforcing encryption to avoid data loss and regularly test recovery processes. It is crucial to verify claims regarding compatibility and pre-boot options when selecting encryption solutions. Native engines are free, but management layers typically charge per endpoint annually.
Tech Optimizer
September 10, 2026
If you hold Microsoft 365 E5, you have access to Microsoft Defender for Endpoint, which provides enterprise-grade endpoint protection at no additional cost. For organizations without a dedicated security specialist, Sophos is recommended for its user-friendly platform. CrowdStrike is suggested for those with a mature Security Operations Center (SOC) and sufficient budget. Other options include SentinelOne for mid-sized organizations needing automation, ESET for older hardware and virtual desktops, Avast Business for very small businesses, VIPRE for budget-conscious mixed estates, and Expel for tool-agnostic managed detection and response. Antivirus and EDR are now unified under a single agent, and organizations should inquire about update staging processes to avoid issues like those experienced in July 2024 with a major vendor's faulty content update. Independent tests from organizations like AV-Comparatives and AV-TEST are crucial for evaluating protection rates and false positives. Linux servers require attention as they are often targeted by ransomware. When deploying endpoint protection, avoid running two real-time agents simultaneously, activate prevention features promptly, and test deployments on critical applications first. Organizations should confirm their Microsoft licensing covers necessary features and ensure there is a plan for responding to alerts. Common pitfalls include neglecting identity management and failing to test response workflows before incidents occur.
Search