trojan

AppWizard
September 19, 2026
A new Android malware called RatHat has emerged, analyzed by researchers from Zimperium's zLabs. It spreads through deceptive smishing texts and malicious ads that lead users to counterfeit download pages for popular apps. Once installed, it manipulates Android's Accessibility Service to gain elevated access by enabling Wireless Debugging and retrieving authentication codes without user intervention. RatHat targets finance and banking apps to steal user IDs, passwords, and MFA codes, using techniques to obtain touch coordinates for PIN recovery. It can intercept SMS messages, gain limited control of the device, and reinstall itself. Users are advised against sideloading apps and granting unnecessary accessibility permissions. Google's Advanced Protection Mode and Malwarebytes for Android can help mitigate risks associated with RatHat.

AppWizard
September 19, 2026
Security researchers have identified an Android banking Trojan named RatHat, which utilizes artificial intelligence, accessibility features, and Android Debug Bridge (ADB) to steal financial credentials, PINs, and one-time passcodes. Unlike traditional malware, RatHat employs a live AI assistant that interacts with the Android accessibility tree, allowing it to make real-time decisions based on the victim's screen content. The infection typically starts with social-engineering tactics, leading victims to counterfeit download pages where they are tricked into sideloading a malicious APK. Once installed, RatHat prompts users to enable Android Accessibility Service permissions, which it exploits to navigate Developer Options and enable Wireless Debugging. This grants it shell-level ADB access, allowing it to bypass application sandbox restrictions. RatHat deploys two native binaries for executing commands and maintaining a connection to the attacker's infrastructure. It targets banking applications through credential-stealing overlays and can intercept SMS messages for transaction verification codes. Additionally, it can record touch coordinates to reconstruct PINs and unlock patterns. RatHat includes persistence mechanisms to restore itself after removal, and users are advised to perform a factory reset if they suspect compromise. To reduce infection risk, users should avoid sideloading apps from unknown links, deny unnecessary Accessibility Service requests, and refrain from enabling Developer Options or Wireless Debugging for unfamiliar applications.
AppWizard
September 11, 2026
The Cybersecurity and Infrastructure Security Agency (CISA) warned of a critical vulnerability in NetScaler, identified as CVE-2026-19490, with a CVSS score of 9.3, which has been exploited and affects all NetScaler ADC and Gateway appliances. Citrix has patched this vulnerability as of August 19. AdaptHealth reported a data breach affecting over 4.1 million individuals, compromising personal, health, and insurance information, but not Social Security numbers or financial data. A new strain of Android malware, MantaxOtax, attributed to Indonesian threat actors, combines ransomware and spyware, stealing sensitive information and affecting older Android versions. The Gigabud banking trojan has evolved to evade detection by installing a secondary app that hides the malicious application. CISA acting director Nick Andersen emphasized the need for swift adaptation to cybersecurity threats and highlighted staffing improvements within CISA. Russian e-commerce giant Wildberries experienced disruptions from a DDoS attack affecting payments to sellers, following claims of a cyber operation by Ukraine's military intelligence. McKesson faced a cyberattack exposing sensitive data of 6.4 million individuals, with the ShinyHunters group releasing this data after a failed extortion attempt. IDScan confirmed a data breach affecting 150 million individuals, resulting in the theft of personally identifiable information and government-issued documents.
AppWizard
September 10, 2026
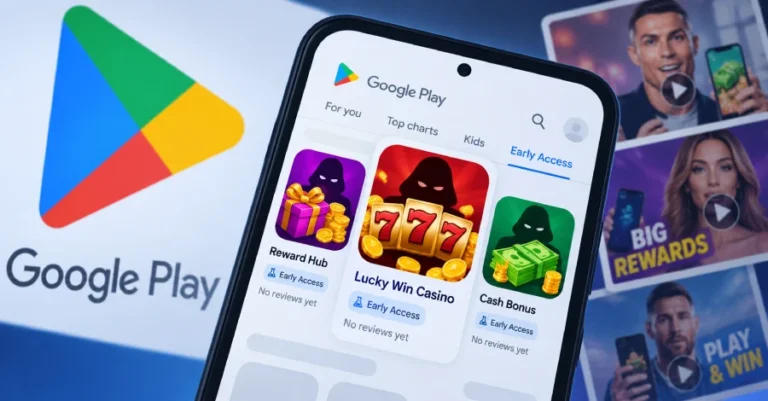
Bad actors are exploiting Google Play's Early Access program to distribute misleading applications that promise money, rewards, and casino winnings. This program allows developers to gather user feedback on unreleased apps but lacks public reviews or star ratings, enabling malicious actors to launch numerous fraudulent applications without immediate scrutiny. An example is the app "Vice Streets: Open World," which mimics Grand Theft Auto, has over 1 million downloads, and recently disappeared from the store without reviews or ratings. These deceptive apps are often promoted on social media with misleading advertisements and promise cash rewards, but users face obstacles when trying to withdraw their earnings. The primary goal of these apps is to generate revenue through excessive advertisements while circumventing regulatory requirements for legitimate gambling apps. Additionally, various malware families targeting Android devices have emerged, including Hagaseca, Mantax Otax, StreamRat, and GoldFactory's use of the Gigabud banking trojan, highlighting ongoing security threats in the digital landscape.
Winsage
September 2, 2026
An active malware campaign is using counterfeit software-download websites to distribute malicious installers, primarily targeting users seeking popular software. This campaign has significantly affected China-based operations of multinational corporations and Chinese-speaking users. The malware, once executed, can establish persistence, undermine security measures, and communicate with attacker-controlled infrastructure. Victims span various sectors, including healthcare, manufacturing, gaming, technology, logistics, government, and education. Microsoft associates this campaign with a Chinese threat cluster called Silver Fox, known for using spoofed vendor download pages to spread Gh0st RAT and ValleyRAT. The malicious websites are hosted on .com.cn and .hl.cn domains, featuring Chinese-language content. The downloaded files are dynamically generated, and upon execution, they deploy a wrapper installer that initiates the malware payload. The malware achieves persistence through scheduled tasks and interferes with Windows Update services. The campaign establishes command-and-control communication over non-standard ports, with two identified domains linked to the activity. Microsoft Defender has detected the threat and initiated containment procedures. Kaspersky reported a related malicious installer exploiting a legitimate adware application to execute a backdoor, which captures keystrokes and clipboard contents. ValleyRAT, a sophisticated implant, can collect system information, reboot the computer, capture screenshots, and transmit logs. The attackers are motivated by cyber espionage and financial gain, targeting organizations globally. A subgroup within GoldenEyeDog, known as CuboidalCanine, has also been linked to the use of ValleyRAT, particularly in the gambling industry. In June 2026, Chinese authorities addressed cybercrime cases involving a new variant of the Silver Fox trojan.
Search