Phishing attacks can compromise personal and financial information through deceptive messages and links. The Anti-Phishing Working Group (APWG) reported 425,808 phishing attacks in June 2026, the highest monthly total since April 2023. SMS-based phishing, or smishing, increased by 40% from Q1 to Q2 2026. Antivirus software with anti-phishing features can block fraudulent websites and identify malicious links.
1. Quick Heal: Offers anti-phishing and online protection, with features like AntiFraud.AI and Scam Protection in Total Security.
2. Norton 360: Combines antivirus with web security and AI-driven scam detection, including a password manager and dark web monitoring.
3. Kaspersky Standard: Provides real-time antivirus, anti-phishing tools, and online payment security.
4. Bitdefender Total Security: Includes anti-phishing protection and real-time behavioral analysis for threat detection.
5. McAfee Total Protection: Features a Scam Detector and premium antivirus, along with web protection and identity monitoring.
When choosing antivirus software, consider anti-phishing capabilities, online banking protection, and device compatibility.
Malware, short for "malicious software," is designed to gain unauthorized access to computers or networks for purposes such as data theft and surveillance. It can be introduced through disguised software or deceptive links. To protect against malware, it is essential to install antivirus software, scan external drives before connecting them, be cautious about downloads, avoid suspicious websites and emails, update applications regularly, enable Tamper Protection on Windows, minimize file sharing, enable Firewall protection, watch out for phishing attacks, and back up data regularly. The future of malware protection may involve leveraging artificial intelligence and machine learning to enhance detection and analysis of threats.
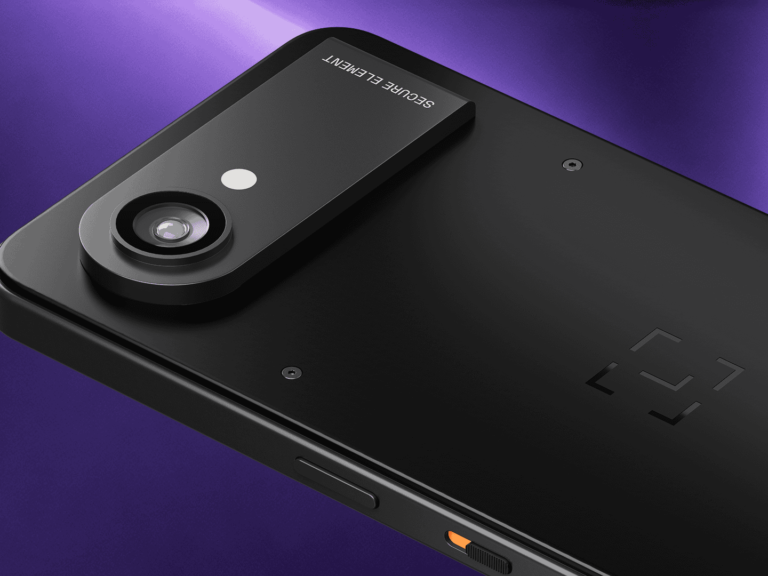
Ledger has introduced Ledger Atom, a security device designed to enhance the protection of sensitive digital activities while allowing the use of everyday applications. It operates on an open-source Android platform for regular apps and a security-focused operating system for sensitive operations, utilizing a secure element chip and a field-programmable gate array (FPGA) for communication between the two environments. Ledger Atom features an integration with OpenClaw, an AI agent platform, which allows AI agents to suggest actions but requires physical approval for sensitive operations. It includes a physical privacy switch that cuts power to the device's cameras and microphones, and supports GPG/OpenPGP encryption for messages. Ledger Atom is positioned as a quantum-ready signing device with post-quantum cryptography and anti-tampering measures. Reservations for a limited Founder’s Edition are open at a price of 9, with an expected launch in summer 2027, pending necessary certifications.
Ledger has introduced the Ledger Atom, a hardware signer designed to run standard Android applications while ensuring robust security features. It operates on a dual-mode system, using Android Open Source Project software for everyday tasks and Ledger OS on a Common Criteria EAL6+ certified Secure Element for sensitive operations. The device features a secure chip, a dedicated screen, and a Privacy Switch to disable the camera and microphone. It is equipped with a 6.77-inch AMOLED display, a 50 MP rear camera, a 32 MP front camera, and connectivity options including 4G and 5G via eSIM. The Atom is a data-only device that does not support traditional voice calls or SMS. It is priced at 9 for the Founders Edition, with shipping expected in the second quarter of 2027.
Microsoft's October 2026 security updates address 1,411 vulnerabilities, marking the largest Patch Tuesday release to date. The update includes 70 vulnerabilities classified as Critical, with 57 related to remote code execution, 11 to elevation of privilege, and two to spoofing. Key vulnerabilities include CVE-2026-96951, a Windows Shell security bypass being actively exploited, CVE-2026-108398, which affects .NET Framework and allows bypassing Windows Defender Application Control, and CVE-2026-92707, a denial-of-service vulnerability in MessagePack-CSharp. The release coincides with critical Windows support deadlines, with the final regular update for Windows 11 24H2 Home and Pro and Windows 10 Enterprise LTSB 2016 occurring on October 13. Organizations are advised to prioritize the exploited vulnerabilities, ensure relevant updates are applied, and validate application-control behavior.
Microsoft Windows 11 Pro is currently available for .99, down from its MSRP of 9. This lifetime license includes advanced features not found in Windows 11 Home, such as BitLocker for drive encryption, Hyper-V for virtualization, and Windows Sandbox for running isolated applications. Additional features include Snap layouts for multitasking, DirectX 12 Ultimate for gaming, and biometric login supported by TPM 2.0. The purchase covers a single PC for life with no ongoing subscription fees.
Microsoft's official account on X experienced a security breach, leading to unauthorized posts promoting a Clippy-themed cryptocurrency token. The company confirmed the breach, removed the misleading content, and is investigating the incident. During the hijack, the account followed a Clippy-themed profile and engaged with its posts, which included a call for likes to "bring Clippy back." Microsoft stated that the posts did not originate from them and emphasized that they do not support any cryptocurrency linked to Clippy. The Clippy-themed account has since been suspended, and Microsoft plans to take legal action against the token and related materials. The incident highlights ongoing concerns about Microsoft's internal security measures, especially given a previous similar breach involving the Microsoft India account in 2024.
Google is experimenting with a new biometric verification feature for password autofill in Chrome on Android devices, which may require users to authenticate their identity through fingerprint scans, facial recognition, or other methods before accessing saved passwords. This initiative aims to enhance security by preventing unauthorized access to stored passwords, even if a device is unlocked. The feature has resurfaced in the latest Chrome Canary build after a previous attempt was shelved over a year ago. Users will need to authenticate themselves before Chrome releases a saved credential, similar to existing biometric methods for password autofill on Apple devices. The feature is currently in the experimental phase with no official release timeline announced.
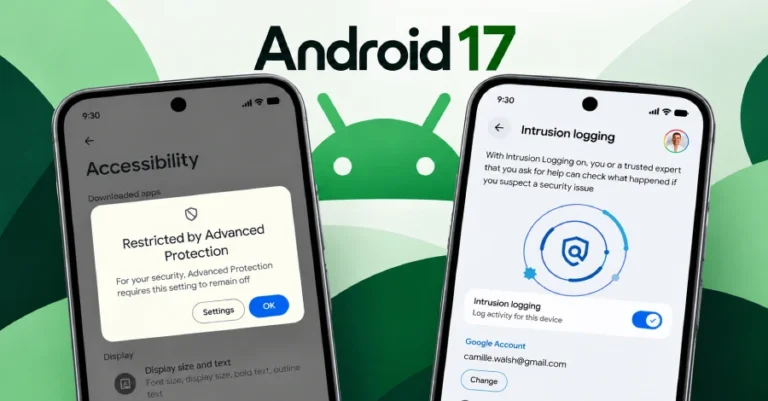
Google has enhanced its Android security framework by restricting access to the AccessibilityService API, allowing only verified applications classified as Accessibility Tools to use these features when Advanced Protection is activated. This decision addresses the misuse of the AccessibilityService API by malicious applications that facilitate malware distribution and financial fraud. The new measures include Intrusion Logging, USB Protection, disabling WebGPU, and a Failed Authentication Lock. Developers will be notified when Advanced Protection is enabled, and users can manually enable Intrusion Logging through the Advanced Protection settings page.