usernames

AppWizard
October 3, 2026
Google is experimenting with a new biometric verification feature for password autofill in Chrome on Android devices, which may require users to authenticate their identity through fingerprint scans, facial recognition, or other methods before accessing saved passwords. This initiative aims to enhance security by preventing unauthorized access to stored passwords, even if a device is unlocked. The feature has resurfaced in the latest Chrome Canary build after a previous attempt was shelved over a year ago. Users will need to authenticate themselves before Chrome releases a saved credential, similar to existing biometric methods for password autofill on Apple devices. The feature is currently in the experimental phase with no official release timeline announced.
AppWizard
September 19, 2026
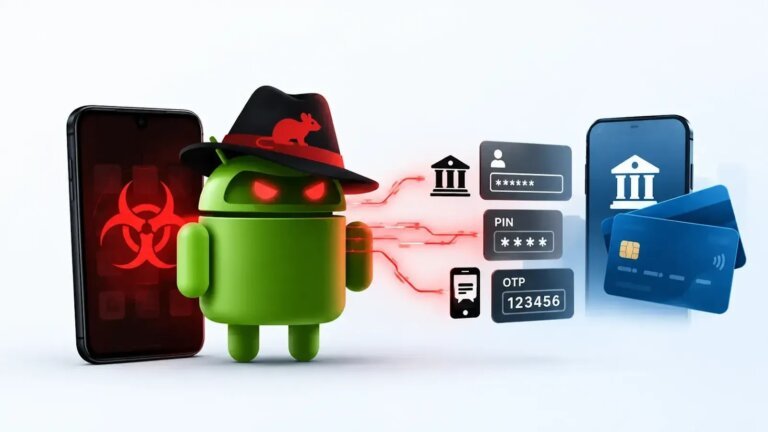
Security researchers have identified an Android banking Trojan named RatHat, which utilizes artificial intelligence, accessibility features, and Android Debug Bridge (ADB) to steal financial credentials, PINs, and one-time passcodes. Unlike traditional malware, RatHat employs a live AI assistant that interacts with the Android accessibility tree, allowing it to make real-time decisions based on the victim's screen content. The infection typically starts with social-engineering tactics, leading victims to counterfeit download pages where they are tricked into sideloading a malicious APK. Once installed, RatHat prompts users to enable Android Accessibility Service permissions, which it exploits to navigate Developer Options and enable Wireless Debugging. This grants it shell-level ADB access, allowing it to bypass application sandbox restrictions. RatHat deploys two native binaries for executing commands and maintaining a connection to the attacker's infrastructure. It targets banking applications through credential-stealing overlays and can intercept SMS messages for transaction verification codes. Additionally, it can record touch coordinates to reconstruct PINs and unlock patterns. RatHat includes persistence mechanisms to restore itself after removal, and users are advised to perform a factory reset if they suspect compromise. To reduce infection risk, users should avoid sideloading apps from unknown links, deny unnecessary Accessibility Service requests, and refrain from enabling Developer Options or Wireless Debugging for unfamiliar applications.
Search