verification

Tech Optimizer
September 21, 2026
More than 5,400 websites across over 2,200 organizations have been compromised to propagate malware, primarily affecting small businesses like clinics and online retailers. The attack mechanism involves malicious code that triggers a deceptive CAPTCHA, instructing users to execute commands that can download malware. Attackers are using the BNB Smart Chain test network to store instructions, making it harder for investigators to shut down operations. A newer variant of the attack uses WebRTC technology to establish encrypted connections for delivering additional malicious code. To protect against these threats, users should avoid pasting commands from websites, be suspicious of unusual CAPTCHA instructions, use strong antivirus protection, keep systems updated, take action if commands are executed, and small business owners should regularly verify their website's integrity.
AppWizard
September 19, 2026
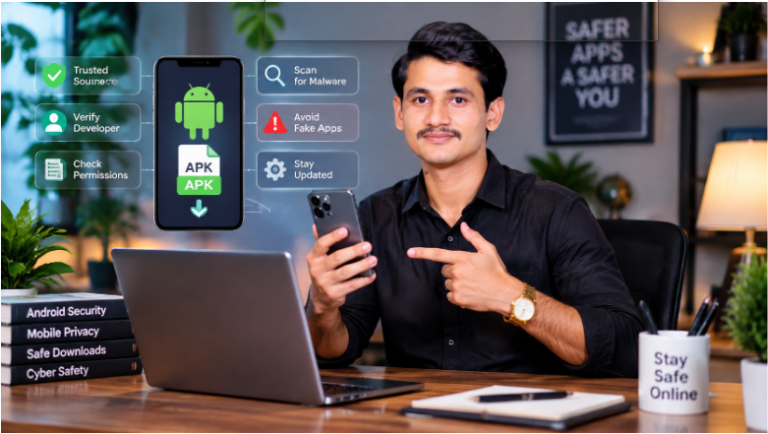
Security researchers have identified an Android banking Trojan named RatHat, which utilizes artificial intelligence, accessibility features, and Android Debug Bridge (ADB) to steal financial credentials, PINs, and one-time passcodes. Unlike traditional malware, RatHat employs a live AI assistant that interacts with the Android accessibility tree, allowing it to make real-time decisions based on the victim's screen content. The infection typically starts with social-engineering tactics, leading victims to counterfeit download pages where they are tricked into sideloading a malicious APK. Once installed, RatHat prompts users to enable Android Accessibility Service permissions, which it exploits to navigate Developer Options and enable Wireless Debugging. This grants it shell-level ADB access, allowing it to bypass application sandbox restrictions. RatHat deploys two native binaries for executing commands and maintaining a connection to the attacker's infrastructure. It targets banking applications through credential-stealing overlays and can intercept SMS messages for transaction verification codes. Additionally, it can record touch coordinates to reconstruct PINs and unlock patterns. RatHat includes persistence mechanisms to restore itself after removal, and users are advised to perform a factory reset if they suspect compromise. To reduce infection risk, users should avoid sideloading apps from unknown links, deny unnecessary Accessibility Service requests, and refrain from enabling Developer Options or Wireless Debugging for unfamiliar applications.
Tech Optimizer
September 13, 2026
The landscape of encryption engines has stabilized, with Microsoft BitLocker and Apple FileVault being the primary solutions. As of 2026, the emphasis is on management rather than just acquiring encryption technology. Key management elements include audit proofing, key escrow and recovery, policy enforcement, and pre-boot options. Native encryption solutions lack features such as fleet-wide compliance proof, centralized key escrow, consistent policy enforcement, advanced pre-boot authentication, and removable-media encryption. Various management models are available for different environments, including: 1. Microsoft BitLocker with Intune: Free for Windows Pro/Enterprise, integrates with Entra ID for key management. 2. Sophos: Manages both BitLocker and FileVault from a single console. 3. ESET: Offers lightweight management and removable-media protection. 4. Trend Micro: Integrates encryption with DLP capabilities. 5. Check Point: Provides advanced pre-boot options and policy management. 6. Trellix: Comprehensive enterprise encryption suite with a complex management interface. 7. WinMagic: Focuses on cross-platform encryption and strong pre-boot options. 8. Broadcom (Symantec): Manages native engines within its broader security framework. 9. Dell: OEM-integrated encryption management for Dell hardware. 10. Kaspersky: Provides encryption management but is restricted in the U.S. Key considerations before deploying encryption include ensuring key escrow is in place, conducting recovery tests, and being mindful of removable media and server encryption. Common mistakes include using outdated freeware and not verifying key escrow. Organizations should request auditor reports for compliance verification and confirm claims of compatibility and pre-boot functionality. Native encryption engines are free, while management layers typically charge on a per-endpoint basis.
AppWizard
September 11, 2026
The Cybersecurity and Infrastructure Security Agency (CISA) warned of a critical vulnerability in NetScaler, identified as CVE-2026-19490, with a CVSS score of 9.3, which has been exploited and affects all NetScaler ADC and Gateway appliances. Citrix has patched this vulnerability as of August 19. AdaptHealth reported a data breach affecting over 4.1 million individuals, compromising personal, health, and insurance information, but not Social Security numbers or financial data. A new strain of Android malware, MantaxOtax, attributed to Indonesian threat actors, combines ransomware and spyware, stealing sensitive information and affecting older Android versions. The Gigabud banking trojan has evolved to evade detection by installing a secondary app that hides the malicious application. CISA acting director Nick Andersen emphasized the need for swift adaptation to cybersecurity threats and highlighted staffing improvements within CISA. Russian e-commerce giant Wildberries experienced disruptions from a DDoS attack affecting payments to sellers, following claims of a cyber operation by Ukraine's military intelligence. McKesson faced a cyberattack exposing sensitive data of 6.4 million individuals, with the ShinyHunters group releasing this data after a failed extortion attempt. IDScan confirmed a data breach affecting 150 million individuals, resulting in the theft of personally identifiable information and government-issued documents.
Search