Virtual Desktop

Winsage
September 12, 2026
Windows 11 KB5124008, released on September 8, has caused various issues, including disruptions to WSL-based applications and Remote Desktop sessions. Users have reported problems with File History backups and instability in Explorer.exe, leading to system and GPU crashes. Microsoft confirmed a bug affecting applications using HCS-managed Linux virtual machines, particularly Claude Cowork, which is experiencing connectivity issues. Remote Desktop Services (RDS) are malfunctioning, leading to connection failures and sign-in problems. Additionally, some users face black screens upon sign-in due to Explorer.exe crashes. Reports indicate that File History is not recognizing external backup drives, and serious GPU issues have been reported on AMD Radeon systems, including driver timeouts and system freezes.
Tech Optimizer
September 12, 2026
If you hold Microsoft 365 E5, you already have access to Microsoft Defender for Endpoint, which provides enterprise-grade endpoint protection at no additional cost. For organizations without a dedicated security specialist, Sophos is recommended. CrowdStrike is suitable for those with a mature Security Operations Center (SOC) and sufficient budget. Other options include SentinelOne for mid-sized organizations needing automation, ESET for older hardware and virtual desktops, Avast Business for very small businesses without IT staff, VIPRE for budget-conscious organizations, and Expel for tool-agnostic managed detection and response. It is essential to assess your organization's current situation honestly when evaluating endpoint protection options. Antivirus and EDR are now essentially the same agent, and organizations should inquire about update staging processes and review independent tests for protection rates. Coverage for servers and Linux environments is often overlooked but crucial, as Linux servers are prime targets for ransomware. Key recommendations include: - Microsoft Defender for Endpoint for organizations already on Microsoft 365 E5. - Sophos for organizations with 25-500 staff relying on IT generalists. - CrowdStrike for enterprises with a well-funded security operations function. - SentinelOne for mid-sized organizations needing autonomous operation. - ESET for organizations with older hardware or virtual desktop infrastructure. - Avast Business for micro and small businesses. - VIPRE for budget-conscious organizations. - Expel for those seeking managed detection across various environments. During deployment, avoid running two real-time agents simultaneously, ensure prevention features are activated, and test on line-of-business applications first. Verify update staging and rollback procedures with vendors, and confirm whether Microsoft licensing covers your needs to avoid unnecessary purchases.
Tech Optimizer
September 10, 2026
If you hold Microsoft 365 E5, you have access to Microsoft Defender for Endpoint, which provides enterprise-grade endpoint protection at no additional cost. For organizations without a dedicated security specialist, Sophos is recommended for its user-friendly platform. CrowdStrike is suggested for those with a mature Security Operations Center (SOC) and sufficient budget. Other options include SentinelOne for mid-sized organizations needing automation, ESET for older hardware and virtual desktops, Avast Business for very small businesses, VIPRE for budget-conscious mixed estates, and Expel for tool-agnostic managed detection and response. Antivirus and EDR are now unified under a single agent, and organizations should inquire about update staging processes to avoid issues like those experienced in July 2024 with a major vendor's faulty content update. Independent tests from organizations like AV-Comparatives and AV-TEST are crucial for evaluating protection rates and false positives. Linux servers require attention as they are often targeted by ransomware. When deploying endpoint protection, avoid running two real-time agents simultaneously, activate prevention features promptly, and test deployments on critical applications first. Organizations should confirm their Microsoft licensing covers necessary features and ensure there is a plan for responding to alerts. Common pitfalls include neglecting identity management and failing to test response workflows before incidents occur.
Winsage
September 9, 2026
On September 8, 2026, Microsoft disclosed a security vulnerability identified as CVE-2026-69449, related to a heap-based buffer overflow in the Windows BitLocker component, allowing authorized attackers to execute code on compromised machines. The vulnerability is classified as CWE-122, and is assessed as “Exploitation Less Likely.” It affects Windows 10, Windows 11, and Windows Server versions from 2012 to 2025. The fixes are included in cumulative updates KB5124008, KB5124012, KB5122878, and KB5122871. No public disclosure or observed exploitation occurred before the patch's release. The flaw allows for remote code execution through in-network attacks, primarily posing a risk to insiders. Affected systems include various versions of Windows 10, Windows 11, and Windows Server, applicable to both x64 and ARM64 architectures. Administrators should verify installed build numbers to ensure updates have been applied. The advisory does not specify which BitLocker code path is affected or the nature of the input that reaches the vulnerable buffer.
Winsage
September 1, 2026
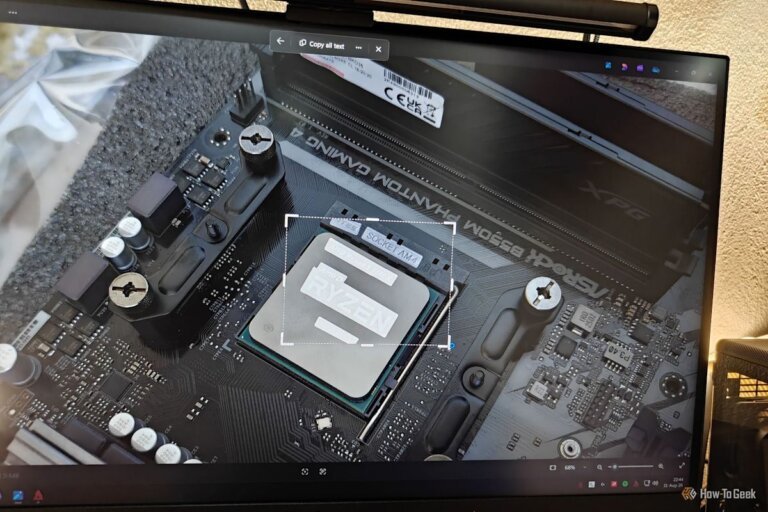
Windows has several advanced features that can enhance productivity, including: - Clipboard History: Activated by pressing Windows+V, this feature stores the last 25 copied items and can be enabled through Settings > System > Clipboard. Users can pin frequently used items for easy access. - Virtual Desktops: Allows users to create multiple workspaces on a single monitor by pressing Windows+Ctrl+D. Users can switch between desktops using Windows+Ctrl+Left Arrow/Right Arrow or Windows+Tab. - Focus Sessions: A built-in Pomodoro timer in the Clock app that promotes productivity by working for 25 minutes followed by a 5-minute break. - Snipping Tool: Accessible via Windows+Shift+S, it allows users to capture screenshots and includes features like screen recording, a color picker, and a Text Extractor for converting text from images. - PowerToys: A suite of free and open-source tools from Microsoft that enhances Windows functionalities, including additional utilities and personalized templates.
Winsage
June 15, 2026
Microsoft has expanded the rollout of the Secure Boot 2023 certificate update to more Windows 11 and Windows 10 devices with the June 2026 Patch Tuesday update (KB5094126). This update aims to ensure that most supported consumer PCs are classified as high confidence, meaning necessary certificates are either installed or will be applied automatically. Secure Boot is a firmware security feature that verifies the software attempting to load during the startup process, blocking unauthorized software. The certificates supporting Secure Boot, issued in 2011, are expiring in stages starting June 24, 2026, prompting Microsoft to deploy replacement certificates. Most home users do not need to take manual action as the updates will occur automatically via Windows Update. Users can check their Secure Boot certificate status in the Windows Security app. A yellow warning indicates pending compatibility data, while a red alert suggests a firmware incompatibility requiring a BIOS update. Multiple reboots during the update process are normal, and a new SecureBoot folder in Windows is for staging cryptographic files. Older PCs may experience longer update times, and some may not receive updates due to firmware issues. HP users should check for BIOS updates if encountering BitLocker recovery loops. IT administrators should monitor device classifications and manually initiate updates for devices not in the high confidence category. Devices with Secure Boot disabled cannot receive updates, leaving them vulnerable. The expiration of the Microsoft Corporation KEK CA 2011 certificate on June 24 does not immediately affect device functionality, but it limits Microsoft's ability to sign new bootkit blacklist updates.
Winsage
May 19, 2026
Parallels Desktop for Mac is recognized as a leading solution for running Windows applications on macOS due to its robust performance, extensive compatibility, and seamless integration capabilities. It allows users to operate Windows, Linux, and other operating systems alongside macOS on a single device, enabling access to Windows 11 and various Windows applications. Parallels Desktop is the only solution endorsed by Microsoft for running Windows 11 on Apple Silicon Macs. It supports features like Coherence Mode, drag-and-drop functionality, direct access to Mac Finder files, and compatibility with thousands of Windows applications, including popular games. The Pro Edition offers advanced tools for developers and power users, such as support for multiple virtual machines, expanded virtual hardware allocation, and integration with Visual Studio. Parallels Desktop is widely adopted by home users, students, enterprises, developers, and creators, and the company provides 24/7 subscriber support and a 30-day money-back guarantee.
Search