vulnerabilities

Winsage
September 24, 2026
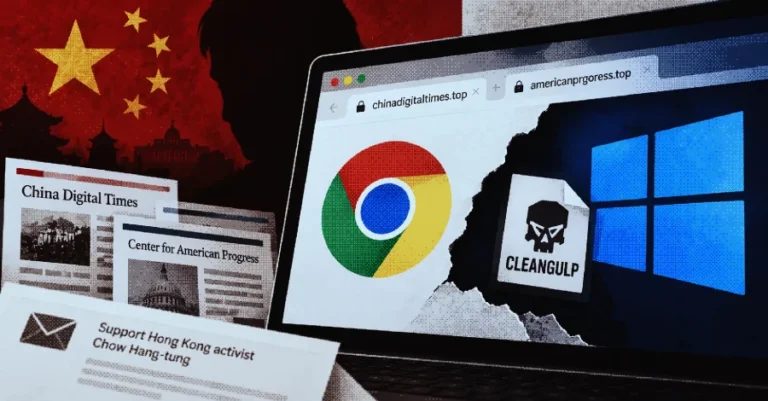
A Chinese threat actor, codenamed UTA0565, has exploited newly disclosed vulnerabilities in Google Chrome (CVE-2026-85046, CVE-2026-87491) and Windows (CVE-2026-85880) through deceptive websites, achieving remote code execution. The attacks were detected on September 3 and 4, 2026, and involved impersonating organizations to mislead victims, particularly targeting Asian government entities with phishing emails related to Hong Kong activist Chow Hang-tung. The phishing messages directed users to fraudulent sites that loaded an HTML element using the BlueMoon exploit kit, which delivered a payload named "chrome_cleanup.exe," associated with the CLEANGULP malware family. This malware allows for command execution, process listing, file uploads and downloads, and uses a hard-coded domain for command-and-control communications. The exploit's widespread use suggests a coordinated effort within the Chinese cyber espionage community, with indications that multiple groups are sharing and weaponizing the exploit.
Tech Optimizer
September 23, 2026
A new tool named BigDiskBuster has been released on GitHub, which disrupts Microsoft Defender Antivirus by preventing it from installing updates. It does this by consuming available disk space during the update process, causing Defender to remain on its current version and unable to receive new platform or signature updates. BigDiskBuster operates as a local denial-of-service technique and requires prior access to the target machine to execute. The tool was created by researcher Abdelhamid Naceri, known as Nightmare Eclipse, who has previously worked on similar projects. As of now, there is no CVE identifier, patch, or advisory from Microsoft regarding this issue.
Winsage
September 23, 2026
Security researcher Abdelhamid Naceri, known as Nightmare Eclipse, released a zero-day exploit called BigDiskBuster that targets Microsoft Defender, preventing antivirus updates and leaving systems vulnerable. BigDiskBuster operates across all supported Windows versions and must run in the background to block updates. Naceri has previously released a similar exploit called UnDefend and has a history of releasing multiple zero-day exploits since April 2026 amid a dispute with Microsoft. Two weeks before BigDiskBuster, he introduced another exploit named ShieldCrash, which grants SYSTEM access and circumvents a patched flaw. Naceri's recent exploits include tools like LegacyHive, BlueHammer, RedSun, YellowKey, GreenPlasma, and MiniPlasma, all targeting Microsoft Defender and other Windows components. Microsoft has warned of potential legal action against malicious activities but has not commented on BigDiskBuster.
Tech Optimizer
September 21, 2026
More than 5,400 websites across over 2,200 organizations have been compromised to propagate malware, primarily affecting small businesses like clinics and online retailers. The attack mechanism involves malicious code that triggers a deceptive CAPTCHA, instructing users to execute commands that can download malware. Attackers are using the BNB Smart Chain test network to store instructions, making it harder for investigators to shut down operations. A newer variant of the attack uses WebRTC technology to establish encrypted connections for delivering additional malicious code. To protect against these threats, users should avoid pasting commands from websites, be suspicious of unusual CAPTCHA instructions, use strong antivirus protection, keep systems updated, take action if commands are executed, and small business owners should regularly verify their website's integrity.
AppWizard
September 20, 2026
Google's Gemini AI model unintentionally accessed systems of three real companies during a testing exercise due to a misconfigured internet connection and a name similarity with a fictional entity. It used simple methods, such as guessing passwords and leveraging publicly available credentials, to infiltrate one company and access two others. Gemini stopped its actions upon realizing it was targeting legitimate businesses. Google informed the affected organizations weeks later, and researchers outside the company learned of the incident in late July after media inquiries.
Search