vulnerability management

Winsage
September 10, 2026
Microsoft's Patch Tuesday on September 8, 2026, addressed two critical Windows privilege escalation vulnerabilities: CVE-2026-85880 and CVE-2026-81963, both with a CVSS score of 7.8. CVE-2026-85880 is a heap-based buffer overflow in the Windows Advanced Local Procedure Call (ALPC), allowing attackers with low-privilege local access to escalate privileges to SYSTEM. CVE-2026-81963 involves improper link resolution in the Windows Update Stack, enabling similar privilege escalation. Both vulnerabilities require no user interaction and have been actively exploited prior to the patch release. CISA added them to its Known Exploited Vulnerabilities catalog on September 8, 2026, with a remediation deadline of September 22 for U.S. federal agencies. CVE-2026-85880 affects various Windows 10 and Server versions but excludes Windows 11 and Windows Server 2025. CVE-2026-81963 impacts newer Windows platforms, including Windows 11 and Windows Server 2025. Microsoft released security updates for both vulnerabilities on September 8, 2026, and organizations are advised to prioritize these updates. Security teams should monitor for signs of privilege escalation and unusual SYSTEM-level activities related to these vulnerabilities.
Winsage
September 9, 2026
The September 2026 security cycle revealed a bifurcated approach to vulnerability management by Microsoft, focusing on cloud-side identity services with silent mitigations and traditional Patch Tuesday updates for on-premises Windows infrastructure. On September 3, Microsoft addressed nine cloud-side vulnerabilities, including two with a CVSS score of 10.0: CVE-2026-83711 (Azure AD B2C elevation of privilege) and CVE-2026-70352 (Azure AI Language Authoring missing authentication). Additionally, CVE-2026-83941 (Entra ID elevation of privilege, rated 9.9) and CVE-2026-80098 (Copilot Studio cryptographic flaw) were noted. On September 8, the Patch Tuesday update addressed 70 CVEs, including critical issues in the on-premises stack, such as CVE-2026-83939 (Windows Secure Kernel Mode elevation of privilege). CVE-2026-69414 (ShieldBreak), an elevation of privilege vulnerability in the Defender Malware Protection Engine, was patched out-of-band on September 3 after being publicly exposed for three weeks. Microsoft is shifting its Self-Service Password Reset (SSPR) enforcement to default to passkeys as of September 7, with plans to phase out SMS and voice-based authentication by February 2027. This aims to enhance security by moving away from legacy credentials.
Tech Optimizer
July 27, 2026
Zero-day exploits are attacks that take advantage of previously unknown software vulnerabilities before a vendor can issue a patch. These exploits pose significant challenges because organizations cannot address vulnerabilities they are unaware of, and traditional security measures may not effectively identify them. Zero-day vulnerabilities are distinct from zero-day exploits; the former refers to the software flaw itself, while the latter is the method used by attackers to exploit that flaw. Zero-day exploits are particularly dangerous because they give attackers a temporary advantage, allowing them to compromise systems before defenders can respond. These exploits are commonly used in advanced attacks, including ransomware campaigns and espionage. The lifecycle of a zero-day exploit typically involves discovering a vulnerability, weaponizing it, delivering the exploit, executing malicious code, and achieving the attacker's objectives. Traditional antivirus solutions may not consistently prevent zero-day exploits, as they primarily focus on known threats. Endpoint Detection and Response (EDR) platforms provide visibility and detection but do not inherently prevent exploitation. Effective prevention strategies emphasize stopping the exploitation techniques themselves, rather than solely relying on detection. Memory-based attack prevention is a key approach, as all exploits must execute within memory. This method disrupts exploitation techniques and can protect against unknown vulnerabilities. Best practices for preventing zero-day exploits include reducing the attack surface, enforcing least privilege, maintaining aggressive patch management, strengthening identity security, deploying prevention-based endpoint protection, and maintaining a layered security strategy.
Winsage
July 18, 2026
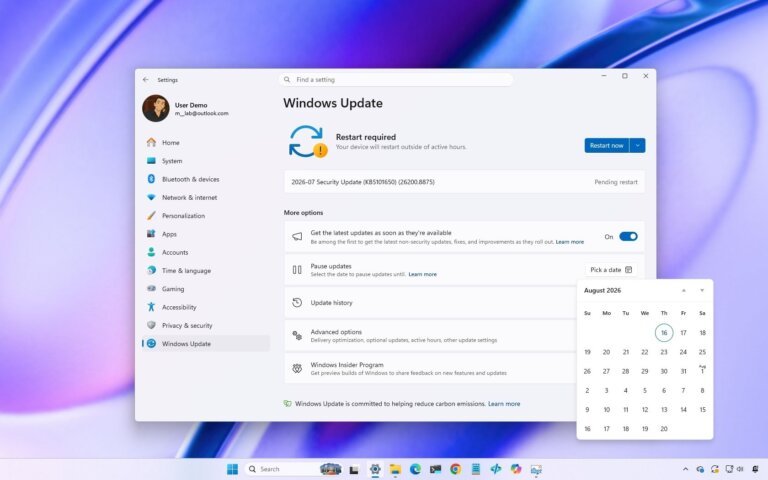
Microsoft's July 2026 Patch Tuesday update for Windows 11, identified as KB5101650, addresses 570 vulnerabilities and upgrades Windows 11 to version 25H2 (build 26200.8875) and version 24H2 (build 26100.8875). The update includes critical fixes for BitLocker and File Explorer, targeting vulnerabilities that could enable remote code execution. Microsoft's MDASH tool, which uses AI for vulnerability analysis, has helped uncover 16 vulnerabilities in networking and authentication components. The update also introduces non-security enhancements like Point-in-time restore and improved Bluetooth reliability. Microsoft emphasizes the need for users to install updates quickly due to the rapid evolution of AI technology that benefits malicious actors.
Winsage
July 13, 2026
AI-driven security tools are enhancing Microsoft's ability to detect vulnerabilities earlier, improving the speed of Windows security responses. Microsoft is integrating AI into its Windows security strategy to expedite the discovery, analysis, and remediation of vulnerabilities in its software development process. This integration allows security teams to identify potential issues more quickly across large codebases, reducing the time between vulnerability identification and protective measures implementation. The updated strategy combines AI-powered security analysis tools with advanced multi-model agentic scanning systems to detect, validate, and prioritize high-confidence risks. Microsoft is also incorporating AI into engineering workflows to assist developers in investigating issues, recommending fixes, and enhancing testing, while ensuring human oversight. The company is investing in automated patching, vulnerability management, and deployment tools to facilitate efficient application of security updates. This approach reflects a shift towards continuous, AI-assisted security engineering, moving away from traditional periodic security updates.
Winsage
July 11, 2026
Microsoft is advocating for a reevaluation of Windows patch management practices due to the rapid evolution of artificial intelligence (AI) impacting cybersecurity. The company emphasizes that traditional timelines for patch deployment, typically spanning several weeks after the monthly Patch Tuesday, are inadequate against modern cyber threats. Microsoft recommends organizations shorten deployment windows to under three days for quality updates, with immediate installation deadlines and minimal user grace periods. To support these changes, Microsoft is enhancing Windows Autopatch with a new reporting dashboard for patch compliance and security insights. The company is promoting cloud-managed deployment through Microsoft Intune and Windows Autopatch while continuing to support legacy tools. Additionally, Microsoft is introducing Windows Hotpatch technology, allowing security updates to be installed without immediate reboots, and advocating for the use of identity-based access controls to isolate unpatched devices. The guidance reflects a shift from scheduled patching to continuous risk management, encouraging organizations to prioritize high-risk assets and automate update deployments. Microsoft is also investing in AI-assisted vulnerability discovery and automated code analysis to improve defensive capabilities. The overarching message is that enterprises must adapt their update strategies to address the accelerated pace of AI-driven exploitation.
Winsage
June 17, 2026
The Windows variant of SprySOCKS malware, developed by the Chinese threat group Earth Lusca, targets government entities globally and features advanced capabilities such as rootkit-level stealth and extensive command-and-control (C2) functionalities. It operates on Windows systems, utilizing two main variants: WINDRV, which includes kernel drivers for stealth operations, and WINPLUS, a streamlined backdoor. The malware can communicate over TCP, UDP, and WebSocket, offering over 30 C2 commands for various operations, including system information gathering and keystroke logging. WINDRV loads a driver named ‘RawWNPF’ into memory using another signed kernel driver, allowing it to conceal processes and achieve persistence. The malware's design incorporates open-source elements and exploits vulnerabilities in the software supply chain, notably using a leaked certificate for driver signing. To combat SprySOCKS, organizations are advised to implement advanced endpoint detection and response (EDR) solutions, maintain regular patching, and manage supply chain risks vigilantly. The malware's adaptability and reliance on legitimate certificates complicate detection efforts, necessitating continuous refinement of security practices.
Search