wallet

AppWizard
September 29, 2026
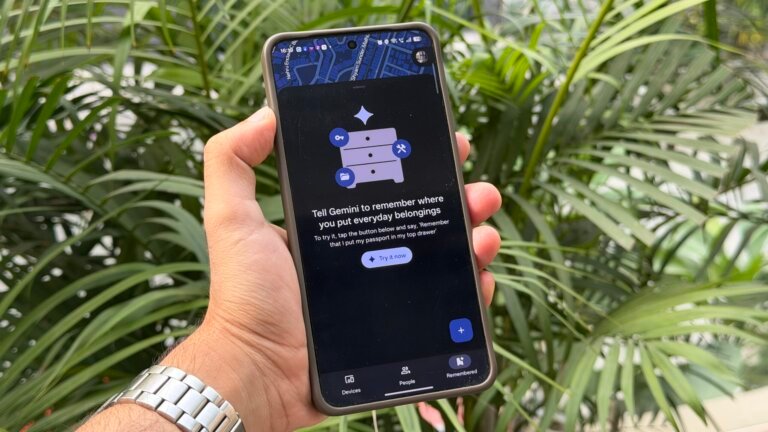
Google has enhanced the Find Hub app by introducing a feature called the Remembered tab, which allows users to track items that cannot accommodate a physical tracker. Users can tag items, record notes, and attach pictures to help remember where they are stored. Instead of using a physical tracker, users can inform Google’s AI assistant, Gemini, about an item's location verbally or through manual entry. This feature is particularly useful for organizing items that are not frequently moved, such as passports or other essential belongings. Users can quickly add items by stating their location and taking a photo, making it easier to retrieve them later. The Remembered tab enhances the utility of the Find Hub app without requiring additional subscriptions or gadgets.
AppWizard
September 28, 2026
The Android version of Google Wallet now allows users to check their balance of Google Store Points, expanding its functionality beyond managing Google Play Points. Users can monitor their Google Store Points alongside other rewards, but these points cannot be used for purchases within the app.
Tech Optimizer
September 25, 2026
Cybercriminals have developed an infostealer called MacSync, targeting Mac devices by using iCloud calendar events and cloud storage. This malware disguises itself as fake cryptocurrency wallets and pirated software. It begins with a loader that retrieves instructions from calendar entries and deploys malware to exfiltrate sensitive information, including credentials and cryptocurrency wallets. Recent versions have introduced an Objective-C backdoor that mimics Finder. Victims are often tricked into downloading these malicious applications, and effective antivirus solutions can prevent damage. Cybercriminals use tactics like SEO poisoning and phishing to direct victims to fraudulent websites or social media promoting pirated software. In one case, the loader was marketed as a cryptocurrency wallet, and victims encountered a misleading ClickFix error message that prompted them to execute a command in the Terminal.
Tech Optimizer
September 22, 2026
LastPass has identified a sophisticated scheme targeting users of its Authenticator app, involving SEO poisoning and deceptive GitHub pages that distribute malicious ZIP files disguised as legitimate software. Users searching for "LastPass Authenticator download" may encounter these counterfeit pages, which redirect them to a malicious server delivering a ZIP file containing vsdbg.exe and vsdbg.dll. The executable is a legitimate Microsoft debugging tool exploited to execute the malicious DLL through DLL sideloading, allowing the malware to run undetected. Named Rapuncel by security researchers from Delphos, this malware is undetectable by antivirus engines and targets a hardcoded list of 145 antivirus and endpoint security products, disabling them upon detection. Rapuncel harvests sensitive information, including saved passwords from over 25 web browsers, cryptocurrency wallet files from more than 30 applications, and session tokens from platforms like Discord and Steam. It also captures screenshots and compiles a profile of the infected system, uploading the stolen data to an attacker-controlled server. The malware includes a kernel driver that intercepts web traffic, allowing for advertisement injection and search result manipulation. This campaign has been active for several months, with LastPass vaults remaining unaffected. Users are advised to download applications only from trusted sources. Rapuncel establishes persistence on infected machines by installing itself as a Windows service that starts with the system and terminates activated security products. Removing the kernel driver requires booting into Safe Mode or using external recovery tools, as standard Windows utilities cannot eliminate software operating at that level.
Search