Windows Autopatch

Winsage
October 1, 2026
Microsoft has rolled out the Windows 11 2026 Update (version 26H2) for eligible devices running Windows 11 versions 24H2 or 25H2. The update is being implemented as a controlled feature rollout and is delivered as an enablement package, activating features already integrated into the system. Versions 24H2, 25H2, and 26H2 share a unified servicing branch and codebase, making the installation process similar to a standard monthly cumulative update. Windows 11 26H2 consolidates various improvements, security enhancements, and fixes from version 25H2, with some features previously disabled in 25H2 now enabled by default. Installing 26H2 resets the support clock, providing 24 months of support for Home and Pro editions and 36 months for Enterprise and Education editions. Users can manually request the update through Windows Update settings. Organizations can deploy version 26H2 using Windows Autopatch and other management tools, with a recommendation for targeted deployment initially. Devices that shipped with Windows 11 version 26H1 cannot upgrade to 26H2 due to differences in the Windows core. Microsoft may also implement safeguard holds on devices with known compatibility issues, delaying the update until resolved.
Winsage
September 30, 2026
Microsoft has unveiled the Windows 11 2026 Update, version 26H2, on September 29, 2023, accessible for eligible devices running Windows 11 versions 24H2 or 25H2. The update is a controlled feature rollout and is delivered as an enablement package, activating features already embedded in the system. It consolidates improvements, security patches, and enhancements from the past year, with some features previously disabled in 25H2 now enabled by default in 26H2. Installing 26H2 resets the support lifecycle, providing 24 months of support for Home and Pro editions and 36 months for Enterprise and Education editions. Users can manually request the update through Windows Update settings. Organizations can deploy 26H2 via Windows Autopatch and other management tools, with targeted deployments recommended first. Devices that shipped with Windows 11 version 26H1 cannot upgrade to 26H2 and will receive a future upgrade path instead. Microsoft may also implement safeguard holds on devices with known compatibility issues.
Winsage
September 30, 2026
Windows 11, version 26H2 is now available for eligible devices running Windows 11, versions 25H2 and 24H2. The update is delivered via a small enablement package that activates new features already integrated into the operating system. The installation process is similar to a monthly update, requiring a minor download and a quick restart. The update includes enhancements in quality, reliability, and security. For commercial and educational customers, it can be accessed through existing management tools like Windows Autopatch and the Microsoft 365 admin center. Version 26H2 offers 24 months of support for Home and Pro editions and 36 months for Enterprise and Education editions. Some features that were disabled in version 25H2 will now be enabled by default in version 26H2.
Winsage
August 27, 2026
Windows 10 Enterprise LTSB 2016 and Windows 10 IoT Enterprise 2016 LTSB will reach their end of support on October 13, 2026, after which they will no longer receive security updates. These operating systems are designed for fixed-function devices like kiosks and point-of-sale terminals, which are often not actively managed, posing risks if the end-of-support date is overlooked. Microsoft offers an Extended Security Updates (ESU) program as a temporary solution, with escalating costs over three years, but it is not intended as a long-term fix. Customers must decide whether to continue paying for ESU, upgrade to newer hardware, or transition away from Windows.
Winsage
July 13, 2026
Microsoft has released a guide on the Windows servicing model, detailing monthly security updates, optional preview releases, hotpatch updates, and feature rollout mechanisms. Patch Tuesday occurs every second Tuesday of the month, delivering cumulative security updates to supported Windows versions. For consumers and small businesses, updates are managed through Windows Update, while enterprises can use various tools like Windows Autopatch and WSUS. Hotpatch updates, which focus on security fixes, can be installed without a restart, unlike quarterly baseline updates that require one. Optional non-security preview updates are released in the fourth week of each month for testing upcoming fixes and new features, available only for the latest supported Windows versions. Unmanaged devices can access these updates through Windows Update settings, while IT-managed devices depend on organizational policies. Microsoft also issues out-of-band updates to address urgent issues, which can be deployed through enterprise management tools. New features for Windows 11 are rolled out throughout the year via various channels, with a gradual rollout strategy to monitor quality and compatibility, using the Controlled Feature Rollout approach.
Winsage
July 11, 2026
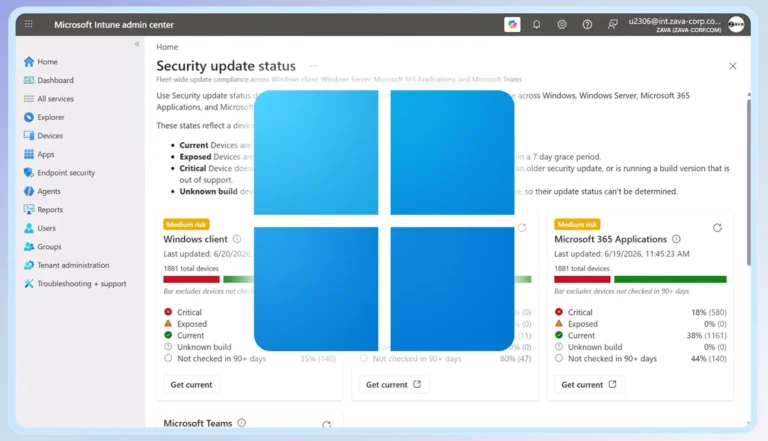
Microsoft is advocating for a reevaluation of Windows patch management practices due to the rapid evolution of artificial intelligence (AI) impacting cybersecurity. The company emphasizes that traditional timelines for patch deployment, typically spanning several weeks after the monthly Patch Tuesday, are inadequate against modern cyber threats. Microsoft recommends organizations shorten deployment windows to under three days for quality updates, with immediate installation deadlines and minimal user grace periods. To support these changes, Microsoft is enhancing Windows Autopatch with a new reporting dashboard for patch compliance and security insights. The company is promoting cloud-managed deployment through Microsoft Intune and Windows Autopatch while continuing to support legacy tools. Additionally, Microsoft is introducing Windows Hotpatch technology, allowing security updates to be installed without immediate reboots, and advocating for the use of identity-based access controls to isolate unpatched devices. The guidance reflects a shift from scheduled patching to continuous risk management, encouraging organizations to prioritize high-risk assets and automate update deployments. Microsoft is also investing in AI-assisted vulnerability discovery and automated code analysis to improve defensive capabilities. The overarching message is that enterprises must adapt their update strategies to address the accelerated pace of AI-driven exploitation.
Winsage
July 10, 2026
Microsoft advises organizations to expedite their Windows update deployment timelines due to advancements in artificial intelligence that allow cyber attackers to quickly exploit vulnerabilities after security updates are released. Jeremy Chapman, Director of Microsoft 365, warns that delaying critical quality updates with security fixes increases the risk of exploitation. Microsoft recommends a quality update deferral period of fewer than three days, update deadlines of zero or one day, and a grace period of no more than two days. The Windows Autopatch report within Microsoft Intune helps identify unpatched devices, allowing administrators to adjust update deferral policies. Organizations can configure update delivery settings through policy controls in Windows Autopatch and Microsoft Intune, as well as other management tools like Microsoft Configuration Manager and Windows Server Update Services. Microsoft also promotes the use of Hotpatch for quicker installation of security updates without rebooting and encourages Conditional Access policies to restrict access to corporate resources for devices that lack required updates.
Winsage
July 9, 2026
Windows 10 and 11 updates can cause significant issues for users, including high disk space consumption, disruptions to desktop UI functionalities, and potential lockouts via BitLocker recovery. These problems often lead to delays in installing new patches by IT administrators and users, which can expose systems to vulnerabilities. Microsoft has raised concerns about this cautious approach, emphasizing that AI is changing the cybersecurity landscape by enabling faster identification and exploitation of vulnerabilities. To address this, Microsoft recommends moving away from broad deployment delays and adopting staged rollout strategies, using deployment rings to validate patches on a limited number of devices before wider distribution. Additionally, Microsoft has introduced technologies like Windows Autopatch and Hotpatching to automate and streamline the update process while maintaining security. The company advocates for expediting update validation to better protect systems in an evolving threat environment.
Search