Windows hosts

Winsage
September 13, 2026
NVIDIA released CUDA Toolkit 13.4 on September 9, 2026, introducing native CUDA support for Windows on Arm. This update allows developers to compile and run CUDA applications on Windows Arm64 systems, closing a gap that existed since CUDA's inception in 2007. The toolkit offers two workflows: native compilation on Windows Arm64 machines and cross-compilation from x86-64 systems. Developers must install an R616-series Developer Driver to utilize the new features. The release aligns with the upcoming launch of NVIDIA's RTX Spark laptops, built on the N1X Arm platform. The toolkit is designed for RTX Spark devices, which leverage NVIDIA’s Blackwell GPU architecture. Current Windows on Arm devices can also begin using the toolkit in preparation for the hardware launch. The initial feature set for Windows Arm64 is narrower compared to x86-64, but developers are encouraged to adapt their applications for the new environment.
Winsage
June 3, 2026
Microsoft has introduced Coreutils for Windows, based on the open-source Rust reimplementation of GNU Coreutils, to enhance its developer ecosystem and simplify cross-platform development. This integration allows developers to use familiar Linux command-line utilities natively within Windows, promoting consistency across operating systems. Additionally, Microsoft has unveiled WSL containers, enabling developers to create, run, and deploy Linux containers directly through the Windows Subsystem for Linux (WSL). This feature aims to streamline Linux container workflows and reduce reliance on third-party platforms. Microsoft has noted significant engagement with WSL, receiving over 200 pull requests monthly since its open-sourcing. New APIs will also allow native Windows applications to manage Linux containers programmatically, with controls for IT administrators to oversee container usage. A public preview of WSL containers is expected in the coming months.
Tech Optimizer
January 29, 2026
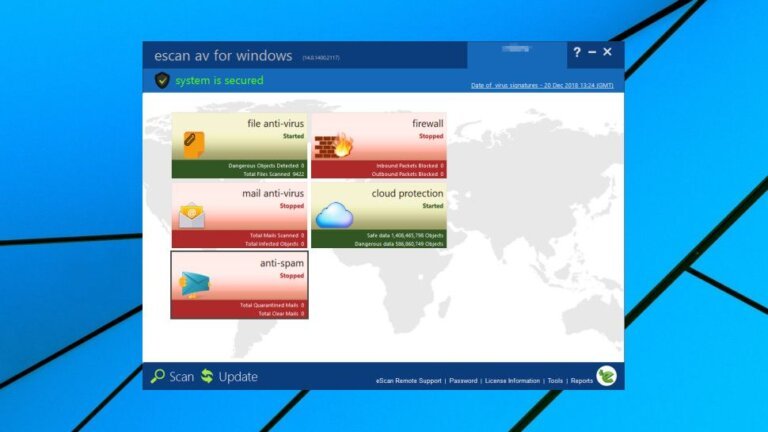
Recent reports indicate that the antivirus program eScan experienced a security breach, leading MicroWorld Technologies to conduct an internal investigation. A threat actor exploited compromised update servers to distribute malware to users who downloaded updates during a two-hour window on January 20, 2026. The exact number of affected users is unknown, but the company has isolated the compromised infrastructure and refreshed credentials while assisting impacted users. The eScan product itself was not altered, and the victims were limited to a specific regional cluster. The malware, identified as CONSCTLX, operates as a backdoor and downloader, allowing attackers to maintain access and execute commands on infected devices. The identity of the attackers is unknown, but North Korean cybercriminals previously exploited eScan's update mechanism in 2024. MicroWorld Technologies has provided support to millions of customers but has not disclosed the total number of eScan users.
Winsage
November 4, 2025
The Russian-aligned APT group Curly COMrades has been using hidden Alpine Linux virtual machines (VMs) on compromised Windows hosts via Microsoft Hyper-V to evade detection and maintain covert access. This technique was uncovered in mid-2025 through an investigation by Bitdefender and the Georgian CERT, which traced suspicious activities to a compromised Georgian website. The attackers activated Hyper-V on the infected machines, downloaded a disguised VM image, and named it “WSL.” The VM, operating on Alpine Linux, had a small disk footprint and low RAM usage, minimizing alerts from security systems. Within this environment, they deployed two malware implants: CurlyShell, a reverse shell for command execution, and CurlCat, a reverse proxy tool for SSH traffic. Both implants were designed to maintain a low forensic footprint. The attackers also used a PowerShell script to inject encrypted Kerberos tickets into LSASS for lateral movement and employed various tunneling tools for communication. Artifacts from their operations were stored in directories that blended with legitimate Windows files. Security teams are advised to audit Hyper-V usage, monitor for hidden VMs, and enable host-based network inspection.
Winsage
September 29, 2024
Oracle has released VirtualBox version 7.1.2, a maintenance update focusing on user experience improvements and technical fixes. Key enhancements include a multi-window layout, resolution of virtual machine management issues, customizable remote display security, and a more stable macOS/Arm UI. Technical fixes address NAT performance on Windows hosts, DHCP issues for certain guest configurations, enablement of 3D acceleration for ARM-based VMs, improvements in state management, UEFI Secure Boot querying, and SDK enhancements. VirtualBox 7.1.2 is available for free download and supports multiple platforms, including Windows, macOS, Linux, and Solaris.
Winsage
September 3, 2024
VMware Workstation Pro has transitioned to a free model for personal use with the release of version 17.6. This update introduces a new command-line tool, vmcli, which allows users to perform operations such as creating virtual machines and modifying VM settings via Command Prompt or Terminal. The update expands support for guest and host operating systems, including Windows Server 2025, Windows 11 Version 23H2, Ubuntu 24.04, and Fedora 40. It addresses critical issues such as VMware KVM crashes, slow virtual machine performance on non-admin Windows accounts, and installation failures on Linux hosts with kernel version 6.8. Notable changes include the removal of legacy VMTools ISOs, end-of-life support for Bluetooth hub passthrough, discontinuation of physical host parallel ports support for Windows, removal of Unity mode, and the Enhanced Keyboard driver. VMware Workstation Pro can be downloaded for free for personal use, but a free account is required, and commercial use still requires a license.
Winsage
July 27, 2024
The faulty update provided by CrowdStrike for Windows led to massive system failures, affecting major airlines, healthcare providers, and retail operations. The issue was not a result of a cyberattack but a critical flaw in the update's coding. CrowdStrike's CEO, George Kurtz, had previously been involved in a similar tech failure at McAfee in 2010, raising questions about the company's internal processes and safeguards.
Search