Windows Security app

Tech Optimizer
September 19, 2026
For nearly two months, Windows 11 users received persistent notifications from the Windows Security app falsely indicating that Microsoft Defender was disabled, despite it functioning properly. This issue, which began in early August, has been addressed with a security update from Microsoft. The false alerts affected all versions of Windows 11, Windows Server, and Windows 10, and were linked to a bug introduced with a recent Defender security update. Microsoft confirmed that no manual action is required from users to resolve the issue, as the fix will be automatically deployed to all PCs with mandatory security updates enabled. The problem was resolved in the Microsoft Defender Antivirus update (version 4.18.26080.4), released on September 17, 2026. Users can verify the status of Defender by checking Windows Security or using a PowerShell command.
Winsage
September 19, 2026
Microsoft resolved an issue that caused misleading alerts indicating that Defender Antivirus was disabled after recent updates. This fix was confirmed in an update to the Windows release health dashboard and was implemented in the Microsoft Defender Antivirus update (version 4.18.26080.4) rolled out on September 17. The bug, acknowledged by Microsoft in late August, affected users in the Release Preview Channel of the Windows Insider program since at least June and impacted all supported versions of Windows clients and servers. Users received erroneous notifications in the Windows Security app prompting them to activate Microsoft Defender Antivirus, despite it functioning correctly. Misleading alerts could appear upon Windows startup and intermittently thereafter, even when notification settings were disabled.
Tech Optimizer
September 8, 2026
Microsoft has acknowledged a software bug causing persistent Windows Security pop-ups that incorrectly indicate antivirus protection is disabled. These notifications began appearing after the latest Microsoft Defender Antivirus updates, but the antivirus is functioning correctly. The issue affects various versions of Windows and Windows Server with the latest Defender updates. Microsoft has committed to resolving the issue in a future update, though no timeline has been provided. Users are advised to verify the status of their antivirus through the Windows Security app and disregard the notifications until a fix is released.
Tech Optimizer
September 4, 2026
Microsoft has acknowledged a software bug in its Windows operating system that causes misleading pop-up notifications, indicating that antivirus protection is disabled. These alerts began appearing after the latest Microsoft Defender Antivirus updates, despite the antivirus functioning correctly. The notifications can occur at startup and intermittently, and cannot be silenced through standard notification controls. The issue affects various versions of Windows and Windows Server with the latest Defender updates. Microsoft is working on a resolution, but no timeline has been provided. Users are advised to verify their antivirus status through the Windows Security app and can ignore the notifications if real-time protection is confirmed as active.
Tech Optimizer
August 30, 2026
Microsoft has confirmed that notifications stating “Microsoft Defender Antivirus is turned off” are erroneous and can appear during startup and intermittently, even with notification settings disabled. The issue stems from recent updates to Windows antivirus software, but the antivirus is functioning correctly. This problem affects all versions of Windows or Windows Server running Microsoft Defender Antivirus with the latest updates. Users may see pop-ups urging them to “Turn on virus protection,” which falsely suggest that protection is disabled. Microsoft is working on a resolution, and users are advised to verify that their antivirus is operational and that real-time protection is enabled.
Winsage
August 20, 2026
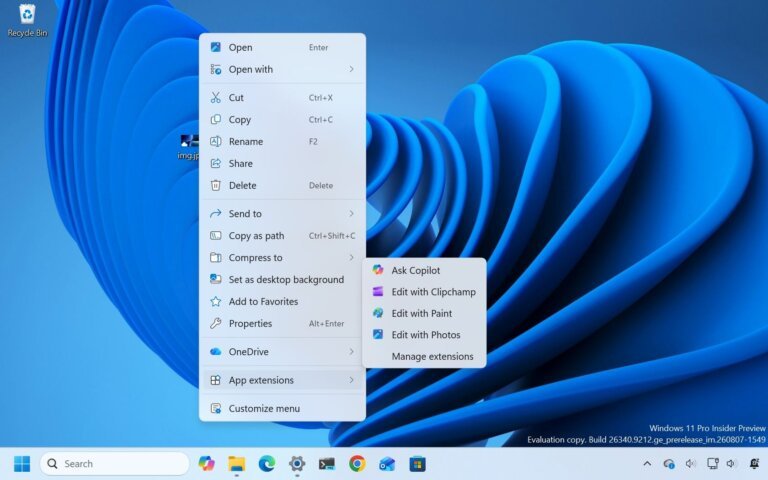
In early August, there were no new Windows 11 builds released for over 15 days in the Windows Insider Program. On August 17, Microsoft released five new preview builds, introducing several features and enhancements. Key updates include a fully customizable context menu, allowing users to tailor options directly from Settings under Personalization, and improvements to the desktop background experience with higher resolution previews and better slideshow transitions. The Camera Roll backup feature now automatically backs up photos and videos to OneDrive. The Magnifier tool received a visual refresh, and the Windows Recovery Environment was upgraded to reuse eligible Wi-Fi profiles automatically. Microsoft also removed the Windows Management Instrumentation Command-line (WMIC) tool and the Drag Tray feature while maintaining access to WMI through PowerShell. File Explorer improvements include a faster launch for the "Home" page and touch scrolling support in the "Recommended" section. Minor visual adjustments were made to the Windows Security app, enhancing its alignment with the Windows 11 design language.
Winsage
July 29, 2026
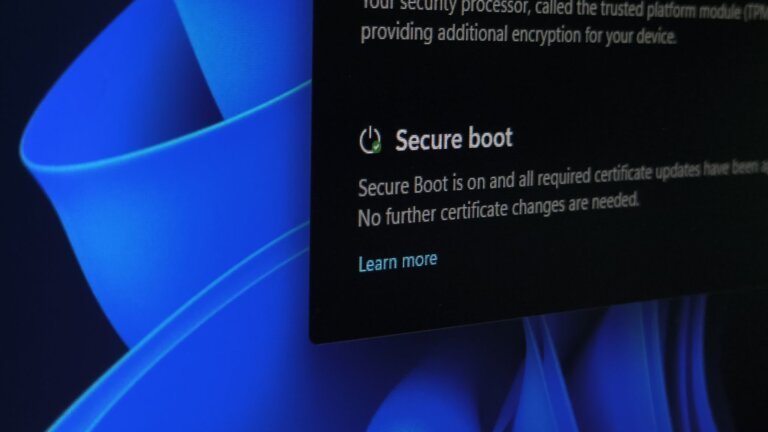
Microsoft reassured Windows 11 and Windows 10 users that their PCs will continue to boot normally and receive updates even if they have not yet received the new Secure Boot 2023 certificates. The rollout of these certificates is expected to continue over the upcoming months. The initial Secure Boot certificate expired on June 24, 2026, and Microsoft has been replacing older 2011 certificates since 2024. The latest update, KB5101650, transitioned Windows 11 to OS builds 26200.8875 and 26100.8875 for versions 25H2 and 24H2, respectively. The 2023 certificates replace older certificates with modern cryptographic standards, allowing Microsoft to deliver DBX revocation updates without interruption. Devices using the 2011 KEK can only receive DBX updates signed with that key, which is no longer valid after June 24. Microsoft has been rolling out the 2023 certificates for the past two years, and many devices remained in a yellow or red status by the June deadline. To check Secure Boot status, users can navigate to Windows Security > Device Security. A green checkmark indicates successful application of the certificates, while yellow and red alerts indicate compatibility issues or firmware incompatibility. PCs that are older or operating in Legacy BIOS mode will not receive the updates. Windows 10 also receives Secure Boot updates, but enrollment in Extended Security Updates (ESU) is required.
Winsage
July 10, 2026
Microsoft has acknowledged that some Windows 11 PCs are facing issues with Secure Boot certificate updates, which may fail to install or be blocked. The company is working with PC manufacturers to develop a patch, while users may need to take proactive measures if their certificates are obstructed. Microsoft has temporarily halted the rollout of Secure Boot for certain devices due to complications, and affected users will receive detailed error messages in the Windows Security app regarding their Secure Boot certificates. Secure Boot certificates issued in 2011 have expired, and Microsoft is replacing them with new certificates issued in 2023. Most modern hardware is already utilizing the new certificates, but some devices may have disabled Secure Boot or faulty firmware. Users can check their Secure Boot status in the Windows Security app. HP has confirmed that Secure Boot updates are being blocked on some of its PCs due to a BitLocker issue, which prevents the installation of new certificates. Microsoft has paused Secure Boot certificate updates for devices affected by known issues while collaborating with manufacturers to identify specific devices or firmware complications. A firmware update will be necessary for affected devices, but it is not yet available. The majority of PCs have received the Secure Boot certificates via Windows Update, but compatibility issues may prevent some devices from receiving the update. Older devices or those not among the OEM’s top-selling models may not receive updates if the UEFI firmware is unsupported. Secure Boot is a security feature required for Windows 11, preventing unauthorized software from executing at boot. While an expired Secure Boot certificate does not stop a PC from functioning, it may limit long-term security protection. Microsoft advises users not to disable Secure Boot, as it would compromise security further.
Winsage
June 29, 2026
Major PC manufacturers, including HP, Dell, ASUS, Lenovo, MSI, Acer, Samsung, LG, and Microsoft’s Surface division, have provided guidance on transitioning to new Secure Boot certificates as the expiration of Microsoft’s 2011 certificates approaches. The expiration will occur in three phases: Microsoft Corporation KEK CA 2011 expired on June 24, 2026; Microsoft UEFI CA 2011 expired on June 27, 2026; and Microsoft Windows Production PCA 2011 is set to expire on October 19, 2026. Microsoft has begun rolling out replacement certificates through Windows Update, contingent on OEMs providing compatible BIOS updates. ASUS offers detailed documentation for both consumer and commercial devices, confirming that most users will receive updates automatically. Lenovo provides direct download links for BIOS updates organized by product family and specifies which products will not receive updates. Dell's support article covers its entire product lineup, noting that devices with an End of Service Life before January 1, 2026, will not receive updates. HP outlines a dual-track approach for updates, with specific timelines for commercial PCs. Microsoft's Surface devices receive updates directly from Microsoft, while MSI categorizes guidance based on processor generation for its laptops. Acer emphasizes backing up the BitLocker recovery key and provides a model table for confirmed BIOS release dates. Samsung confirms that all PCs running Windows 10 or 11 will function normally post-expiration, but security updates will cease. LG has released a guide for checking BIOS updates for its PCs. To verify if a PC has the 2023 certificates, users can check the Secure Boot section in Windows Security. A green checkmark indicates successful application, while yellow or red icons indicate pending updates or incompatibility. Microsoft has pushed the certificates to all eligible devices as of June 2026.
Search