Windows system

Tech Optimizer
September 12, 2026
If you hold Microsoft 365 E5, you already have access to Microsoft Defender for Endpoint, which provides enterprise-grade endpoint protection at no additional cost. For organizations without a dedicated security specialist, Sophos is recommended. CrowdStrike is suitable for those with a mature Security Operations Center (SOC) and sufficient budget. Other options include SentinelOne for mid-sized organizations needing automation, ESET for older hardware and virtual desktops, Avast Business for very small businesses without IT staff, VIPRE for budget-conscious organizations, and Expel for tool-agnostic managed detection and response. It is essential to assess your organization's current situation honestly when evaluating endpoint protection options. Antivirus and EDR are now essentially the same agent, and organizations should inquire about update staging processes and review independent tests for protection rates. Coverage for servers and Linux environments is often overlooked but crucial, as Linux servers are prime targets for ransomware. Key recommendations include: - Microsoft Defender for Endpoint for organizations already on Microsoft 365 E5. - Sophos for organizations with 25-500 staff relying on IT generalists. - CrowdStrike for enterprises with a well-funded security operations function. - SentinelOne for mid-sized organizations needing autonomous operation. - ESET for organizations with older hardware or virtual desktop infrastructure. - Avast Business for micro and small businesses. - VIPRE for budget-conscious organizations. - Expel for those seeking managed detection across various environments. During deployment, avoid running two real-time agents simultaneously, ensure prevention features are activated, and test on line-of-business applications first. Verify update staging and rollback procedures with vendors, and confirm whether Microsoft licensing covers your needs to avoid unnecessary purchases.
Tech Optimizer
September 10, 2026
If you hold Microsoft 365 E5, you have access to Microsoft Defender for Endpoint, which provides enterprise-grade endpoint protection at no additional cost. For organizations without a dedicated security specialist, Sophos is recommended for its user-friendly platform. CrowdStrike is suggested for those with a mature Security Operations Center (SOC) and sufficient budget. Other options include SentinelOne for mid-sized organizations needing automation, ESET for older hardware and virtual desktops, Avast Business for very small businesses, VIPRE for budget-conscious mixed estates, and Expel for tool-agnostic managed detection and response. Antivirus and EDR are now unified under a single agent, and organizations should inquire about update staging processes to avoid issues like those experienced in July 2024 with a major vendor's faulty content update. Independent tests from organizations like AV-Comparatives and AV-TEST are crucial for evaluating protection rates and false positives. Linux servers require attention as they are often targeted by ransomware. When deploying endpoint protection, avoid running two real-time agents simultaneously, activate prevention features promptly, and test deployments on critical applications first. Organizations should confirm their Microsoft licensing covers necessary features and ensure there is a plan for responding to alerts. Common pitfalls include neglecting identity management and failing to test response workflows before incidents occur.
BetaBeacon
August 18, 2026
- Ads: No - Funding model: Open-source community RetroArch - Base price: Free - Optional paid tier: None - Ads: No - Funding model: Open-source community Winlator - Base price: Free - Optional paid tier: None - Ads: No - Funding model: Donation-funded DraStic - Base price: Free - Optional paid tier: None - Ads: No - Funding model: None public
Winsage
August 17, 2026
Microsoft is removing the Windows Management Instrumentation Command-line (WMIC) from Windows 11 to enhance security by eliminating a tool that has been exploited by malware and ransomware. WMIC will not be included in Windows 11 versions 24H2, 25H2, and 26H2, with complete removal scheduled for the August 2026 Patch Tuesday update. The decision to remove WMIC is based on the availability of more secure alternatives like PowerShell. WMIC has been a vector for attacks, allowing threat actors to disable antivirus solutions and access sensitive data. Microsoft has phased out WMIC since 2021, encouraging users to transition to modern tools while continuing to support the underlying Windows Management Instrumentation (WMI) infrastructure.
Winsage
August 12, 2026
A survey by the Browser Choice Alliance involving 2,000 U.S. adults reveals significant dissatisfaction with Microsoft's Edge browser. Key findings include: - 86% of respondents believe they should control their default browser, and 80% want a "one-click browser default" option. - 26% currently have Edge as their default browser, but only 19% would choose it if given a free choice. - 72% of those who tried to change their default browser in the past two years faced obstacles, such as Edge being recommended or links opening in Edge. - 29% reported that Windows system updates changed their browser preferences. - Among adults aged 65 and older, 44% found changing their default browser complex, and 61% lacked confidence in the process. - 14% of respondents believe users should not have the ability to choose their default browser. - Microsoft has made changes to enhance user choice only within the EU, ignoring global opportunities. - Tools like MSEdgeRedirect and EdgeDeflector aimed at redirecting links to preferred browsers are now ineffective or limited. - Microsoft announced the discontinuation of support for MV2 extensions, affecting tools like uBlock Origin.
Winsage
August 12, 2026
Microsoft released a patch for a zero-day vulnerability, CVE-2026-68820, which is being exploited by cybercriminals, specifically the North Korean hacking group Lazarus. This vulnerability allows unauthorized attackers to elevate their privileges locally, posing a significant risk to affected systems. The August 2026 Patch Tuesday update addressed 421 vulnerabilities, including three zero-days, with CVE-2026-68820 being the only one confirmed to be actively exploited. The vulnerability's impacts on confidentiality, integrity, and availability are rated as High. Users of Microsoft Windows 10, Windows 11, and various versions of Windows Server should prioritize deploying the patch for this vulnerability.
Winsage
August 5, 2026
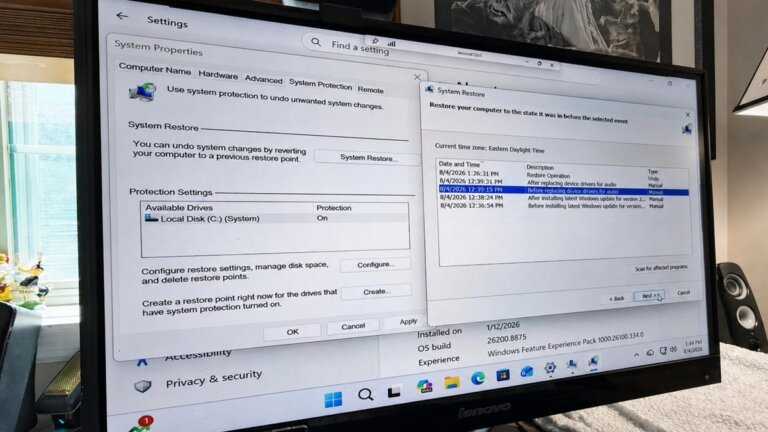
System Restore is a recovery feature in Windows that allows users to revert their systems to a previous state by creating snapshots of the current configuration. It captures crucial system components such as Windows system files, Registry settings, device drivers, and installed applications, but does not back up personal files. Windows automatically generates restore points during significant events or after a week without new points, and users can manually create them before making substantial changes. Restore points occupy hard drive space, and the oldest points are deleted when storage is full. To use System Restore, users can configure it in the System Properties window, create restore points, view and select restore points, preview changes, and initiate the restoration process. After restoration, the PC reboots, and users should check if issues are resolved.
Search