Windows Utilities

Winsage
September 28, 2026
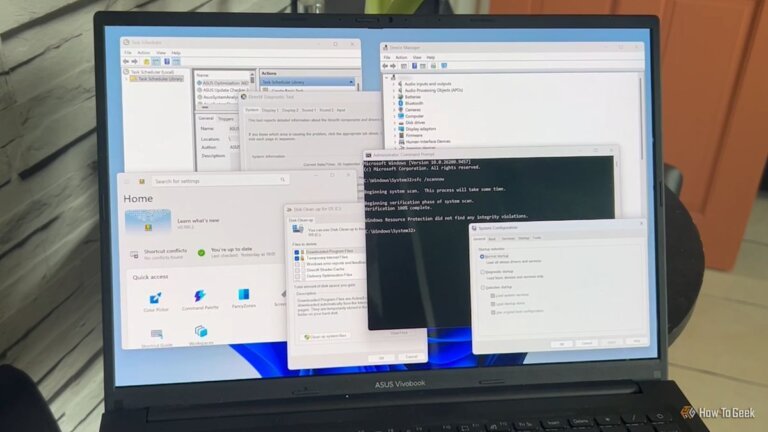
Microsoft PowerToys originated during the development of Windows 95 as small programs created by engineers to test concepts and ease workloads. The first collection of PowerToys included tools like FindX, Send To X, and Tweak UI. System Configuration (MSConfig) helps isolate configuration and startup issues by allowing selective loading of services and startup components, remaining useful despite modern management shifting to Task Manager. Disk Cleanup was launched with Windows 98 to help users reclaim disk space, featuring commands that allow saving cleanup profiles, a functionality that persists in Windows 11. Task Scheduler, introduced in 1995 as System Agent in the Microsoft Plus! pack for Windows 95, automates tasks based on specific triggers. System File Checker (SFC), dating back to Windows 98, scans and repairs protected Windows resources, evolving from a graphical utility to a command-line tool. Device Manager provides an expandable tree of hardware components and reflects advancements in Microsoft's Plug and Play system from Windows 95, continuing to assist users in hardware inspection and troubleshooting. The DirectX Diagnostic Tool (DxDiag) was created for gamers in the late '90s to examine hardware and software configurations related to DirectX and remains available in Windows 11.
Tech Optimizer
September 22, 2026
LastPass has identified a sophisticated scheme targeting users of its Authenticator app, involving SEO poisoning and deceptive GitHub pages that distribute malicious ZIP files disguised as legitimate software. Users searching for "LastPass Authenticator download" may encounter these counterfeit pages, which redirect them to a malicious server delivering a ZIP file containing vsdbg.exe and vsdbg.dll. The executable is a legitimate Microsoft debugging tool exploited to execute the malicious DLL through DLL sideloading, allowing the malware to run undetected. Named Rapuncel by security researchers from Delphos, this malware is undetectable by antivirus engines and targets a hardcoded list of 145 antivirus and endpoint security products, disabling them upon detection. Rapuncel harvests sensitive information, including saved passwords from over 25 web browsers, cryptocurrency wallet files from more than 30 applications, and session tokens from platforms like Discord and Steam. It also captures screenshots and compiles a profile of the infected system, uploading the stolen data to an attacker-controlled server. The malware includes a kernel driver that intercepts web traffic, allowing for advertisement injection and search result manipulation. This campaign has been active for several months, with LastPass vaults remaining unaffected. Users are advised to download applications only from trusted sources. Rapuncel establishes persistence on infected machines by installing itself as a Windows service that starts with the system and terminates activated security products. Removing the kernel driver requires booting into Safe Mode or using external recovery tools, as standard Windows utilities cannot eliminate software operating at that level.
Winsage
June 30, 2026
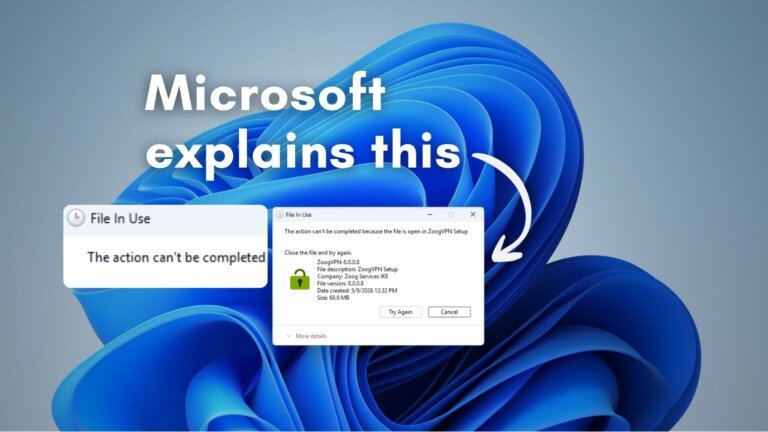
The 'file in use' error in Windows indicates that a file is currently being accessed by a program, preventing deletion or renaming to avoid data corruption. This error can persist even after closing an application due to reasons such as antivirus software scanning the file, network references from other devices, or files loaded as Dynamic Link Libraries (DLLs) that remain in memory. To identify the process causing the error, Mark Russinovich developed the command-line tool Handle, which shows all open file handles, and Process Explorer, which provides a graphical interface to find and manage these handles. Microsoft is integrating Sysinternals tools into PowerToys for easier access, including the File Locksmith tool that allows users to unlock files directly. A recommended workaround for the error is to rename the file instead of deleting it, as Windows permits renaming even when a file is open.
Tech Optimizer
February 16, 2026
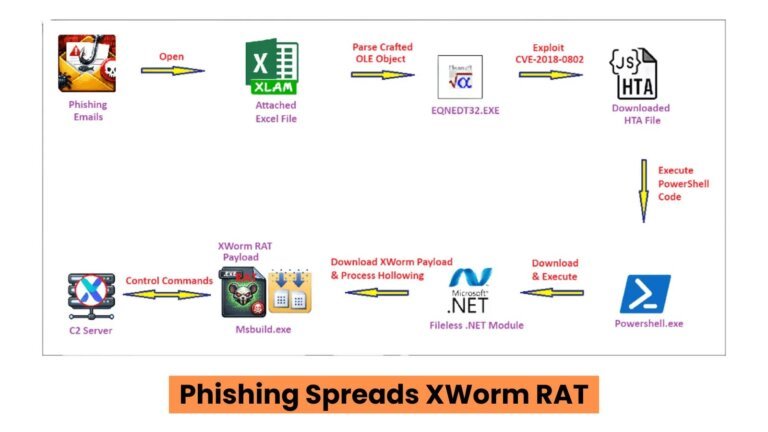
A cyber-espionage campaign is utilizing the XWorm Remote Access Trojan (RAT) to infiltrate systems via phishing emails and a Microsoft Office vulnerability (CVE-2018-0802). XWorm, first detected in 2022, allows attackers remote control over infected computers for surveillance and data theft. The campaign uses business-oriented phishing emails with malicious Excel attachments that exploit the vulnerability to execute a fileless attack. The malware connects to a command-and-control server, encrypting communications and transmitting system details. XWorm features a plugin architecture with over 50 modules for various malicious activities, including credential theft and DDoS attacks. Security experts highlight the ongoing risk of legacy software vulnerabilities and recommend patching outdated components.
Winsage
February 10, 2026
The Global Group has shifted to a local execution strategy for ransomware, complicating detection and response efforts. Their infection process begins when a user opens a shortcut file with a double extension (e.g., “Document.doc.lnk”), which appears as a legitimate document due to Windows' default settings that hide file extensions. The shortcut icon mimics that of a Microsoft Word file. When executed, the .lnk file activates Windows utilities like cms.exe and PowerShell to retrieve and execute the next-stage payload, effectively bypassing traditional security controls focused on malicious documents or executable attachments.
Winsage
October 30, 2025
Event Viewer is a built-in diagnostic tool in Windows that logs every event occurring on a PC, helping users troubleshoot performance issues. It categorizes logs into Application, System, Security, and Setup sections, allowing users to focus on relevant categories during troubleshooting. Events are classified as Critical, Error, Warning, and Information, with Critical events indicating potential sources of system crashes. Users can filter logs, research Event IDs, and utilize the Details section for deeper insights. Event Viewer can be paired with Reliability Monitor for a visual overview of system stability. Many third-party diagnostic tools also rely on data from Event Viewer, making it a valuable resource for addressing persistent errors.
Winsage
October 17, 2025
Light Switch is a new tool included in the PowerToys 0.95 update from Microsoft, allowing users to transition between light and dark modes based on the time of day. Users can set custom time frames for this transition and choose which components of the operating system will change modes. To use Light Switch, users must download PowerToys and ensure they have the latest version installed.
Search