zero-day exploit

Winsage
September 15, 2026
A spear-phishing campaign linked to the Chinese threat actor UTA0560 targeted various NGOs on September 1, 2026, exploiting recently patched vulnerabilities in Google Chrome and Microsoft Windows. The campaign utilized a malicious JavaScript backdoor called GRIMWEDGE, which was deployed through a multi-stage exploit chain that involved three vulnerabilities: CVE-2026-85046, CVE-2026-87491, and CVE-2026-85880. The attack began with spear-phishing emails that led recipients to a vulnerable U.S.-based university website, allowing attackers to redirect users to their infrastructure. The exploit chain enabled arbitrary code execution and facilitated the deployment of GRIMWEDGE, which is capable of host reconnaissance, file and process management, command execution, and payload delivery. The initial payload was an executable named "msgbox.exe," which extracted a legitimate Windows binary and a malicious DLL called "wsc.dll." This DLL initiated a sideloading chain and contacted a command-and-control server for further instructions. GRIMWEDGE allows for several commands, including system reconnaissance, directory listing, file deletion, and command execution in a hidden window. It lacks built-in persistence or lateral movement mechanisms but provides a foothold for further exploitation. Concurrently, another Chinese threat actor, JungleBamboo (APT31), used the same exploit chain to deploy a loader named SUPERSTOMP, which installs a credential-stealing Chrome extension called LONGTALE. The simultaneous use of the exploit chain by multiple actors suggests potential sharing or sale of the exploit, raising concerns about patch-gap vulnerabilities that pose risks for exploitation campaigns.
Winsage
August 13, 2026
Nightmare Eclipse has released a new zero-day exploit called ShieldBreak, which can bypass Microsoft's RoguePlanet patch (CVE-2026-50656) and allow attackers to gain SYSTEM privileges on fully patched Windows 10, Windows 11, and Windows Server systems. The exploit has been confirmed by security expert Kevin Beaumont, who provided detection methods for it. ShieldBreak is the tenth zero-day from Nightmare Eclipse since April and was released shortly after Microsoft's monthly Patch Tuesday. The exploit allows local privilege escalation and has a 100% success rate on the latest version of Windows 11 and Windows Server 2025, while Windows 10 remains vulnerable. Microsoft is aware of the vulnerability and is investigating it, emphasizing the importance of coordinated vulnerability disclosure. Previous exploits from Nightmare Eclipse include LegacyHive and GreatXML, with earlier vulnerabilities having been patched but recent ones still unaddressed. Microsoft had threatened legal action against Nightmare Eclipse in May but later reconsidered its approach to vulnerability disclosure.
Winsage
August 13, 2026
Security researcher Nightmare Eclipse has released a zero-day exploit named ShieldBreak that allows privilege escalation on Windows by targeting a vulnerability in Microsoft Defender. This exploit, designated as CVE-2026-50656, is categorized as a race condition vulnerability and affects the latest versions of Windows 11 and Windows Server 2025, with potential impacts on Windows 10. The exploit was disclosed on June 9, 2026, and Microsoft acknowledged the issue on June 16, rolling out fixes by July 9. The mechanics of ShieldBreak involve manipulating Defender’s scan path and executing a scheduled task to gain System-level privileges. Experts have noted differences between ShieldBreak and the previously known RoguePlanet exploit, emphasizing that ShieldBreak requires Defender to be active to function.
Tech Optimizer
July 27, 2026
Zero-day exploits are attacks that take advantage of previously unknown software vulnerabilities before a vendor can issue a patch. These exploits pose significant challenges because organizations cannot address vulnerabilities they are unaware of, and traditional security measures may not effectively identify them. Zero-day vulnerabilities are distinct from zero-day exploits; the former refers to the software flaw itself, while the latter is the method used by attackers to exploit that flaw. Zero-day exploits are particularly dangerous because they give attackers a temporary advantage, allowing them to compromise systems before defenders can respond. These exploits are commonly used in advanced attacks, including ransomware campaigns and espionage. The lifecycle of a zero-day exploit typically involves discovering a vulnerability, weaponizing it, delivering the exploit, executing malicious code, and achieving the attacker's objectives. Traditional antivirus solutions may not consistently prevent zero-day exploits, as they primarily focus on known threats. Endpoint Detection and Response (EDR) platforms provide visibility and detection but do not inherently prevent exploitation. Effective prevention strategies emphasize stopping the exploitation techniques themselves, rather than solely relying on detection. Memory-based attack prevention is a key approach, as all exploits must execute within memory. This method disrupts exploitation techniques and can protect against unknown vulnerabilities. Best practices for preventing zero-day exploits include reducing the attack surface, enforcing least privilege, maintaining aggressive patch management, strengthening identity security, deploying prevention-based endpoint protection, and maintaining a layered security strategy.
Winsage
June 30, 2026
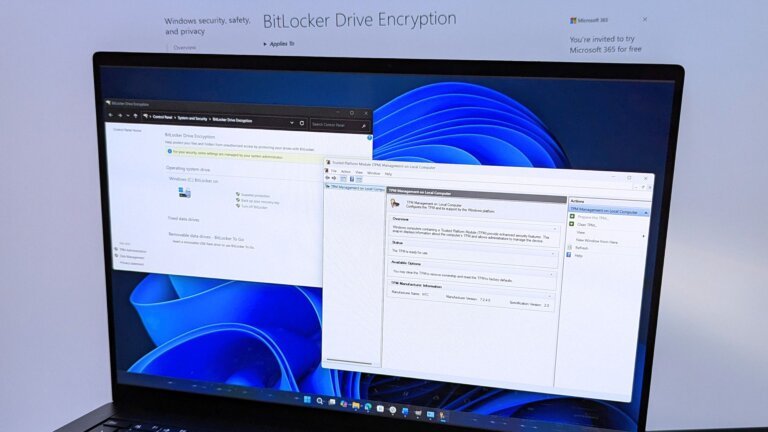
Security researcher Chaotic Eclipse, known as Nightmare-Eclipse, bypassed Windows 11's BitLocker security using a USB stick and claimed Microsoft intentionally included a backdoor in the feature. Microsoft responded by patching three zero-day exploits disclosed by Nightmare-Eclipse: YellowKey, GreenPlasma, and MiniPlasma, and is monitoring another exploit called RoguePlanet, cataloged as CVE-2026-50656. The RoguePlanet exploit is a race condition with varying success rates on different machines, achieving a 100% success rate on some devices. Microsoft acknowledged that while Windows 11's Defender is generally sufficient for most users, third-party tools can offer additional security features. Tensions between Nightmare-Eclipse and Microsoft have risen, with the company previously considering legal action but now indicating it will not pursue lawsuits against researchers sharing their findings.
Winsage
May 20, 2026
Microsoft is addressing a zero-day exploit known as YellowKey, identified as CVE-2026-45585, which allows attackers to bypass BitLocker security using a specially crafted USB device. Following the release of exploit code by a hacker named Chaotic Eclipse, Microsoft has issued urgent mitigation advice. Cybersecurity expert Neena Sharma recommends treating this as an active threat and suggests implementing compensating controls, such as restricting USB boot access, until a patch is available. Microsoft has provided guidance for users to protect their systems, including the recommendation to add a PIN to BitLocker protection to reduce the risk of exploitation. Detailed instructions for adding a PIN are included in the advisory. YellowKey has not yet been exploited in the wild but requires physical access to the device.
Search