accessibility

Winsage
September 19, 2026
Microsoft has released a modernized version of the Mouse Indicator in Windows 11 Insider Preview Build 26340.9502 on September 18, 2026. This update features a new animation that can be activated through Accessibility settings, allowing users to keep the indicator on until they press the Esc key. Users can choose to activate the Mouse Indicator with a single or double Ctrl press. The previous version displayed a simplistic circle around the pointer briefly, while the new version offers a smoother, more dynamic animation. The feature is currently available only in the Insider build for the Experimental channel, and users can enable it by navigating to Settings > Accessibility > Mouse pointer and touch > Mouse indicator.
AppWizard
September 19, 2026
Google has launched Android Bench 2.0, an upgraded benchmark for evaluating AI coding agents, which now includes 30 long-horizon tasks that can take human engineers days or weeks to complete. The best pass rate for these tasks is around 28%, down from approximately 91% in the previous version. The benchmark measures both pass rates and completion rates, acknowledging partial progress rather than just failures. It assesses various challenges, including app creation and feature integration, using a comprehensive scoring methodology that evaluates functionality, regression checks, and visual fidelity. AI models perform better with new code than with modifications to existing systems, facing challenges in runtime validation and cross-platform conversions. The current leaderboard shows OpenAI’s GPT-6 Astra leading with a 28% pass rate, while Gemini 3.8 Flash has an 8% pass rate. Developers using AI agents should be aware that while AI can generate significant portions of applications, further refinements will require human input. The benchmark is available on Google’s Android Bench leaderboard.
AppWizard
September 19, 2026
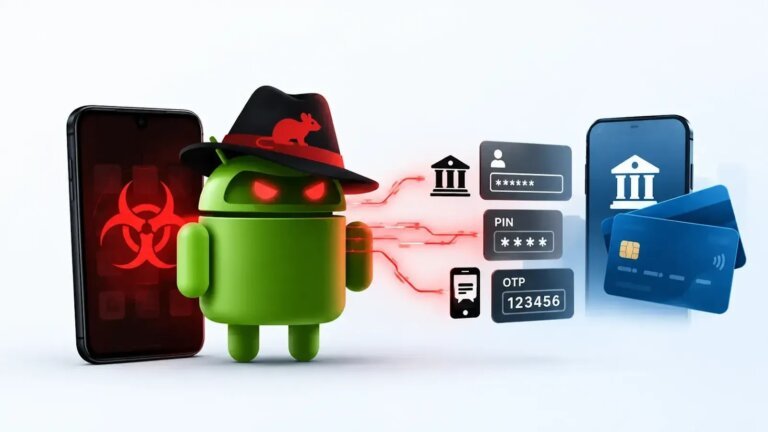
A new Android malware called RatHat has emerged, analyzed by researchers from Zimperium's zLabs. It spreads through deceptive smishing texts and malicious ads that lead users to counterfeit download pages for popular apps. Once installed, it manipulates Android's Accessibility Service to gain elevated access by enabling Wireless Debugging and retrieving authentication codes without user intervention. RatHat targets finance and banking apps to steal user IDs, passwords, and MFA codes, using techniques to obtain touch coordinates for PIN recovery. It can intercept SMS messages, gain limited control of the device, and reinstall itself. Users are advised against sideloading apps and granting unnecessary accessibility permissions. Google's Advanced Protection Mode and Malwarebytes for Android can help mitigate risks associated with RatHat.
AppWizard
September 19, 2026
Security researchers have identified an Android banking Trojan named RatHat, which utilizes artificial intelligence, accessibility features, and Android Debug Bridge (ADB) to steal financial credentials, PINs, and one-time passcodes. Unlike traditional malware, RatHat employs a live AI assistant that interacts with the Android accessibility tree, allowing it to make real-time decisions based on the victim's screen content. The infection typically starts with social-engineering tactics, leading victims to counterfeit download pages where they are tricked into sideloading a malicious APK. Once installed, RatHat prompts users to enable Android Accessibility Service permissions, which it exploits to navigate Developer Options and enable Wireless Debugging. This grants it shell-level ADB access, allowing it to bypass application sandbox restrictions. RatHat deploys two native binaries for executing commands and maintaining a connection to the attacker's infrastructure. It targets banking applications through credential-stealing overlays and can intercept SMS messages for transaction verification codes. Additionally, it can record touch coordinates to reconstruct PINs and unlock patterns. RatHat includes persistence mechanisms to restore itself after removal, and users are advised to perform a factory reset if they suspect compromise. To reduce infection risk, users should avoid sideloading apps from unknown links, deny unnecessary Accessibility Service requests, and refrain from enabling Developer Options or Wireless Debugging for unfamiliar applications.
AppWizard
September 19, 2026
ESG reporting standards are becoming increasingly important in mobile technology, affecting various aspects such as data management, material sourcing, energy consumption, privacy, supply chain dynamics, and product accountability. The lifecycle of mobile devices involves raw material sourcing, component manufacturing, device assembly, shipping, marketing, sales, updates, repairs, trade-ins, and disposal. Companies must understand ESG standards to create coherent sustainability narratives and may need to disclose supplier practices, carbon emissions, and governance documentation when partnering with larger firms. Consumers are now asking more questions about the longevity of software updates, repairability, data collection, packaging design, and the accountability of product creators. The rise of connected devices complicates ESG reporting due to extended product lifecycles and the need for ongoing software support. Companies should track product lifespan estimates, warranty data, repair trends, and update schedules to improve product quality and ESG reporting credibility. Emerging tech companies can start their ESG journey by cataloging product claims, consolidating evidence, designating ownership of records, and reviewing product lifecycle information. Global sustainability frameworks exist but may not align with consumer needs for straightforward product information. Successful mobile tech companies will need to bridge formal reporting requirements with accessible product-level communication. Trust and transparency in practices will increasingly influence consumer choices in mobile technology.
AppWizard
September 18, 2026
Cybersecurity experts have identified a new Android malware named RatHat, believed to be operated by Chinese threat actors. RatHat is distributed primarily through smishing and malvertising campaigns, leading users to deceptive download portals. It employs an automated multi-stage infection process and exploits Accessibility features along with a local ADB self-pairing mechanism to escape the Android application sandbox. The malware uses various anti-analysis techniques, including container tampering, manifest bombs, DEX bytecode poisoning, and dual string-encryption. RatHat's architecture consists of a malicious Android application, a Go agent, and an FRP reverse-proxy client, which together enable it to gain critical system permissions and perform various malicious activities such as credential capturing, screen recording, and SMS interception. Even if uninstalled, the malware retains shell access to the device, allowing attackers to reinstall it. RatHat can serialize the device's Accessibility tree to XML and communicate with a Generative AI assistant for tasks like screen coordinate determination and text extraction. The Go Agent, masquerading as a native library, exploits shell access to execute commands and establish a persistent connection to a command-and-control server via the FRP client. The C2 server can issue extensive commands to collect sensitive information, including SMS messages, credentials, files, and keystrokes, and RatHat also features a hardware-level keylogger.
AppWizard
September 18, 2026
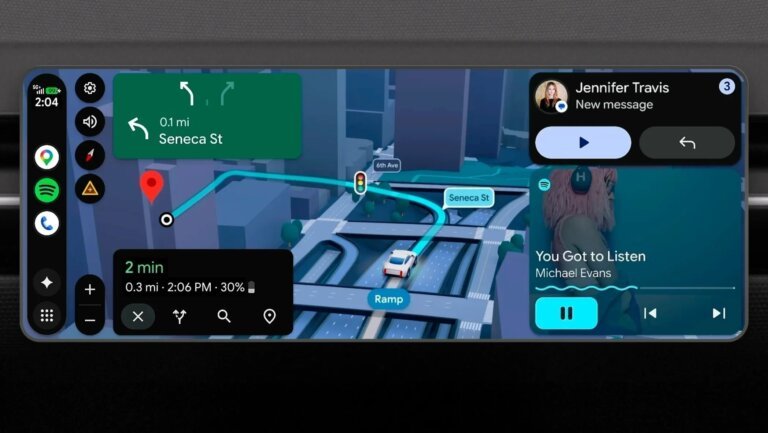
Gemini has launched on Android Auto, but user feedback has been largely negative. Google is working on improvements, including a new destination card in Google Maps that will utilize Gemini's AI to provide information about destinations, such as reviews, essential details, practical tips, and visuals. The user interface is still being optimized, and there is no guarantee that the feature will be finalized for public release. Users have reported issues with Gemini, including problems with making calls and sending texts, distractions from excessive chatter, and app crashes. The latest updates were noted in Android Auto version 17.8, which is still in development.
AppWizard
September 17, 2026
Security researchers at Zimperium have identified a new strain of Android malware called RatHat, which is linked to threat actors from China and is designed to steal sensitive credentials and banking information. RatHat infiltrates devices through phishing sites, malvertising, and SMS phishing (smishing), tricking users into downloading malicious Android package kits (APKs). The malware uses a dropper to activate its payload, which is hidden in encrypted assets, and employs techniques to bypass Android's security measures. RatHat consists of three main components: a malicious Android application, a Go agent (liblocal-service.so), and an FRP client (libmedia_codec.so). The app collects sensitive information such as banking credentials, notifications, 2FA codes, OTP keys, and screen inputs. It features a generative AI user interface-automation engine that communicates in Mandarin and can perform various tasks like determining screen coordinates and issuing navigation commands. The Go agent acts as a command-and-control executor, executing commands to bypass app-level security and manage system-level tasks. The FRP client maintains a secure reverse tunnel to the attacker's server, allowing ongoing remote access to the device. The architecture of RatHat demonstrates the inadequacy of traditional mobile security measures against such advanced threats.
Winsage
September 17, 2026
The most recognized Windows XP product key is FCKGW-RHQQ2-YXRKT-8TG6W-2B7Q8. Windows XP was released in two formats: Retail for consumers and Volume for Microsoft partners and OEMs. The Volume discs were not intended for the general public and were designed for mass installations without individual activation. The final CD version, Release to Manufacturing (RTM), was completed on August 24, 2001, two months before the official launch on October 25. A leak of the Volume image and its Volume License Key (VLK) is believed to have originated from a major OEM, possibly Dell or Intel, which was exploited by the pirate group Devils0wn, allowing broader access to Windows XP.
Search