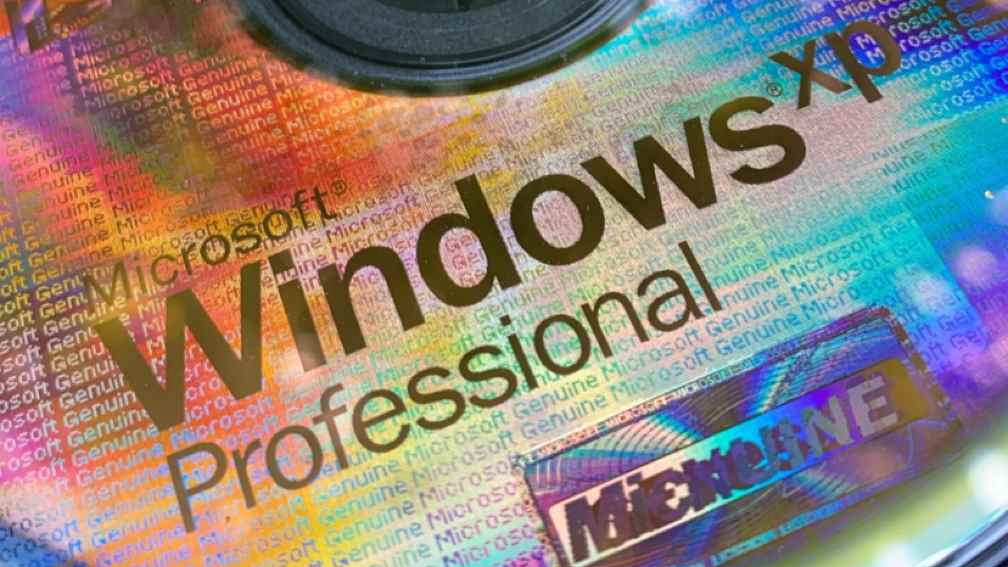
For those who navigated the digital landscape during the early 2000s, a particular string of characters likely resonates with nostalgia: FCKGW-RHQQ2-YXRKT-8TG6W-2B7Q8. This alphanumeric sequence is not merely a random assortment but rather the most recognized Windows XP product key, enabling countless users to install and operate the operating system with just a single CD. The question lingers: how did Microsoft allow such a significant vulnerability in its copy protection? Insights from former engineer Dave Plummer shed light on this intriguing chapter of tech history.
The Dual Nature of Windows XP Media
Windows XP was released in two distinct formats: Retail and Volume. The Retail version catered to everyday consumers purchasing the OS from stores, while the Volume edition was tailored for Microsoft partners and OEMs, designed for mass installations across numerous machines without the need for individual activation at each setup.
Interestingly, the Volume discs were not intended for the general public. These enterprise-only versions were meant to streamline the installation process for businesses. The final iteration of the CD, known as Release to Manufacturing (RTM), was completed on August 24, 2001, a full two months prior to its official launch on October 25. This early availability allowed OEMs and partners to prepare their products with Windows XP pre-installed.
The Leak That Changed Everything
Plummer reveals that access to the Volume image and its corresponding Volume License Key (VLK) was limited to a select few organizations. He speculates that the leak originated from a major OEM, possibly Dell or Intel, which inadvertently made the Volume media and key available before the official release. This leak was swiftly capitalized on by the pirate group Devils0wn, who disseminated it online, allowing a wider audience to experience Windows XP without the usual restrictions.
Such events highlight the unpredictable nature of software distribution and the challenges companies face in safeguarding their products against unauthorized access. The legacy of Windows XP, marked by both its widespread adoption and the controversies surrounding its activation, continues to influence discussions about software security and user accessibility today.