analysts

Tech Optimizer
September 12, 2026
If you hold Microsoft 365 E5, you already have access to Microsoft Defender for Endpoint, which provides enterprise-grade endpoint protection at no additional cost. For organizations without a dedicated security specialist, Sophos is recommended. CrowdStrike is suitable for those with a mature Security Operations Center (SOC) and sufficient budget. Other options include SentinelOne for mid-sized organizations needing automation, ESET for older hardware and virtual desktops, Avast Business for very small businesses without IT staff, VIPRE for budget-conscious organizations, and Expel for tool-agnostic managed detection and response. It is essential to assess your organization's current situation honestly when evaluating endpoint protection options. Antivirus and EDR are now essentially the same agent, and organizations should inquire about update staging processes and review independent tests for protection rates. Coverage for servers and Linux environments is often overlooked but crucial, as Linux servers are prime targets for ransomware. Key recommendations include: - Microsoft Defender for Endpoint for organizations already on Microsoft 365 E5. - Sophos for organizations with 25-500 staff relying on IT generalists. - CrowdStrike for enterprises with a well-funded security operations function. - SentinelOne for mid-sized organizations needing autonomous operation. - ESET for organizations with older hardware or virtual desktop infrastructure. - Avast Business for micro and small businesses. - VIPRE for budget-conscious organizations. - Expel for those seeking managed detection across various environments. During deployment, avoid running two real-time agents simultaneously, ensure prevention features are activated, and test on line-of-business applications first. Verify update staging and rollback procedures with vendors, and confirm whether Microsoft licensing covers your needs to avoid unnecessary purchases.
AppWizard
September 11, 2026
The Cybersecurity and Infrastructure Security Agency (CISA) warned of a critical vulnerability in NetScaler, identified as CVE-2026-19490, with a CVSS score of 9.3, which has been exploited and affects all NetScaler ADC and Gateway appliances. Citrix has patched this vulnerability as of August 19. AdaptHealth reported a data breach affecting over 4.1 million individuals, compromising personal, health, and insurance information, but not Social Security numbers or financial data. A new strain of Android malware, MantaxOtax, attributed to Indonesian threat actors, combines ransomware and spyware, stealing sensitive information and affecting older Android versions. The Gigabud banking trojan has evolved to evade detection by installing a secondary app that hides the malicious application. CISA acting director Nick Andersen emphasized the need for swift adaptation to cybersecurity threats and highlighted staffing improvements within CISA. Russian e-commerce giant Wildberries experienced disruptions from a DDoS attack affecting payments to sellers, following claims of a cyber operation by Ukraine's military intelligence. McKesson faced a cyberattack exposing sensitive data of 6.4 million individuals, with the ShinyHunters group releasing this data after a failed extortion attempt. IDScan confirmed a data breach affecting 150 million individuals, resulting in the theft of personally identifiable information and government-issued documents.
AppWizard
September 11, 2026
Amazon has secured £4.25 billion in a borrowing initiative in London, aimed at enhancing its cloud services division, Amazon Web Services (AWS), and advancing its artificial intelligence initiatives. The company's long-term debt now stands at £9.1 billion. This move raises questions about the capacity of the US debt market to absorb large-scale borrowings and reflects a strategic choice to diversify funding sources. The funds will likely be directed towards enhancing AWS and AI capabilities, signaling confidence in Amazon's growth trajectory despite rising debt levels.
Tech Optimizer
September 10, 2026
If an organization holds Microsoft 365 E5, it already has access to Microsoft Defender for Endpoint. For organizations without a dedicated security specialist, Sophos is recommended for its user-friendly management. CrowdStrike is preferred for those with a mature Security Operations Center (SOC) and sufficient budget. The choice of endpoint protection depends on specific organizational needs. Business endpoint protection integrates various technologies to defend against malware and attacks on devices. Organizations should assess their current situation before selecting a solution. Key recommendations include: - Microsoft Defender for Endpoint for organizations already using Microsoft 365 E5. - Sophos for organizations with 25-500 staff relying on IT generalists. - CrowdStrike for enterprises with a funded SOC. - SentinelOne for mid-sized organizations needing automation. - ESET for those with older hardware or virtual desktops. - Avast Business for very small businesses lacking IT staff. - VIPRE for budget-conscious organizations needing straightforward coverage. - Expel for organizations wanting managed detection across diverse environments. Organizations should avoid running multiple real-time agents simultaneously and ensure prevention features are activated. Testing should prioritize line-of-business applications, and rollout procedures should be defined before going live. It’s essential to verify update staging and rollback procedures with vendors and confirm existing licenses to avoid unnecessary purchases.
Tech Optimizer
September 10, 2026
If you hold Microsoft 365 E5, you have access to Microsoft Defender for Endpoint, which provides enterprise-grade endpoint protection at no additional cost. For organizations without a dedicated security specialist, Sophos is recommended for its user-friendly platform. CrowdStrike is suggested for those with a mature Security Operations Center (SOC) and sufficient budget. Other options include SentinelOne for mid-sized organizations needing automation, ESET for older hardware and virtual desktops, Avast Business for very small businesses, VIPRE for budget-conscious mixed estates, and Expel for tool-agnostic managed detection and response. Antivirus and EDR are now unified under a single agent, and organizations should inquire about update staging processes to avoid issues like those experienced in July 2024 with a major vendor's faulty content update. Independent tests from organizations like AV-Comparatives and AV-TEST are crucial for evaluating protection rates and false positives. Linux servers require attention as they are often targeted by ransomware. When deploying endpoint protection, avoid running two real-time agents simultaneously, activate prevention features promptly, and test deployments on critical applications first. Organizations should confirm their Microsoft licensing covers necessary features and ensure there is a plan for responding to alerts. Common pitfalls include neglecting identity management and failing to test response workflows before incidents occur.
Tech Optimizer
September 7, 2026
Endpoint detection and response (EDR) continuously records process, file, registry, and network activity on endpoints, applying behavioral analytics to identify attacker techniques while providing tools for investigation and containment. Several EDR platforms have emerged, each catering to different organizational needs: 1. CrowdStrike: Best overall for its rich telemetry and elite threat intelligence. 2. SentinelOne: Best for autonomous response, featuring strong containment and rollback capabilities. 3. Microsoft Defender for Endpoint: Best value for organizations already using Microsoft 365 E5. 4. Palo Alto Cortex XDR: Best for native data fusion across endpoint, network, and cloud telemetry. 5. Sophos: Best for generalist IT teams due to its user-friendly interface. 6. Trend Micro: Best for server and workload coverage, focusing on cloud and hybrid environments. 7. Bitdefender: Best mid-market value with strong detection capabilities at an accessible price. 8. Trellix: Best for organizations already using Trellix products, offering integrated solutions. 9. Huntress Managed EDR: Best for managed endpoint security, ideal for teams lacking full staffing. 10. Cisco Secure Endpoint: Best for Cisco environments, integrating well with Cisco security solutions. Key differentiators among these platforms include the analyst burden, alert management efficiency, and the impact of retention policies on investigation quality. The evaluation of EDR solutions should consider detection depth, response capabilities, operational costs, and the specific needs of the organization.
Winsage
September 7, 2026
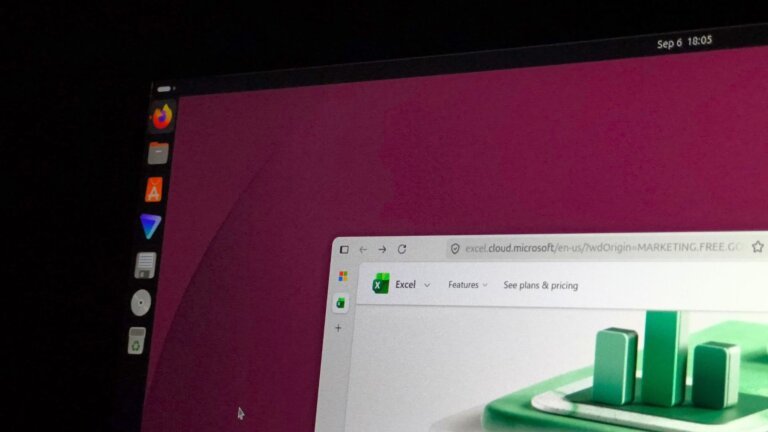
Omarchy is a Linux distribution created by David Heinemeier Hansson (DHH), designed for developers and creators, based on Arch Linux. DHH has challenged Microsoft to develop native Office applications for Linux, highlighting that while Microsoft 365's web version is available, Linux users only access about 90% of the functionality compared to Windows users. Microsoft’s revenue from Windows has decreased by 7% year-over-year, while Microsoft 365 Commercial cloud revenue has grown by 14%, and Azure by 43%. Windows now accounts for only 5% of Microsoft's total revenue, indicating a shift towards cloud services. Microsoft has launched Edge for Linux and supports tools like VS Code and PowerShell on the platform. The web version of Office lacks features found in the desktop version, affecting usability for professionals. Despite Linux's growing interest, particularly through the Windows Subsystem for Linux (WSL), it may not be enough to prompt Microsoft to prioritize a native Office port. DHH's Omarchy aims to create a user-friendly Linux experience rather than convert Windows users.
Winsage
September 3, 2026
A prominent company has unveiled new products focusing on user experience, incorporating consumer feedback. Key features include enhanced connectivity, sustainability initiatives using eco-friendly materials, and intuitive interfaces for ease of use. Initial reactions from consumers and industry experts are positive, indicating a potential shift in consumer preferences. The company's emphasis on innovation and sustainability may enhance brand loyalty and attract environmentally conscious consumers.
Search