attack

AppWizard
September 21, 2026
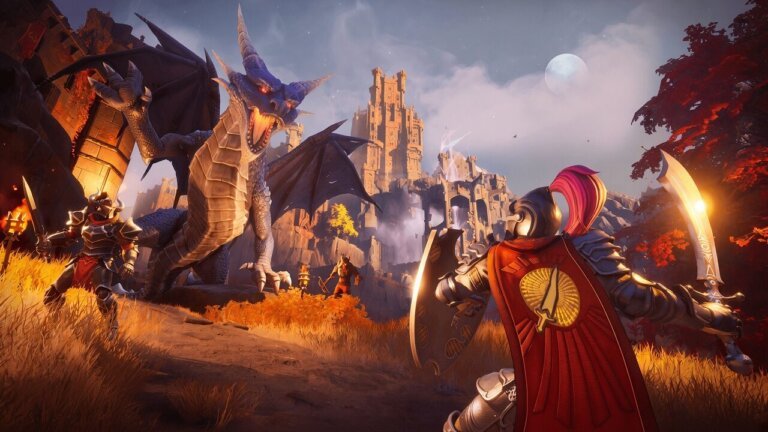
RuneScape: Dragonwilds introduces players to the new continent of Ashenfall, where they face the Dragon Queen Kuldra amidst a significant dragon threat. The game features a new biome called the Scorned Wilderness and a raid-style dungeon, requiring 40 to 60 hours of gameplay to complete its story content. It includes a sophisticated crafting system that allows for extensive customization of the game world. The combat system has been modernized, incorporating various weapon types and a nuanced parrying system, while the magic system offers unique runes that alter spell effects. Players experience skill progression through the use of tools or weapons, but the early game lacks healing potions, making it challenging. The game encourages exploration with a robust crafting system and in-game mounts, as well as the ability to create travel routes using loadstone teleporter panels. It also features dungeons with platforming elements and diverse enemy encounters. RuneScape: Dragonwilds supports full crossplay for consoles and has a roadmap for future updates.
Tech Optimizer
September 21, 2026
More than 5,400 websites across over 2,200 organizations have been compromised to propagate malware, primarily affecting small businesses like clinics and online retailers. The attack mechanism involves malicious code that triggers a deceptive CAPTCHA, instructing users to execute commands that can download malware. Attackers are using the BNB Smart Chain test network to store instructions, making it harder for investigators to shut down operations. A newer variant of the attack uses WebRTC technology to establish encrypted connections for delivering additional malicious code. To protect against these threats, users should avoid pasting commands from websites, be suspicious of unusual CAPTCHA instructions, use strong antivirus protection, keep systems updated, take action if commands are executed, and small business owners should regularly verify their website's integrity.
AppWizard
September 19, 2026
A new Android malware called RatHat has emerged, analyzed by researchers from Zimperium's zLabs. It spreads through deceptive smishing texts and malicious ads that lead users to counterfeit download pages for popular apps. Once installed, it manipulates Android's Accessibility Service to gain elevated access by enabling Wireless Debugging and retrieving authentication codes without user intervention. RatHat targets finance and banking apps to steal user IDs, passwords, and MFA codes, using techniques to obtain touch coordinates for PIN recovery. It can intercept SMS messages, gain limited control of the device, and reinstall itself. Users are advised against sideloading apps and granting unnecessary accessibility permissions. Google's Advanced Protection Mode and Malwarebytes for Android can help mitigate risks associated with RatHat.
AppWizard
September 18, 2026
Cybersecurity experts have identified a new Android malware named RatHat, believed to be operated by Chinese threat actors. RatHat is distributed primarily through smishing and malvertising campaigns, leading users to deceptive download portals. It employs an automated multi-stage infection process and exploits Accessibility features along with a local ADB self-pairing mechanism to escape the Android application sandbox. The malware uses various anti-analysis techniques, including container tampering, manifest bombs, DEX bytecode poisoning, and dual string-encryption. RatHat's architecture consists of a malicious Android application, a Go agent, and an FRP reverse-proxy client, which together enable it to gain critical system permissions and perform various malicious activities such as credential capturing, screen recording, and SMS interception. Even if uninstalled, the malware retains shell access to the device, allowing attackers to reinstall it. RatHat can serialize the device's Accessibility tree to XML and communicate with a Generative AI assistant for tasks like screen coordinate determination and text extraction. The Go Agent, masquerading as a native library, exploits shell access to execute commands and establish a persistent connection to a command-and-control server via the FRP client. The C2 server can issue extensive commands to collect sensitive information, including SMS messages, credentials, files, and keystrokes, and RatHat also features a hardware-level keylogger.
BetaBeacon
September 17, 2026
- Mobile version of Dome Keeper, a popular mining survival game, is in the works - Pre-registration is open on Google Play and pre-orders are available on the App Store for 899 rubles - Dome Keeper involves balancing resource extraction and defense against alien attacks - Players can enhance the dome, upgrade mining equipment, and increase movement speed with materials found - Procedurally generated maps offer a unique experience with each new run - Dome Keeper was originally released on Steam in 2022 and has sold over a million copies by October 2024
AppWizard
September 15, 2026
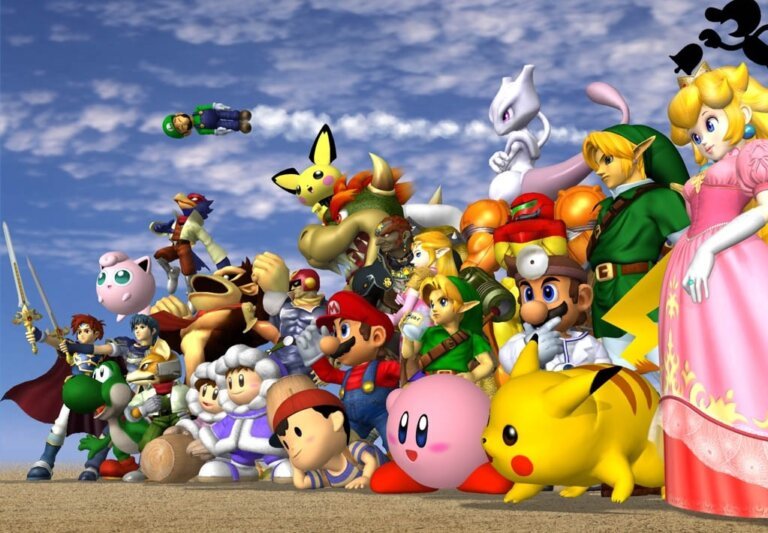
An unofficial PC port of the Nintendo GameCube game Super Smash Bros. Melee has been released. The game, originally launched in 2001, features a unique damage system, various attack types, and diverse stages. It includes several game modes such as Classic Mode, Adventure Mode, and Event Matches, with unlockable characters and content. The PC version supports keyboard and gamepad inputs, allows for resolution adjustments and visual customizations, but lacks online play and widescreen support. Users need to provide their own ROM to play. This release is part of a trend of unofficial PC ports of classic games, including titles like Super Mario 64 and The Legend of Zelda: Ocarina of Time.
Winsage
September 15, 2026
A spear-phishing campaign linked to the Chinese threat actor UTA0560 targeted various NGOs on September 1, 2026, exploiting recently patched vulnerabilities in Google Chrome and Microsoft Windows. The campaign utilized a malicious JavaScript backdoor called GRIMWEDGE, which was deployed through a multi-stage exploit chain that involved three vulnerabilities: CVE-2026-85046, CVE-2026-87491, and CVE-2026-85880. The attack began with spear-phishing emails that led recipients to a vulnerable U.S.-based university website, allowing attackers to redirect users to their infrastructure. The exploit chain enabled arbitrary code execution and facilitated the deployment of GRIMWEDGE, which is capable of host reconnaissance, file and process management, command execution, and payload delivery. The initial payload was an executable named "msgbox.exe," which extracted a legitimate Windows binary and a malicious DLL called "wsc.dll." This DLL initiated a sideloading chain and contacted a command-and-control server for further instructions. GRIMWEDGE allows for several commands, including system reconnaissance, directory listing, file deletion, and command execution in a hidden window. It lacks built-in persistence or lateral movement mechanisms but provides a foothold for further exploitation. Concurrently, another Chinese threat actor, JungleBamboo (APT31), used the same exploit chain to deploy a loader named SUPERSTOMP, which installs a credential-stealing Chrome extension called LONGTALE. The simultaneous use of the exploit chain by multiple actors suggests potential sharing or sale of the exploit, raising concerns about patch-gap vulnerabilities that pose risks for exploitation campaigns.
Search